The Insider Threat: How Internal Actors Are Becoming Crypto’s Weakest Link
A report reveals that the attacker was persistent and used many different methods. The mole inserted backdoors in engineering workstations while working at the firm, which went undetected for weeks. They also used social...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
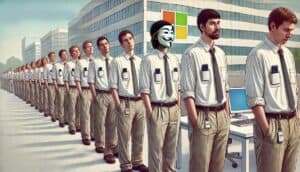
A report reveals that the attacker was persistent and used many different methods. The mole inserted backdoors in engineering workstations while working at the firm, which went undetected for weeks. They also used social engineering, supply chain attacks. The incident is reminiscent of another recent ‘inside job’ at Coinbase where helpdesk staff sold highly confidential customer data to criminal gangs. It further underscores a disturbing truth: even well-audited systems can be undermined from within.
Insiders are emerging as a potential existential threat to crypto infrastructure. These are developers, employees, and even third-party contractors who have privileged access to systems and who can exploit that access for malicious gain.
Are Your Developers the Weakest Link?Insider attacks often evade traditional security measures. Their method of entry relies on being handed the keys to the castle. Developers and auditors have access to production environments, commit privileges, and real-time knowledge of system weaknesses.
Their method of entry relies on being handed the keys to the castle, not through brute-force hacks or zero-day exploits, but by securing legitimate access as trusted team members. Once inside, these insiders can move laterally through internal systems, plant backdoors, exfiltrate sensitive keys, or manipulate smart contract deployments, all under the guise of normal developer activity. This makes them far harder to detect than external attackers and significantly increases the potential for long-term, undetected compromise.
In many ways, trust in team members has become a security liability. And in a pseudonymous industry where open-source contributors may never meet in person, the challenge of verifying intent and identity is especially complex.
North Korea’s Cyber Army and the Infiltration of Web3 TeamsThe most alarming trend subset of the trend is the state-sponsored weaponization of remote work. According to U.S. government reports and cybersecurity firm DTEX, North Korea has deployed sleeper agents into Web3 organizations by posing as freelance developers and IT workers. These operatives use fake identities, convincing GitHub contributions, and professional LinkedIn profiles to secure contracts at crypto startups and DAOs.
Once inside, they either steal sensitive credentials directly or insert backdoors into the codebase. These attacks are extremely difficult to detect, especially in globally distributed teams with minimal in-person verification.
The FBI, Treasury, and Department of Justice have issued joint advisories urging crypto projects to vet remote workers more rigorously. As of late 2024, more than US$1 billion in crypto thefts have been linked to North Korean state-sponsored actors.
Is the Pseudonymous Culture of Crypto a Security Risk?Security isn’t just about code, it’s about people. One of crypto’s foundational values is the ability to operate pseudonymously; the industry is built around a respect for individual privacy. This feature, however, makes traditional HR and security practices difficult to apply. While pseudonymity has empowered whistleblowers, open-source contributors, and communities in oppressive regions, it also opens the door to abuse.
Are the values of decentralization compatible with the trust models required to build secure systems? A potential solution is a hybrid approach, where pseudonymous contributors operate in sandboxed roles, while core infrastructure is limited to verified team members.
ConclusionThe Bedrock exploit and the broader trend of state-linked suggest that the industry can no longer rely solely on external audits and bug bounties. In a sector built on transparency and code, human trust may be the most straightforward attack surface.
For Web3 to scale securely, it must grapple with an uncomfortable truth: the most dangerous threat may not be on the outside looking in, but already inside the walls.
Why this matters
This altcoin story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on Brave New CoinRelated market context
Ledger’s crypto wallet implant scare triggers Trezor reseller crackdown as security fears spread
Trezor is cutting authorized resellers after a hardware-implant attack against rival Ledger exposed vulnerabilities in cryptocurre...
Bitcoin’s quantum-safe protection gets 82% cheaper as researchers race to secure 6 million exposed BTC
Researchers have cut the estimated computing cost of a specialized quantum-safe Bitcoin transaction by 82% to $59. Data from the Q...

Bybit Expands Beyond Crypto as CEO Outlines Next Phase of Financial Platform
Dubai, United Arab Emirates, October 13th, 2026, Chainwire Bybit Co-founder and CEO Ben Zhou has outlined the latest stage of the...
Cardano Foundation research finds big reserves don’t guarantee proof-of-stake security
Cardano's findings highlight the need for dynamic security strategies in proof-of-stake systems, emphasizing adaptability over res...
$694M in crypto long positions liquidated in 24 hours: WhaleInsider
The liquidation highlights potential market instability, influencing future crypto sentiment and price expectations amid regulator...
Ripple and Privy bring embedded XRPL wallets to app developers
The integration of embedded XRPL wallets could significantly enhance app usability, streamline crypto transactions, and boost AI-d...