dYdX v3 compromised in an apparent DNS attack
An attacker appears to have installed a token-draining program on the official domain for dYdX version 3.0.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.

An attacker appears to have installed a token-draining program on the official domain for dYdX version 3.0.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context
Electrum Fixes Bitcoin Wallet Flaw That Could Turn A Fee Bump Into Theft
Electrum disclosed a wallet flaw on October 24 that could turn a Bitcoin fee adjustment into an unintended payment. Its advisory e...
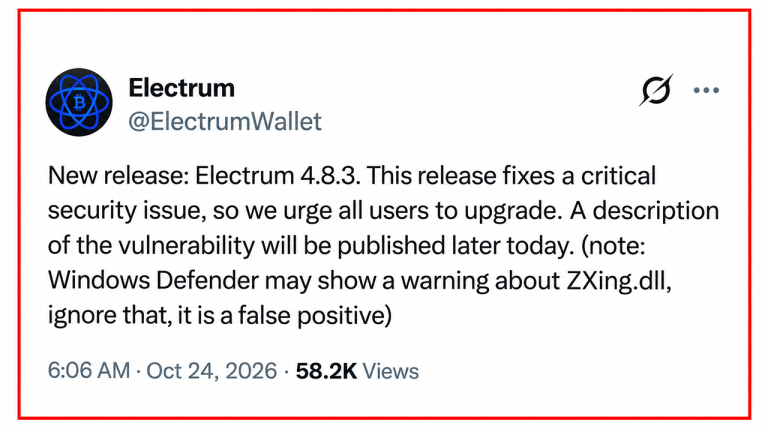
Electrum Wallet Attack Hid Bitcoin Theft Behind a Fee Increase
A malicious bitcoin wallet server could quietly swap a legitimate payment for a thief’s transaction, then wait for its owner to ap...

Passport Wallet Maker Foundation Traces Phishing Emails to Backend Breach, Promises Report
Foundation, the company behind the Passport bitcoin hardware wallet, said customer funds and devices are safe after attackers sent...
UNDP And Blockchain For Good Put Public-Service Security Ahead Of New Payment Rails
UNDP and the Blockchain for Good Alliance announced a two-year cybersecurity programme on October 19. The initiative brings a prac...
Binance Founder CZ Makes Shocking Claim About AI Hacking: “No Crypto Wallet Is 100% Safe”
The comments followed two X posts in which CZ discussed the limits of digital security and AI risks, highlighting phishing and soc...
US Launches $5M Pacific Program to Hunt Illicit Crypto Funds
The Trump Administration announced a series of initiatives that will encompass an investment of over $18 million to disrupt crimin...