FBI Issues Alert Concerning Malicious State-Sponsored North Korean Hackers Targeting Crypto Firms
On April 18, the Federal Bureau of Investigation (FBI), the U.S. Treasury Department, and the Cybersecurity and Infrastructure Security Agency (CISA) published a Cybersecurity Advisory (CSA) report concerning malicious N...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
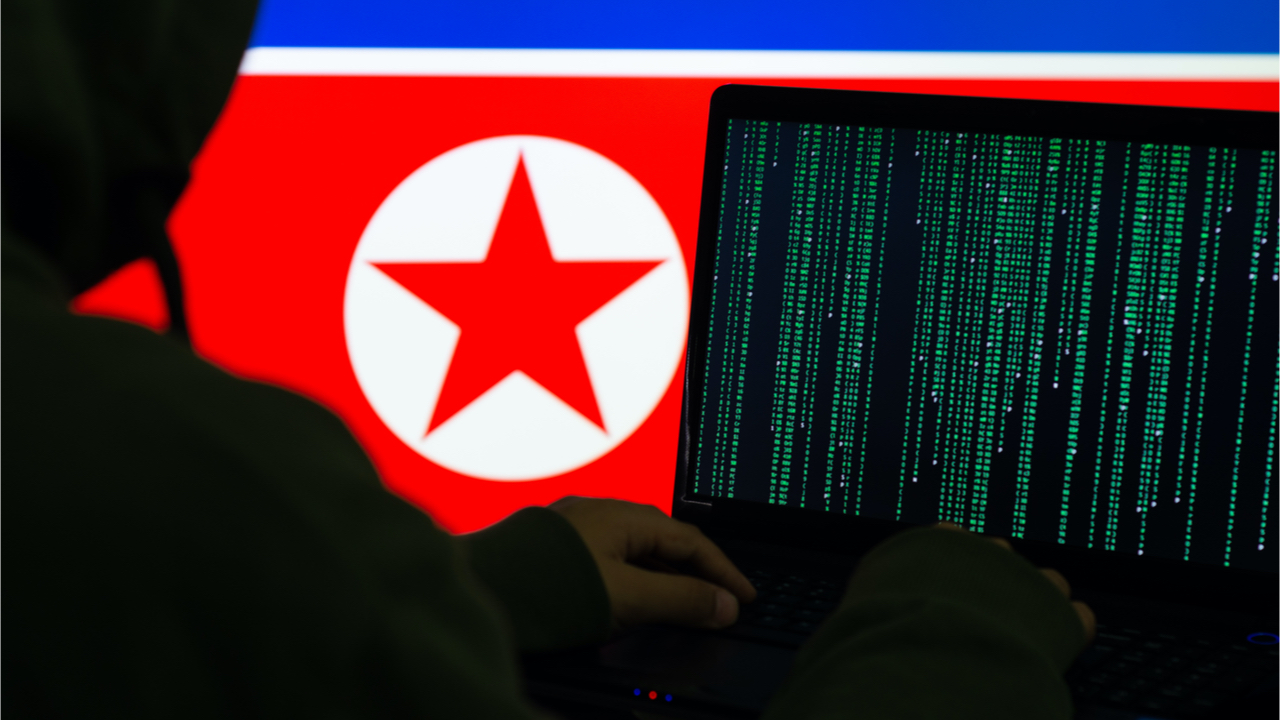
On April 18, the Federal Bureau of Investigation (FBI), the U.S. Treasury Department, and the Cybersecurity and Infrastructure Security Agency (CISA) published a Cybersecurity Advisory (CSA) report concerning malicious North Korean state-sponsored cryptocurrency activity. According to the U.S. government, law enforcement officials have observed North Korean cyber actors targeting specific blockchain companies in the industry.
FBI Alleges North Korean Hacking Activity Is on the Rise, Report Highlights Lazarus Group’s ActivitiesThe FBI, alongside a number of U.S. agencies, published a CSA report called “North Korean State-Sponsored APT Targets Blockchain Companies.” The report details that the APT (advanced persistent threat) has been state-sponsored and active since 2020. The FBI explains that the group is commonly known as Lazarus Group, and U.S. officials accuse the cyber actors of a number of malicious hack attempts.
North Korean cyber actors target a variety of organizations such as “organizations in the blockchain technology and cryptocurrency industry, including cryptocurrency exchanges, decentralized finance (defi) protocols, play-to-earn cryptocurrency video games, cryptocurrency trading companies, venture capital funds investing in cryptocurrency, and individual holders of large amounts of cryptocurrency or valuable non-fungible tokens (NFTs).”
The FBI’s CSA report follows the recent Office of Foreign Assets Control (OFAC) update which accuses Lazarus Group and North Korean cyber actors of being involved in the Ronin bridge attack. After the OFAC update was published, the ethereum mixing project Tornado Cash revealed it was leveraging Chainalysis tools, and blocking OFAC-sanctioned ethereum addresses from using the ether mixing protocol.
‘Apple Jesus’ Malware and the ‘TraderTraitor’ TechniqueAccording to the FBI, Lazarus Group leveraged malicious malware called “Apple Jesus,” which trojanizes cryptocurrency companies.
“As of April 2022, North Korea’s Lazarus Group actors have targeted various firms, entities, and exchanges in the blockchain and cryptocurrency industry using spearphishing campaigns and malware to steal cryptocurrency,” the CSA report highlights. “These actors will likely continue exploiting vulnerabilities of cryptocurrency technology firms, gaming companies, and exchanges to generate and launder funds to support the North Korean regime.”
The FBI says the North Korean hackers utilized massive spearphishing campaigns sent to employees working for crypto firms. Typically the cyber actors would target software developers, IT operators, and Devops employees. The tactic is called “TraderTraitor” and it often mimics “a recruitment effort and offer high-paying jobs to entice the recipients to download malware-laced cryptocurrency applications.” The FBI concludes that organizations should report anomalous activity and incidents to the CISA 24/7 Operations Center or visit a local FBI field office.
What do you think about the FBI’s claims about North Korean state-sponsored cyber attackers? Let us know what you think about the FBI’s latest report in the comments section below.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on Bitcoin NewsRelated market context
North Korean hackers routed Bybit loot through Sky’s stablecoin swap module, report finds
The incident highlights vulnerabilities in DeFi systems, potentially prompting increased regulatory scrutiny and impacting institu...
South Korea Set to Let 3,500 Companies Buy Bitcoin, Report Says
Bitcoin Magazine South Korea Set to Let 3,500 Companies Buy Bitcoin, Report Says South Korea’s Financial Services Commission plans...
US Task Force’s New Scam-Fighting Hub Taps Crypto Firms and Runs on TRM Labs Software
The Homeland Security Task Force (HSTF), a permanent federal law enforcement network, on Wednesday launched the Threat Disruption...
SEC Charges Eight Colorado Firms in $37 Million Fake Crypto Platform Scam
Bitcoin Magazine SEC Charges Eight Colorado Firms in $37 Million Fake Crypto Platform Scam The SEC charged eight Colorado-based en...
Binance Hack-Linked Wallet Moves 34,279 ETH, but Investigators See No Confirmed Sale
TL;DR Investigators tracked 34,279.66 ETH from a Binance hack-linked address to three new wallets. The movement was worth roughly...
H100 Group asks shareholders to approve buybacks funded by its Bitcoin trading pool
H100's buyback plan could set a precedent for Swedish firms, influencing market strategies and shareholder value perceptions amid...