Ledger scammers are sending letters to steal seed phrases
Scammers are mailing physical letters to the owners of Ledger crypto hardware wallets asking them to validate their private seed phrases in a bid to access the wallets to clean them out.In an April 29 X post, tech commen...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
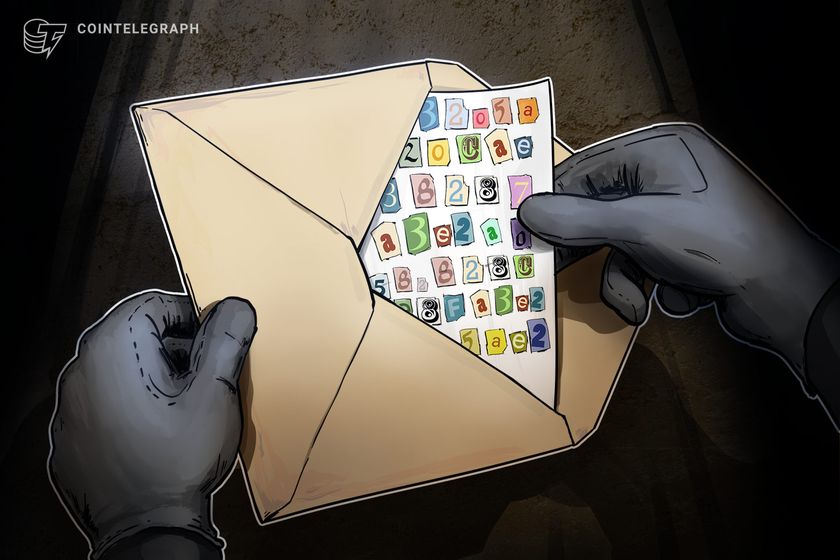
Scammers are mailing physical letters to the owners of Ledger crypto hardware wallets asking them to validate their private seed phrases in a bid to access the wallets to clean them out.
In an April 29 X post, tech commentator Jacob Canfield shared a scam letter sent to his home via post that appeared to be from Ledger claiming he needed to immediately perform a “critical security update” on his device.
The letter, which uses Ledger’s logo, business address, and a reference number to feign legitimacy, asks to scan a QR code and enter the wallet’s private recovery phrase under the guise of validating the device.
The letter threatens that “failure to complete this mandatory validation process may result in restricted access to your wallet and funds.”
A seed phrase, or recovery phrase, is a string of up to 24 words that unlocks access to a crypto wallet. A scammer with the phrase can access and control the associated wallet to transfer its holdings elsewhere.
Earlier this month, the X account of a crypto hardware wallet reseller said it had also received multiple reports of Ledger users receiving a similar letter.
In response to Canfield’s post, Ledger said the letter is a scam and cautioned its device users to stay vigilant against phishing attempts.
Related: Ledger wallet user reports 10 BTC loss — Community blames phishing
“Ledger will never call, DM [direct message], or ask for your 24-word recovery phrase. If someone does, it's a scam,” it added.
“Please don't engage with accounts claiming to be Ledger employees or anyone offering to help recover funds.”Unclear whether connected to the Ledger’s data leakCanfield suggested that scammers were sending letters to Ledger customers whose data was leaked nearly five years ago.
In July 2020, a hacker breached Ledger’s database and dumped the personal information of more than 270,000 of its customers online, which included names, phone numbers and home addresses
The following year, several Ledger users claimed to have been mailed fake Ledger devices that were tampered with and designed to install malware upon use, Bleeping Computer reported at the time.
Magazine: Your AI ‘digital twin’ can take meetings and comfort your loved ones
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context

Trezor Cuts Resellers After $86M Wallet Tampering Scare, Says Devices Remain Safe
Key Takeaways: Trezor recently has seen hardware wallet supply chain issues, so it has shortened its list of authorized retailers....
XRP Ledger patches lending protocol with follow-up amendment before launch
The delayed launch and patching of XRP Ledger's lending protocol highlight the complexities and challenges in achieving consensus...
Qubic Halts Network After $1.4M Seed Exploit, Tether Backs AI Startup AIsa, Circle Eyes 40 Developing Markets
Qubic halts after a $1.4M seed exploit hits 1,400+ accounts, Tether backs AI firm AIsa, and Circle targets 40 developing markets....
XRP Ledger Repairs Its Lending Protocol Before It Goes Live
XRP developers published a second amendment to repair the ledger’s new uncollateralized lending feature while the original still a...
Kraken’s opt-in European wallet can expose spot holdings to futures losses
After eligible EEA Kraken Pro users opt in, default cross margin can draw on their full eligible balance, including qualifying Ear...
Trust Wallet cuts 200 MB from its app by deleting nine years of code
Streamlining Trust Wallet enhances performance and security, reducing technical debt and attack surfaces, while optimizing resourc...