Supply chain attack hits Axios npm releases, users urged to rotate keys
Security companies flagged [email protected] and 0.30.4 as compromised, urging credential rotation and rollback of affected packages.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Security companies flagged [email protected] and 0.30.4 as compromised, urging credential rotation and rollback of affected packages.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context

AI Could Weaken Ethereum Security as Cryptographic Risks Grow, Vitalik Buterin Warns
Buterin urged developers to prepare for potential AI vulnerabilities in both conventional and quantum-resistant cryptography, whil...

Vitalik Warns AI Math Could Threaten Crypto Keys Before Quantum Computing Arrives
Key Takeaways: Vitalik Buterin states that the rise of today’s cryptography is outpaced by AI-accelerated mathematics. In addition...
BNB Chain Hits 2 Million RWA Holders, Capturing 40% of Onchain Market
BNB Chain has become the first blockchain to surpass 2 million holders of tokenized real-world assets (RWAs), giving it roughly 40...
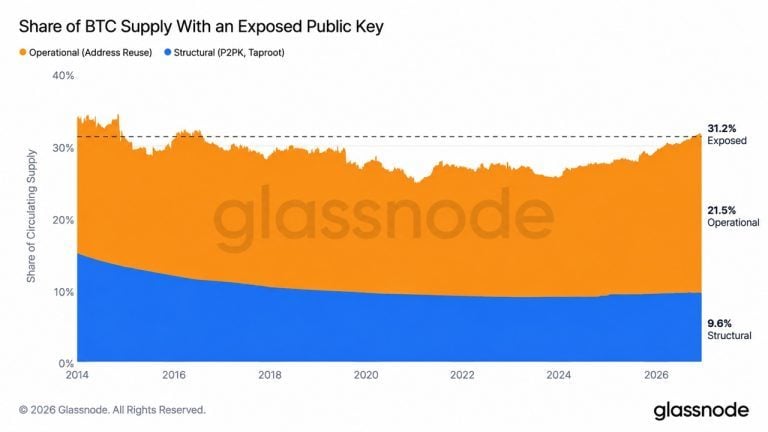
Glassnode: Over $500B in Bitcoin Is Sitting Behind Keys Anyone Can Read
Glassnode says 6.26 million BTC, or 31.2% of supply, now sits in addresses whose public keys are already visible onchain. The coun...
XRP Ledger discloses overflow bug that could have minted XRP beyond its supply cap
The XRP Ledger bug highlights the critical need for robust security measures and swift response protocols to maintain trust in blo...
Ledger hack scare nears $90 million as Tether moves to freeze stolen USDT
Suspected Ledger wallet thefts are approaching $90 million as Tether freezes USDT stablecoin linked to the incident, according to...