Malicious Pull Request Inserted Into Ethereum Code Extension: Research
Cybersecurity firm ReversingLabs uncovered two lines of malicious code in an update forETHCode, an open source suite of tools.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Why this matters
This ethereum story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on DecryptRelated market context
Gnosis bridges cut Ethereum deposit waits to seconds with fast confirmation
Gnosis' integration of FCR enhances transaction speed, potentially boosting user engagement and cross-chain activity, despite secu...

AI Could Weaken Ethereum Security as Cryptographic Risks Grow, Vitalik Buterin Warns
Buterin urged developers to prepare for potential AI vulnerabilities in both conventional and quantum-resistant cryptography, whil...
AI Coding Agents Drive Surge in Bitcoin Integration Requests: Breez
Bitcoin Magazine AI Coding Agents Drive Surge in Bitcoin Integration Requests: Breez Bitcoin software company Breez said demand fo...
Gnosis Bridges Adopt Fast Confirmation for Ethereum Deposits
Users and apps need no changes, but the faster processing relies on different security guarantees from Ethereum finality.... Read...
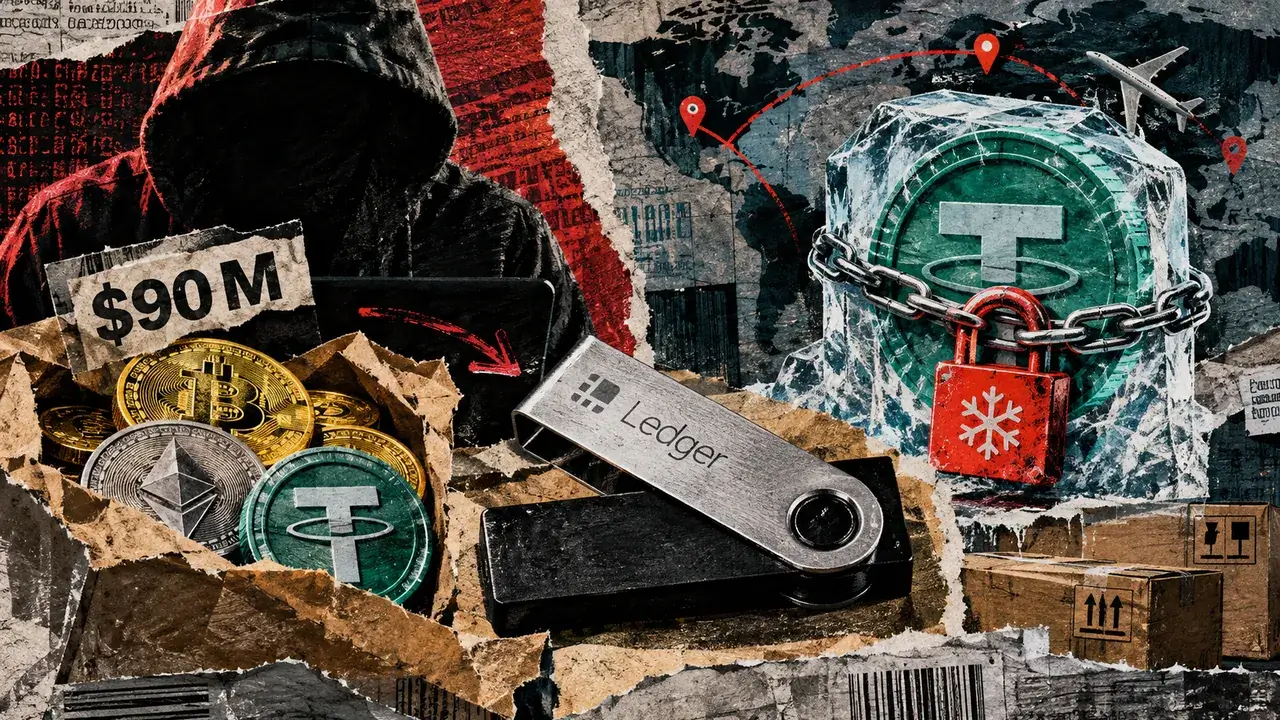
Ledger hack scare nears $90 million as Tether moves to freeze stolen USDT
Suspected Ledger wallet thefts are approaching $90 million as Tether freezes USDT stablecoin linked to the incident, according to...
OpenAI, Google and Meta battle for AI internet domains as crypto firms target .bitcoin and .wallet
OpenAI, Google, and Meta are competing for AI-related internet domains as cryptocurrency firms pursue their own digital naming rig...