Crypto founders report deluge of North Korean fake Zoom hacking attempts
At least three crypto founders have reported foiling an attempt from alleged North Korean hackers to steal sensitive data through fake Zoom calls over the past few days. Nick Bax, a member of the white hat hacker group t...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
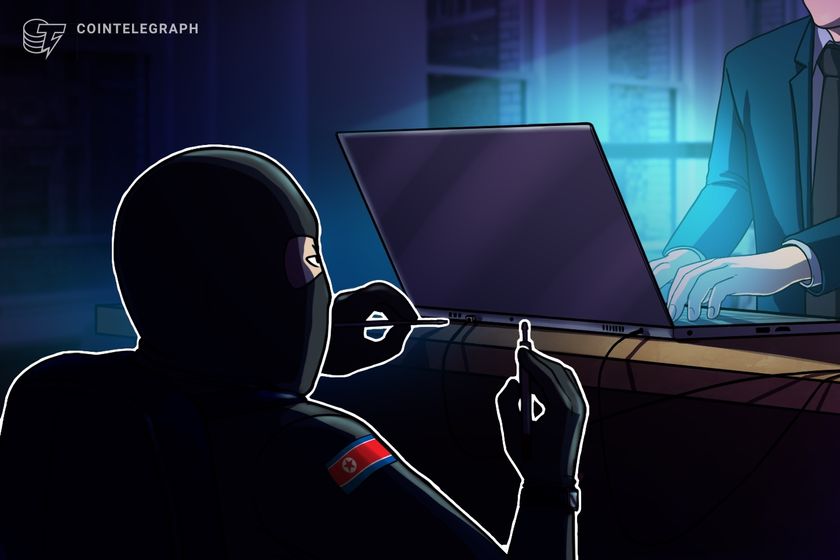
At least three crypto founders have reported foiling an attempt from alleged North Korean hackers to steal sensitive data through fake Zoom calls over the past few days.
Nick Bax, a member of the white hat hacker group the Security Alliance, said in a March 11 X post the method used by North Korean scammers had seen millions of dollars stolen from suspecting victims.
Generally, the scammers will contact a target with a meeting offer or partnership, but once the call starts, they send a message feigning audio issues while a stock video of a bored venture capitalist is on the screen; they then send a link to a new call, according to Bax.
Having audio issues on your Zoom call? That's not a VC, it's North Korean hackers.
Fortunately, this founder realized what was going on.
The call starts with a few "VCs" on the call. They send messages in the chat saying they can't hear your audio, or suggesting there's an… pic.twitter.com/ZnW8Mtof4F
“It’s a fake link and instructs the target to install a patch to fix their audio/video,” Bax said.
“They exploit human psychology, you think you’re meeting with important VCs and rush to fix the audio, causing you to be less careful than you usually are. Once you install the patch, you’re rekt.”The post prompted several crypto founders to detail their experiences with the scam.
Giulio Xiloyannis, co-founder of the blockchain gaming Mon Protocol, said scammers tried to dupe him and the head of marketing with a meeting about a partnership opportunity.
However, he was alerted to the ruse when, at the last minute, he was prompted to use a Zoom link that “pretends to not be able to read your audio to make you install malware.”
“The moment I saw a Gumicryptos partner speaking and a Superstate one I realized something was off,” he said.
Source: Giulio Xiloyannis
David Zhang, co-founder of US venture-backed stablecoin Stably, was also targeted. He said the scammers used his Google Meet link but then made up an excuse about an internal meeting, asking him to join that meeting instead.
“The site acted like a normal Zoom call. I took the call on my tablet though, so not sure what the behavior would’ve been on desktop,” Zhang said.
“It probably tried to determine the OS before prompting the user to do something, but it just wasn’t built for mobile Oses.”
Source: David Zhang
Melbin Thomas, founder of Devdock AI, a decentralized AI platform for Web3 projects, said he was also hit with the scam and was unsure if his tech was still at risk.
“The same thing happened to me. But I didn’t give my password while the installation was happening,” he said.
“Disconnected my laptop and I reset to factory settings. But transferred my files to a hard drive. I have not connected the hard drive back to my laptop. Is it still infected?”
Related: Fake Zoom malware steals crypto while it’s ‘stuck’ loading, user warns
This comes after the US, Japan and South Korea on Jan. 14 issued a joint warning against the growing threat presented by cryptocurrency hackers associated with North Korean hackers.
Groups such as the Lazarus Group are prime suspects in some of the biggest cyber thefts in Web3, including the Bybit $1.4 billion hack and the $600 million Ronin network hack.
The Lazarus Group has been moving crypto assets using mixers following a string of high-profile hacks, according to blockchain security firm CertiK, which detected a deposit of 400 Ether (ETH) worth around $750,000 to the Tornado Cash mixing service.
Magazine: Lazarus Group’s favorite exploit revealed — Crypto hacks analysis
Why this matters
This research story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context
Ledger Says Organized Crime Group Spent Millions Targeting Hardware Wallet Users
Bitcoin Magazine Ledger Says Organized Crime Group Spent Millions Targeting Hardware Wallet Users Ledger has issued a statement fo...

Coinbase Joins 4-Day Crackdown on West Africa Crypto Scams and Asset Freezes
Key Takeaways: Coinbase participated in a four-day assault of scam networks in West Africa in London. Its Global Intelligence team...

USDC’s EU Reserves and Capital Shift to EBA Supervision in MiCA’s First ‘Significant’ Call
Circle’s European USDC issuer will answer to the European Banking Authority (EBA) on reserves, liquidity and capital from Nov. 12,...
FBI helps smash crypto scam targeting Russian speakers in Brooklyn
The FBI has helped take down a crypto scam network that targeted Russian-speaking individuals living in the US and likely stole te...
XRP Price Prediction: Evernorth’s $648M Game Plan Takes Shape
XRP trades at $1.30, down 6% over 24 hours, as traders weigh sticky U.S. inflation against a major institutional treasury plan. Ev...
Ripple targets trillion-dollar securities markets with new US brokerage and South Korean deals
Ripple calls Meritz its fourth Korean institutional partner this year, with custody and tokenization cooperation to widen as regul...