New ‘Crocodilus’ Android Malware Steals Sensitive Crypto Wallet Credentials: Research
A new “highly capable” mobile banking malware dubbed “Crocodilus,” targets Android devices, extorting sensitive crypto wallet credentials using social engineering tactics.A recent research by cybersecurity firm Threat Fa...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
A new “highly capable” mobile banking malware dubbed “Crocodilus,” targets Android devices, extorting sensitive crypto wallet credentials using social engineering tactics.
A recent research by cybersecurity firm Threat Fabric found the emergence of a new malware family Crocodilus. The malware is reportedly distributed through a proprietary dropper that bypasses Android 13+ restrictions.
“Despite being new, it already includes all the necessary features of modern banking malware: overlay attacks, keylogging, remote access, and ‘hidden’ remote control capabilities,” analysts noted.
Sophisticated Android malware designed to steal cryptocurrency private keys isn’t new. In October 2024, the FBI issued a warning about a similar malware called SpyAgent, which was linked to North Korean hackers.
However, what differs in the new mobile banking Trojan Crocodilus is the “device takeover and advanced credential theft,” Threat Fabric wrote on X.
A new mobile banking Trojan has emerged—#Crocodilus. Discovered during regular threat hunting, it’s already showing capabilities that rival top malware families, including device takeover and advanced credential theft.https://t.co/RlyfFxUYHe#BankingTrojan #ThreatFabric pic.twitter.com/47zPbPfFad
— ThreatFabric (@ThreatFabric) March 28, 2025 Crocodilus Displays Overlays to Target Banks and CryptosCrocodilus malware works on a modus operandi similar to modern “Device Takeover banking Trojan,” analysts noted. After initial installation via a proprietary dropper, the malware requests “Accessibility Service” to be enabled, they added.
In order to intercept credentials, Crocodilus connects to the command-and-control (C2) server for instructions such as overlays to be used.
Further, the threat initially appeared in Spain and Turkey, targeting several crypto wallets, the Mobile Threat Intelligence team revealed.
“We expect this scope to broaden globally as the malware evolves,” the team noted.
Additionally, the two-factor authentication (2FA) is bypassed by the malware using RAT command that triggers a screen capture on the content of the Google Authenticator application. Crocodilus captures the code displayed on the screen in the Google Authenticator app, and sends to the C2.
Malware Instructs Victims to Do the JobUnlike other Trojans, Crocodilus overlays target crypto wallet by asking victims to take a backup of their wallet keys.
“Back up your wallet key in the settings within 12 hours. Otherwise, the app will be reset, and you may lose access to your wallet,” the overlay text reads.
This social engineering hack guides victims to navigate to their seed phrase. This inturn allows Crocodilus to extract the text using its Accessibility Logger.
“With this information, attackers can seize full control of the wallet and drain it completely,” Threat Fabric analysts said.
The post New ‘Crocodilus’ Android Malware Steals Sensitive Crypto Wallet Credentials: Research appeared first on Cryptonews.
Why this matters
This research story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CryptonewsRelated market context
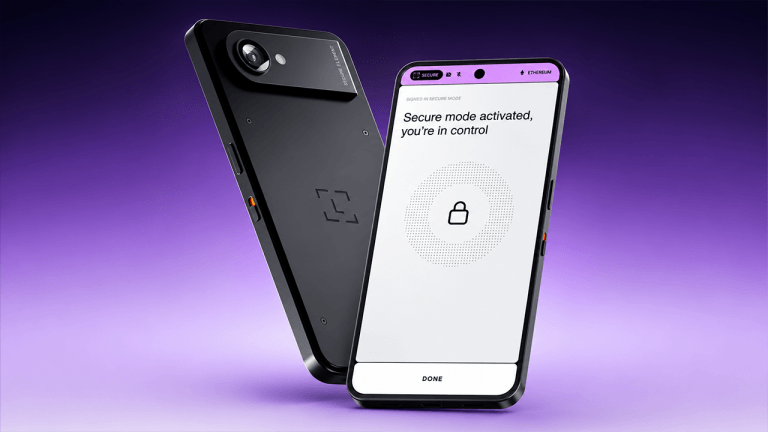
Ledger Launches $849 Android Vault After Multi-Million Dollar Wallet Scare
Ledger has unveiled Atom, an $849 Android-powered security device that integrates Solana Mobile’s Seeker ecosystem, artificial int...
Criminals steal an estimated $90M in crypto using tampered hardware wallets
The incident highlights vulnerabilities in supply chains and raises concerns about the security of crypto assets, impacting user t...
Ledger unveils Atom, an Android security device with Solana Mobile integration
Ledger's Atom could redefine crypto security by integrating AI oversight and Solana, potentially enhancing user trust and market r...
Ledger asks more Southeast Asia resellers to halt wallet sales
Crypto wallet firm Ledger is asking resellers and distributors in Hong Kong and countries across Southeast Asia to stop selling it...
Cross River Bank Brings Ripple’s RLUSD Into Traditional Banking
On Thursday, a spokesperson for Cross River Bank told Bitcoin.com News that it is teaming up with Ripple to make it easier for bus...

Ripple and Privy Bring XRP Wallets to XRPL After $1T Moved Across 8M Accounts
Key Takeaways: With the collaboration of Ripple, Privy offers programmable wallet infrastructure to the XRP Ledger. Developers can...