Bunni Hit by $8.4M Flash-Loan Exploit — ‘Rounding Error’ Blamed
Decentralized finance protocol Bunni suffered an $8.4 million exploit on September 2, after a sophisticated attacker leveraged a flash loan to manipulate liquidity pools on both Ethereum and Unichain. The incident, which...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Decentralized finance protocol Bunni suffered an $8.4 million exploit on September 2, after a sophisticated attacker leveraged a flash loan to manipulate liquidity pools on both Ethereum and Unichain.
The incident, which targeted the weETH/ETH and USDC/USDT pools, has been attributed to a flaw in Bunni’s smart contract logic involving rounding errors.
Bunni Blames Rounding Bug for $2.3M Exploit, Offers 10% BountyAccording to Bunni’s post-mortem, the exploit was executed in three stages. The attacker first borrowed 3 million USDT via a flash loan, using it to manipulate the USDC/USDT pool’s spot price to extreme levels.
With the pool’s active USDC balance reduced to just 28 wei, the exploiter initiated 44 small withdrawals. This exploited a rounding error in Bunni’s code, disproportionately lowering the pool’s liquidity by over 84%.
Exploit Update: The Bunni team has completed analysis of the recent exploit. The details are available in this post mortem blog post (link in comment).
Withdrawals have been unpaused, so LPs are now free to withdraw their assets. All other operations remain paused.
With liquidity artificially suppressed, the attacker carried out a sandwich attack, executing large swaps that pushed prices to distorted values.
By reversing the earlier liquidity reduction, they extracted profits before repaying the flash loan. In total, the exploit yielded approximately 1.33 million USDC and 1 million USDT for the attacker.
Blockchain security firm Cyfrin confirmed that the vulnerability stemmed from how Bunni’s smart contract rounded balances during withdrawals.
While the mechanism was designed to favor pool safety by underestimating liquidity, repeated tiny withdrawals created conditions that allowed the rounding logic to be exploited at scale.
Bunni noted that its largest pool, Unichain’s USDC/USD₮0 pair, was spared due to insufficient flash-loan liquidity available to mount an attack. Exploiting that pool would have required roughly $17 million in borrowed assets, but only $11 million was available across lending venues at the time.
Bunni confirmed that the stolen assets are now split across two wallets linked to the attacker. Investigators traced the origins of the funds but hit a dead end after discovering the wallets were funded through Tornado Cash, a sanctioned privacy tool.
The team has contacted the exploiter directly on-chain, offering a 10% bounty in exchange for returning the remaining funds. Centralized exchanges have also been notified to prevent any attempted off-ramps, while law enforcement has been engaged to pursue recovery options.
In the immediate aftermath, Bunni paused all operations but has since re-enabled withdrawals to allow liquidity providers to recover their deposits. Deposits and swaps remain frozen while developers work on a fix.
Changing the rounding direction of the affected function neutralizes the current exploit vector, though the team acknowledged more extensive testing and security improvements are needed before reopening fully.
Bunni, operated by a six-person team, said it remains committed to continuing development despite the setback. The protocol introduced novel concepts such as Liquidity Density Functions (LDFs), which the team claims represent a new generation of automated market makers.
“We spent years building Bunni because we believe it is the future of AMMs,” the team said in its statement, while pledging to strengthen its codebase and testing frameworks to prevent similar attacks.
August Marks Third-Worst Month for Crypto Security as $163M Lost to Hacks and ScamsBunni, once boasting over $80 million in total value locked (TVL) on BNB Chain, now holds just above $50 million following the exploit. The incident adds to a string of attacks and scams hammering the sector.
Just a day earlier, a Venus Protocol user lost $13.5 million in a phishing scam. According to blockchain security firm PeckShield, the victim unknowingly approved a malicious transaction, granting token permissions that enabled the theft.
@VenusProtocol recovers $27M from exploiter through force-liquidation, sparking decentralization debate over governance intervention.#BNB #Hackhttps://t.co/IO2WhCF0S6
— Cryptonews.com (@cryptonews) September 3, 2025While initial reports suggested $27 million was drained, later analysis showed that debt positions were mistakenly included in the figure. Venus stressed that its smart contracts remained secure and confirmed that only the user was compromised.
The incident followed a surge in crypto-related exploits in August, with PeckShield data showing $163 million stolen across 16 major attacks, up from $142 million in July. The losses made August the third-worst month for crypto security in 2025.
The largest single theft occurred on August 19, when a Bitcoin holder lost 783 BTC, worth $91.4 million, in a social engineering scheme. Attackers allegedly posed as hardware wallet support staff to obtain sensitive credentials before laundering the funds through Wasabi Wallet.
BtcTurk (@btcturk), Turkey's second-largest crypto exchange, loses $48M in a major hack targeting hot wallets across 7 blockchain networks, marking its second incident in 14 months.#CryptoHack #Turkeyhttps://t.co/6Yr8mwgUYO
— Cryptonews.com (@cryptonews) August 14, 2025The Turkish exchange BtcTurk was also hit, losing $54 million in a multi-chain hot wallet breach across seven blockchain networks. The incident brought its cumulative losses to over $100 million following a prior hack in June 2024.
Other notable cases included ODIN•FUN’s $7 million loss, BetterBank.io’s $5 million exploit, and CrediX Finance’s $4.5 million collapse, which turned into an exit scam after developers abandoned the project.
With phishing, exchange vulnerabilities, and exit scams driving mounting losses, August underscored how both technical flaws and human error continue to plague the crypto industry.
The post Bunni Hit by $8.4M Flash-Loan Exploit — ‘Rounding Error’ Blamed appeared first on Cryptonews.
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CryptonewsRelated market context
Samsung Wallet Brings USDC Transfers to 82 Million US Galaxy Devices in Late October
Samsung announced Oct. 7 that eligible Galaxy users in the US will be able to send USDC from Samsung Wallet starting in the last w...
82 Million Galaxy Devices Will Support USDC Transfers This October
USDC is set to become Samsung Wallet’s default dollar stablecoin as Coinbase expands its partnership with the smartphone maker. Th...
Wallet Shifts 150 Million USDT From Aave to Spark Savings
Aave’s Ethereum USDT reserve showed $169.54 million in available liquidity on Oct. 8, after withdrawals coincided with double-digi...
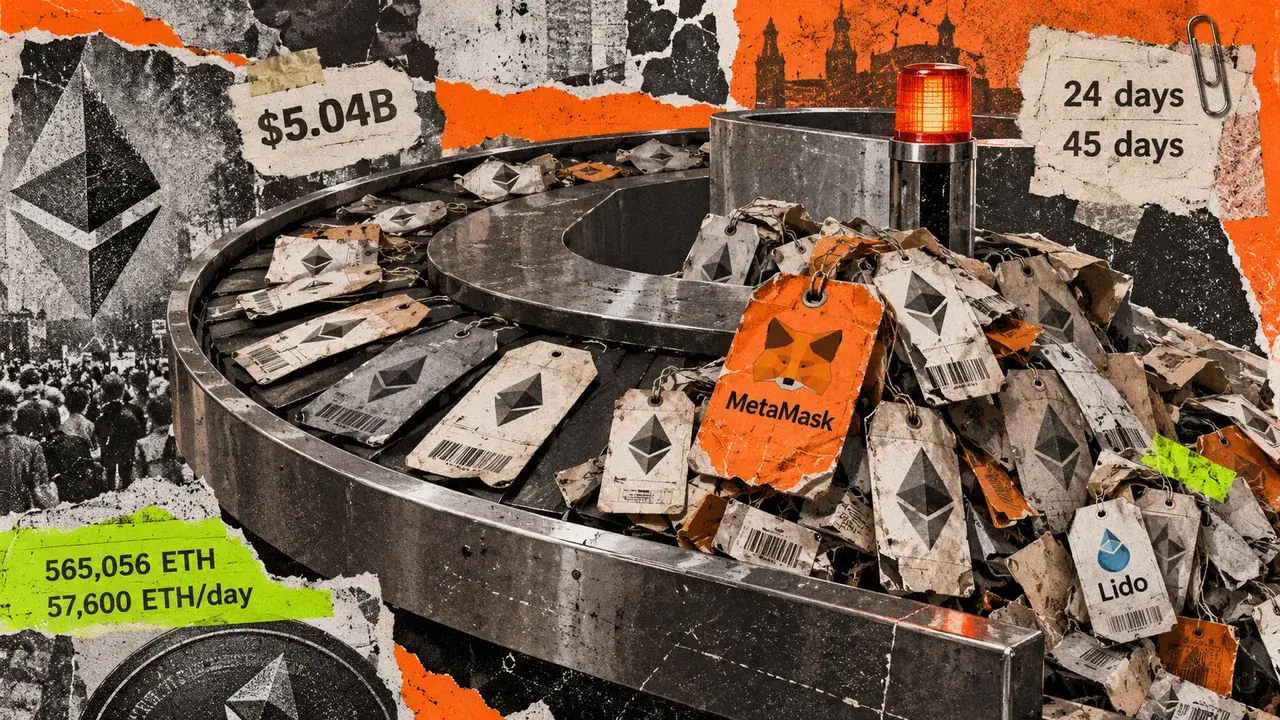
A $1,000 MetaMask incident could turn Ethereum’s staking queue into a $5 billion traffic jam
MetaMask's precautionary validator exits are turning a roughly $1,000 reward diversion into a test of Ethereum's staking capacity....
Wells Fargo Reportedly Talking With Kraken Parent Payward to Source Crypto Trading Liquidity
Wells Fargo is in discussions with Payward, the company that operates the Kraken exchange, about a deal that would have Payward su...

Bitcoin ETFs Bleed $484.9 Million As BlackRock Leads A Broad Day Of Outflows
TL;DR: US spot Bitcoin ETFs recorded $484.9 million in net outflows on October 7, according to Farside Investors. BlackRock’s IBIT...