How a third-party data leak led to phishing attempts against Ledger users
A third-party e-commerce breach exposed order data, enabling phishing attempts without compromising Ledger wallets or self-custody systems.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
A third-party e-commerce breach exposed order data, enabling phishing attempts without compromising Ledger wallets or self-custody systems.
Why this matters
This maps to the Security Incidents hub, so it can help confirm whether that theme is gaining breadth across the crypto news cycle.
Original source
Read on CointelegraphRelated market context

Trezor Shipping Partner Breach Exposes 27,000 Orders, Raising Crypto Phishing Risks
Key Takeaways: Data on approximately 27,000 orders was revealed after a breach of Trezor’s shipping partner, Skladon. The affected...
Trezor Warns 27,000 Shipping Orders Were Exposed in Partner Breach, Not Wallet Keys
TL;DR Trezor says shipping partner Skladon exposed data tied to about 27,000 orders. Names, contact details, addresses and purchas...
Bitcoin Wallet Maker Trezor Says Customer Data Was Exposed Again
A second Trezor shipping partner was breached in three months, exposing buyers' addresses and order details.
Aster Says It Tightened Security After API Wallet Leak
A trader alleges $4.56 million in unauthorized transfers. CEO Leonard told users with suspected key exposure to delete the affecte...
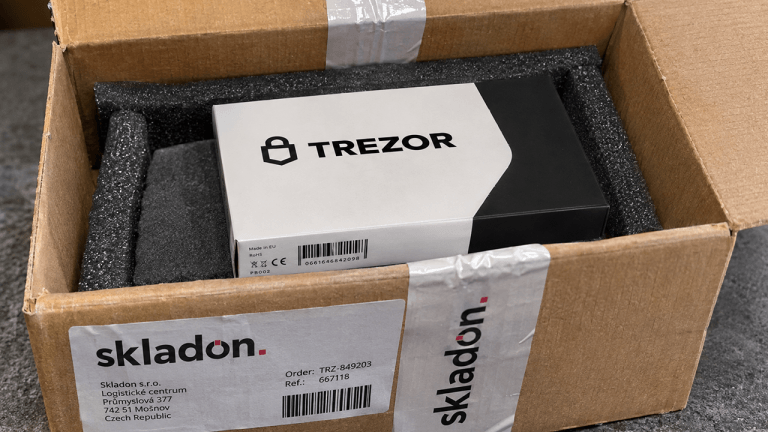
Hackers Strike Trezor Shipping Partner, Exposing Wallet Buyers’ Personal Details
Hardware wallet manufacturer Trezor disclosed Monday, Nov. 16, 2026, that a security breach at shipping partner Skladon exposed pe...
Coinbase Launches ChatGPT Plugin for Trading Bitcoin, Stocks, and Derivatives
Bitcoin Magazine Coinbase Launches ChatGPT Plugin for Trading Bitcoin, Stocks, and Derivatives Coinbase launched an official plugi...