SuperRare $730,000 exploit was easily preventable — Experts weigh in
A critical access control bug in SuperRare’s staking contract — easily detectable by unit tests or even ChatGPT — allowed an attacker to steal $731,000 in RARE tokens.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
A critical access control bug in SuperRare’s staking contract — easily detectable by unit tests or even ChatGPT — allowed an attacker to steal $731,000 in RARE tokens.
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context

Grayscale Adds BitGo To Hyperliquid Staking ETF Custody Setup
TL;DR: Grayscale has added BitGo Bank & Trust as an additional custodian for a portion of the HYPE held by its Hyperliquid Staking...
XRP Ledger adds new controls for banks, stablecoins and tokenized funds
The feature lets businesses give separate accounts limited powers such as approving customers or making payments, while keeping th...
Bitwise finds 5 US wealth platforms restrict Bitcoin ETP access
Limited access to Bitcoin ETPs on major platforms may hinder widespread adoption, affecting potential capital inflows and industry...
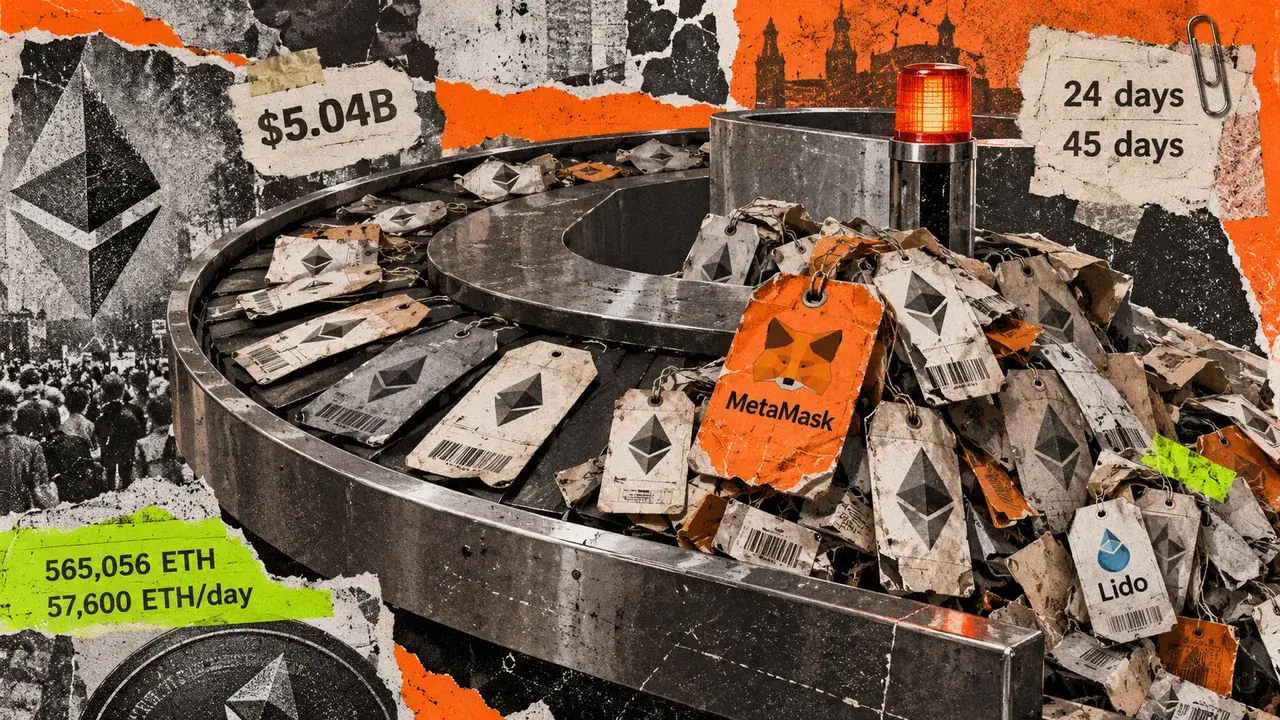
A $1,000 MetaMask incident could turn Ethereum’s staking queue into a $5 billion traffic jam
MetaMask's precautionary validator exits are turning a roughly $1,000 reward diversion into a test of Ethereum's staking capacity....

Uranium Finance hacker convicted over DeFi exploits and laundering
The conviction highlights the enduring vulnerability of DeFi platforms and the lengthy process of legal recourse, impacting user t...
Blanche Lincoln, who warned about sports event contracts, now lobbies for Kalshi
Lincoln's shift from warning to lobbying highlights the evolving regulatory landscape and potential federal-state conflicts in pre...