$50m Hack: Radiant Capital Hit Hard In Rare Multi-Sig Wallet Attack
According to a post from Blockchain security firm Slowmist, the private keys to 3 out of 11 addresses that managed the Radiant Capital project were compromised, and this was enough to approve malicious transactions that...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
According to a post from Blockchain security firm Slowmist, the private keys to 3 out of 11 addresses that managed the Radiant Capital project were compromised, and this was enough to approve malicious transactions that involved a “transfer ownership of the LendingPoolAddressesProvider contract to a malicious contract controlled by the attacker.” This then allowed the attacker to drain Radiant Capital’s lending pools on Arbitrum and BNB Chain.
Radiant Capital acknowledged the attack a few hours after it happened. They also paused their Base and Ethereum contracts as a precaution. On October 18th, the project wrote a longer post-mortem tweet stating — “The attackers exploited multiple developers’ hardware wallets through a highly advanced malware injection.”
They continue that Radiant Capital DAO “is deeply devastated by this attack and will continue to work tirelessly with the respective agencies to identify the exploiter and recover the stolen funds as quickly as possible.” They note in the post-mortem —“The DAO has significantly tightened security on the Admin & DAO multi-sigs (other safes to follow in due course) by reducing the number of signers to 7, with a new signing threshold of 4 out of 7, ensuring that nearly 60% of signers must approve a transaction before it can be executed.”
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on Brave New CoinRelated market context
Bitget hacker withdraws $1.23M from Binance, funnels funds to attacker-controlled wallet
The Bitget hack highlights vulnerabilities in crypto exchanges, prompting urgent calls for enhanced security measures and internat...
Crypto Hacks: Three Projects Hacked in One Day as Losses Hit Over $11M
Three crypto projects were attacked on September 24, suffering combined losses of more than $11M. Attackers drained around $1.8M f...
Bitget Confirms $387.5 Million Security Breach as Revised On-Chain Accounting Reveals Wider Losses
Bitget raises breach losses to $387.5 million after Zcash and TRON transfers found. Attackers spoofed backend transaction data to...
SEC clears regulatory hurdle as crypto token buybacks hit record $638 million
Crypto projects spent about $638 million with token buybacks through late August 2026, according to Allium Labs data. That is alre...
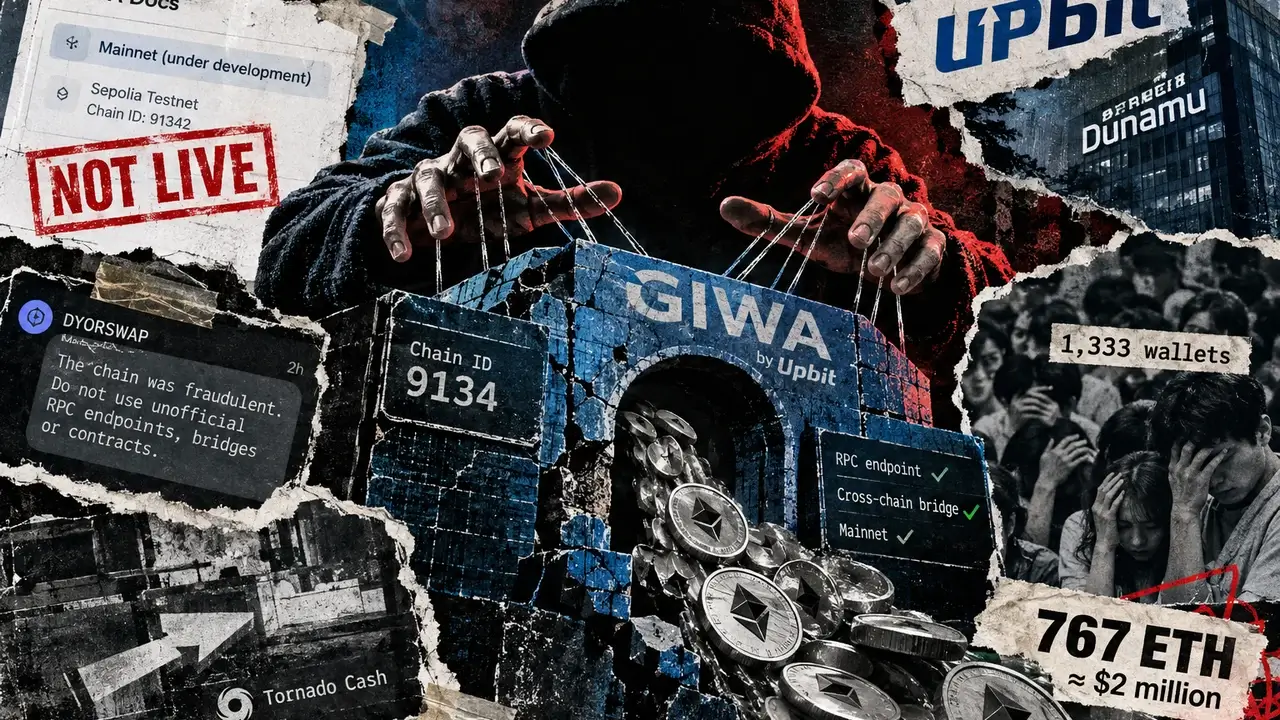
Crypto scammers built an entire fake blockchain to steal over $2 million
Scammers built a counterfeit version of Upbit-backed GIWA blockchain and lured 1,333 wallets into depositing 767 ETH, worth about...
DYORSWAP users tricked into sending 767 ETH to fake bridge contract
Crypto scammers managed to trick DYORSWAP, a multi-chain decentralized exchange, into integrating a spoofed version of upcoming bl...