OpenSea: Users Should Rotate API Keys Following Security Breach
It has been revealed that OpenSea notes the fact that users should rotate the API keys following the latest security breach. Check out the latest reports about the matter below. New security breach addressed OpenSea, a m...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.

It has been revealed that OpenSea notes the fact that users should rotate the API keys following the latest security breach. Check out the latest reports about the matter below.
New security breach addressedOpenSea, a marketplace for NFTs, has informed some of its users that one of its third-party vendors recently experienced a security incident that may have exposed information about their API keys.
Although OpenSea does not anticipate any programs that use an OpenSea API key to be affected, external parties that use one of the exposed keys may experience changes in rate and usage limits.
In response to the incident, OpenSea plans to sunset existing keys by October 2nd. However, the company has not disclosed how many users were impacted by the breach or if any other information was compromised. The Block has reached out to OpenSea for comment but has not received a response at this time.
The latest hack in the spotlightIt has come to light that a hacker stole a considerable amount of customer information from Nansen, a crypto data firm, by exploiting one of the company’s third-party vendors.
Nansen confirmed the security breach on Friday on social media platform X, admitting that the vendor breach allowed the hacker to access admin rights to an account used for customer access on their platform.
Initial inquiries indicate that 6.8% of users had their personal information compromised. Nansen has notified affected users via email, providing information on the scope of the security breach. The email addresses of all impacted users were exposed, while a smaller number had their password hashes and an even smaller group had their blockchain address exposed.
According to Nansen, a data firm in the crypto industry, a third-party vendor they use, who is an established company, has experienced a breach. It is uncertain at this time which company is responsible for the breach.
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CryptoGazetteRelated market context

Safepal Hardware Wallet Users Receive Fake Security Alerts in the Mail
Safepal customers in Italy are reportedly being targeted by a sophisticated phishing campaign involving fraudulent letters contain...
Why the Path to Quantum Resistance Runs Uphill for Wallet Manufacturers
Bitcoin custody has always involved some degree of risk, but wallet manufacturers like Trezor — which build physical devices desig...
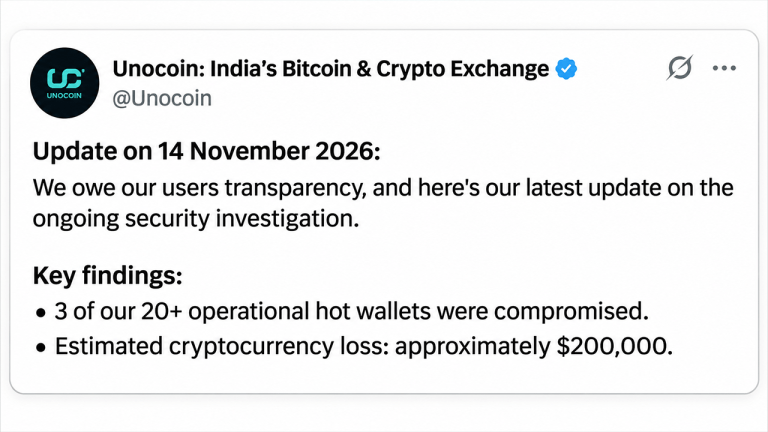
Unocoin Admits $200K Crypto Loss, Warns of Customer Data Breach
Indian cryptocurrency exchange Unocoin confirmed Saturday, Nov. 14, that attackers stole approximately $200,000 in cryptocurrency...
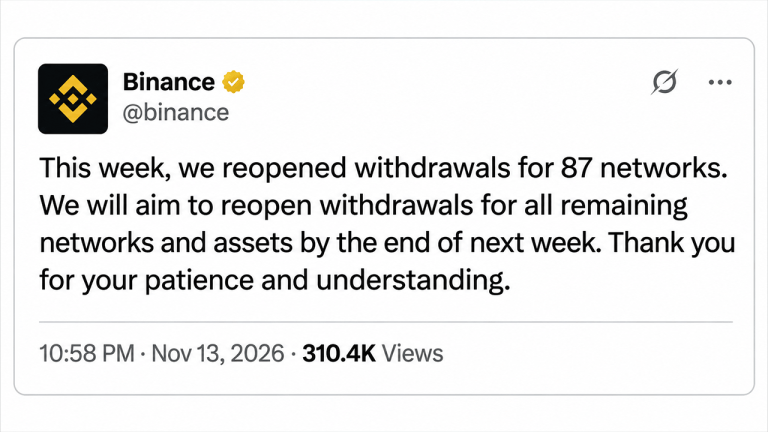
Binance Reopens 87 Networks Following Historic $6.3 Billion Breach
Binance has reopened withdrawals across 87 blockchain networks as the cryptocurrency exchange continues recovering from its devast...

Binance Puts New Reserve Snapshot Under Scrutiny After $6.3B Crypto Hack
Key Takeaways: Binance states that assets affected by the hack of $6.3B are covered. There is now a new Proof of Reserves snapshot...
U.S. Targets $1.2 Billion From Binance Hack—Where Is the Rest?
The Binance hack recovery has reached a significant milestone: U.S. authorities say more than $1.2 billion in stolen cryptocurrenc...