Dogecoin Flaw Exploited, Hacker Crashes 69% of Active Nodes
On December 12, 2024, the Dogecoin network was exploited when an “ethical” hacker uncovered a critical flaw. This exploit brought down a staggering 69% of the network’s active nodes, sparking serious questions about the...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
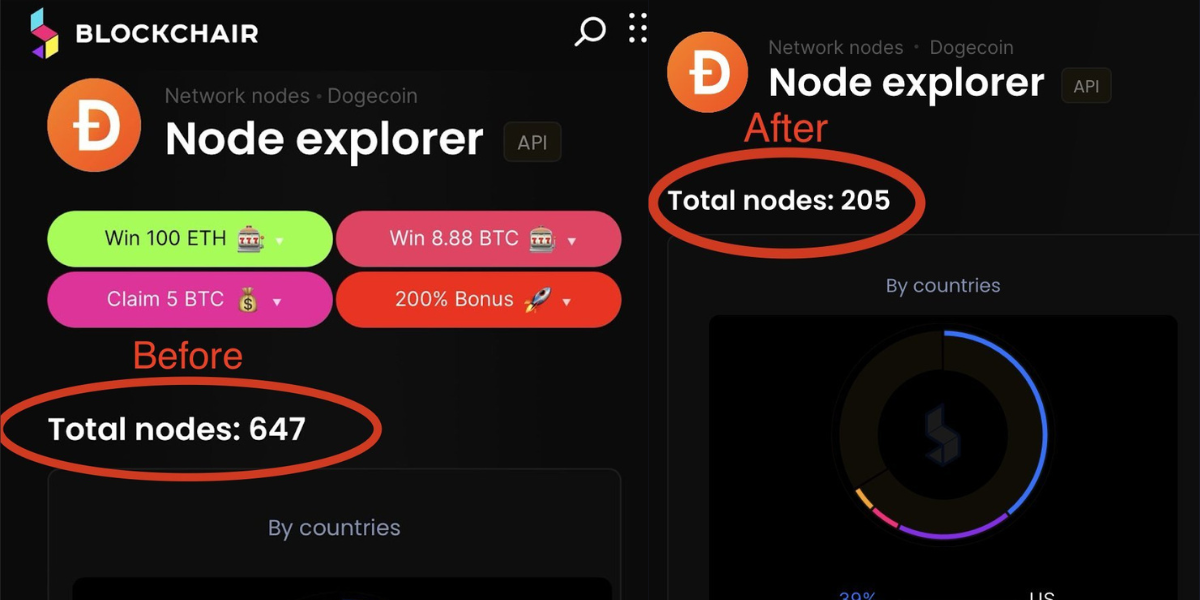
On December 12, 2024, the Dogecoin network was exploited when an “ethical” hacker uncovered a critical flaw. This exploit brought down a staggering 69% of the network’s active nodes, sparking serious questions about the security of decentralized systems and the risks that come with publicly accessible nodes.
The Exploit and Its ExecutionAndreas Kohl, co-founder of the Bitcoin sidechain Sequentia, admitted to carrying out the attack using a vulnerability he called “DogeReaper”. He ran the exploit from nothing more than an old laptop while in El Salvador.
I used a publicly disclosed (by @TobiasRuck) vulnerability to take down 69% of the Dogecoin network from an old thinkpad in rural el salvador. AMA. https://t.co/BNkGDWkWhu pic.twitter.com/qk16AwMaq5
— Andreas Kohl (@aejkohl) December 12, 2024
Before the attack, Dogecoin had 647 active nodes. After the exploit, the number of operational nodes dropped to just 205. Kohl’s actions have brought attention to a critical flaw in the network’s architecture.
The “DogeReaper” vulnerability, first disclosed by a social media account named “Department of DOGE Efficiency” on December 4, allows anyone to remotely crash Dogecoin nodes.
This vulnerability allows anyone to remotely crash Dogecoin nodes by triggering a segmentation fault – a software error that occurs when a program tries to access memory it shouldn’t. Because Dogecoin nodes are publicly listed, they’re easy pickings for anyone who knows how to exploit this flaw.
The “DogeReaper” is a sort of “Death Note” for Dogecoin nodes. The danger it posed was significant: a malicious hacker could have shut down the network entirely, halting transactions and block creation for days.
Also, despite its severity, the vulnerability was labeled “low-risk” by Coinbase. The researcher who discovered it, Tobias Ruck, received just $200 for his efforts. This decision has fueled debates about how the crypto world values major security findings like this one.
More News: Australia to Crack Down on Crypto ATM Providers Due to Money Laundering Risk
Community Response and Security ConcernsThe attack showed just how tricky it is to keep decentralized networks safe. Sharing the flaw out in the open might have been done to push developers to act quickly, but it also gave hackers an easy chance to use it. Some people think the better move would’ve been to tell developers privately and wait to share it after a fix was ready.
Now, Dogecoin’s team is working fast to fix the problem. This isn’t just Dogecoin’s headache – it’s a warning for all blockchain projects. Even popular platforms run by their communities can have serious security problems.
As crypto keeps growing, strong security is more important than ever. Decentralized networks need to stay open but also find ways to block potential attacks.
ConclusionDogecoin’s developers are working on updates to close the security hole. And node operators may need to upgrade their systems. Also, the crypto community and developers should take another look at their security protocols and check how they handle vulnerabilities.
The post Dogecoin Flaw Exploited, Hacker Crashes 69% of Active Nodes appeared first on CryptoNinjas.
Why this matters
This altcoin story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CryptoNinjasRelated market context
Brooklyn prosecutor Alona Katz takes on crypto scam networks behind $11 billion in losses
The crackdown highlights the urgent need for stronger legal frameworks to combat sophisticated crypto scams and protect vulnerable...
OpenAI’s GPT-5.6 Sol AI Model Spent Unauthorized ETH to Deploy Smart Contract
The incident occurred on June 26, 2026, during a task involving a cryptocurrency trading application on Sepolia, an Ethereum test...
Poetic Justice: Scammer Lost $5M in Bitcoin After Being Targeted by Ledger Thieves
Bitcoin Magazine Poetic Justice: Scammer Lost $5M in Bitcoin After Being Targeted by Ledger Thieves Call it poetic justice: one of...
Brooklyn DA Pulls the Plug on Crypto Scam Network
Bitcoin Magazine Brooklyn DA Pulls the Plug on Crypto Scam Network The Brooklyn District Attorney’s office has dismantled the onli...

Grayscale Opens DeFi And AI Crypto Funds To Investors With Just $2,500
TL;DR: Grayscale and investment platform Republic are offering three specialised crypto funds with minimum commitments starting at...
Vitalik Buterin breaks down Bitcoin mining costs versus AI inference
The analysis highlights the strategic shift in resource allocation, emphasizing efficiency and cost management as key factors for...