‘Dark Skippy’ method can steal Bitcoin hardware wallet keys
Malicious firmware can embed secret data into a public Bitcoin transaction, which the attacker can then use to extract a person’s seed words.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.

Malicious firmware can embed secret data into a public Bitcoin transaction, which the attacker can then use to extract a person’s seed words.
Why this matters
This bitcoin story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context

Changer+ Launches Stablecoin-First Self-Custodial Wallet to Make Stablecoins Easier to Use
Singapore, Singapore, October 6th, 2026, Chainwire Multi-chain stablecoin wallet combines simpler transfers, flexible gas-fee opti...
Europol warns crypto wallets are the weak spot for future quantum attacks
The crypto industry must urgently adopt quantum-resistant cryptography to prevent future vulnerabilities and secure digital assets...
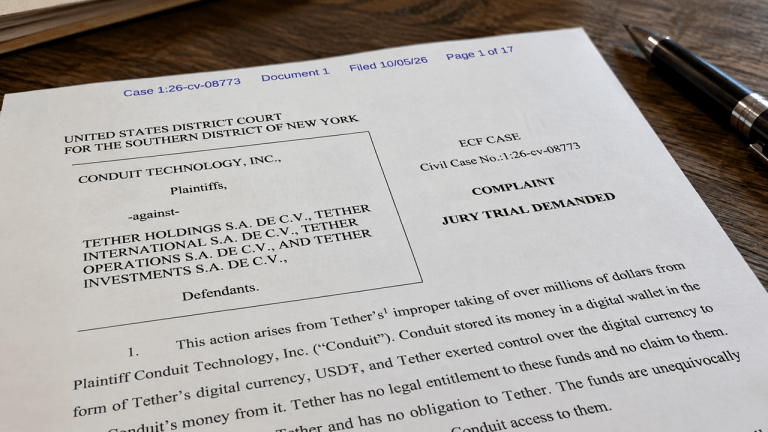
Conduit Sues Tether Over a $2.76M USDT Wallet Frozen for a Year
Conduit Technology has sued Tether after the stablecoin issuer froze $2.76 million in the company’s USDT and allegedly kept it loc...
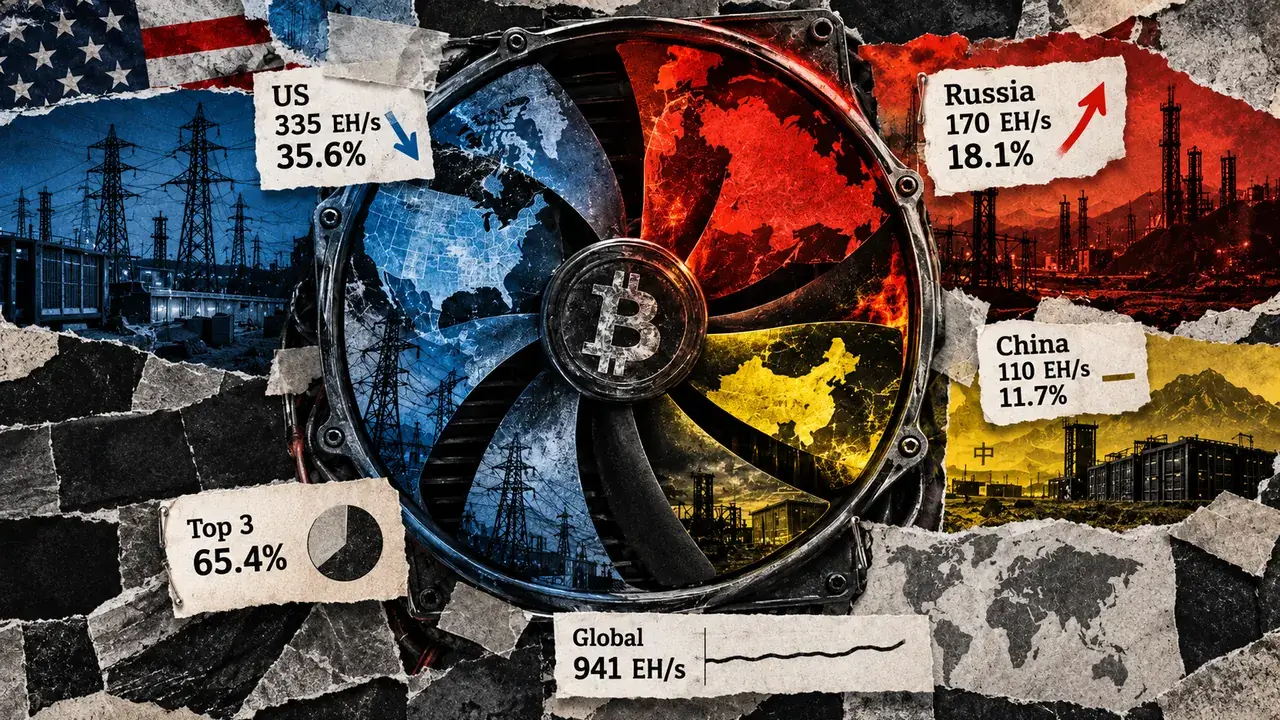
3 countries control 66% of Bitcoin mining, but 1 rival is gaining
Bitcoin's estimated US mining footprint shrank as Russia's grew, with little change in top-three country concentration. Hashrate I...
Fortitude Bets Up to $100 Million on Bitmain Zcash Mining Hardware
Fortitude Mining has signed a non-binding agreement for up to $100 million of Bitmain’s next-generation zcash mining hardware, sec...

Hyperscale Data Says Bitcoin And Cash Reserves Reach $56.4M
TL;DR Hyperscale Data says it held about $56.4 million in Bitcoin, cash and restricted cash as of October 4. That total included 2...