NPM Attack: Javascript Library Compromise Goes After Bitcoin Wallets
Bitcoin Magazine NPM Attack: Javascript Library Compromise Goes After Bitcoin Wallets A major NPM developer, qix, has had their account compromised. It was used to push malware that targets and searches for bitcoin and c...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Bitcoin Magazine
NPM Attack: Javascript Library Compromise Goes After Bitcoin Wallets
A major NPM developer, qix, has had their account compromised. It was used to push malware that targets and searches for bitcoin and cryptocurrency wallets on users devices. If detected, the malware would patch the code functions used to coordinate transaction signing, and replace the address a user is trying to send money to with one of the malware creator’s own addresses.
This should mostly be a concern for web wallet users, so in the Bitcoin ecosystem Ordinals or Runes/other token users, as unless an update for your normal software wallet happened to be pushed just earlier today with the compromised dependency, or if your wallet dynamically loads code directly from the wallet back end bypassing the app-store, you should be fine.
NPM is a package manager for Node.js, a popular Javascript framework. This means it is used to grab large sets of pre-written code used for common functionality to be integrated into different programs without the developer having to rewrite basic functions themselves.
The targeted packages were not cryptocurrency specific, but packages used by countless numbers of normal applications built with Node.js, not just cryptocurrency wallets.
If you are using a hardware wallet in combination with your web wallet, take extra care to verify on the device itself that the destination address you are sending too is correct before signing anything.
If you are using software keys in the web wallet itself, it would be advisable to not open them or transact until you are certain you are not running a vulnerable version of the wallet. The safest course of action would be waiting for an announcement from the team developing the wallet you use.
This post NPM Attack: Javascript Library Compromise Goes After Bitcoin Wallets first appeared on Bitcoin Magazine and is written by Shinobi.
Why this matters
This bitcoin story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on Bitcoin MagazineRelated market context

Your iPhone Duo Under Attack? Binance Flags Dangerous iOS Security Flaw
Binance has warned Apple users about a dangerous iOS vulnerability that could expose crypto wallets, private keys, and login crede...
Hackers hijack Ethersphere’s bee-js package and Swarm Desktop app to push wallet-stealing malware
The incident underscores the critical need for robust security measures in software supply chains, as trust in official channels i...
Bubblemaps alleges Solana trader Cupsey pulled $1.74 million through 30 linked wallets
The allegations highlight the risks of copy trading and underscore the need for transparency in crypto transactions to protect ret...
Ankr Bridge Exploit Sends $292K in Crypto to Attacker Through Five Fake Withdrawals
Key Takeaways: Blockaid reports that about $292,000 were stolen from Ankr’s Ethereum bridge through five suspicious withdrawals. T...
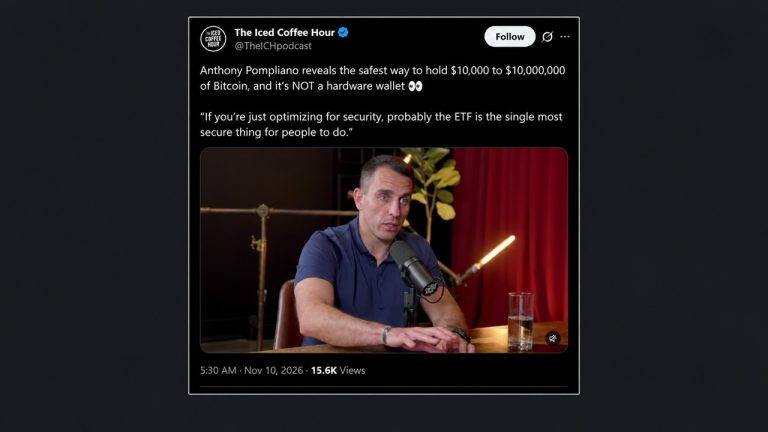
Pompliano Says a Bitcoin ETF Beats Hardware Wallets on Security
Anthony Pompliano says a spot bitcoin exchange-traded fund (ETF) is “the single most secure thing” for people holding $10,000 to $...
Genesis-era Ethereum wallet moves millions after a decade, scam attempts follow within minutes
The rapid scam attempts highlight the need for heightened security measures and vigilance in crypto transactions, especially for d...