Tokens created out of thin air may explain how $320 million in Bitcoin left the Liquid sidechain
Researchers examining the roughly $320 million Liquid Network incident have identified an alleged failure in the software’s transaction-validation cache, offering a more specific explanation for how unbacked tokens could...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
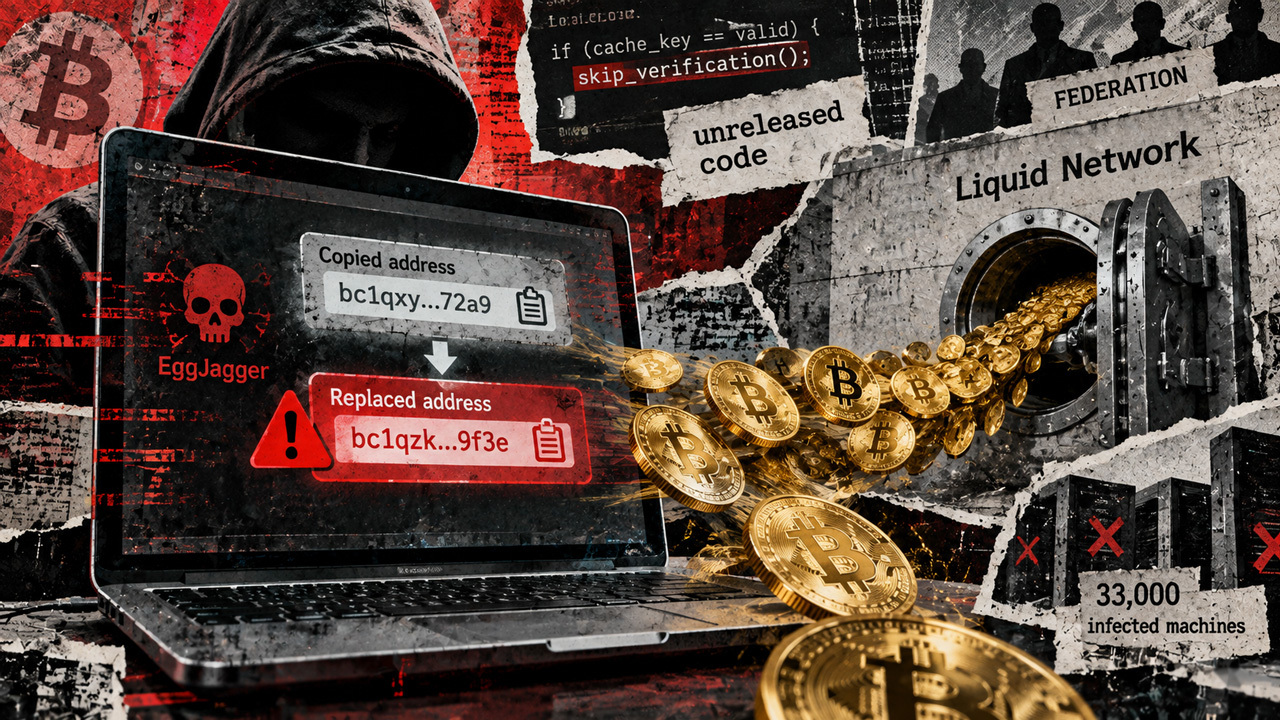
Researchers examining the roughly $320 million Liquid Network incident have identified an alleged failure in the software’s transaction-validation cache, offering a more specific explanation for how unbacked tokens could be redeemed for real Bitcoin.
Accounts also raise a deployment question. Mononaut said the exploited bug had entered Elements’ master development branch the previous week but had never appeared in a tagged release. Liquid’s federation functionaries apparently ran that code, he said, while other nodes rejected the invalid transactions.
That deployment account remains unconfirmed by Blockstream in the available statements. If established, it would put the software rollout at the center of an incident in which valid signing credentials authorized the release of Bitcoin against allegedly bug-created L-BTC.
Liquid is a Bitcoin sidechain whose L-BTC tokens are intended to be backed one-for-one by BTC held by its federation. As CryptoSlate previously reported, SideSwap said a customer submitted 4,000 L-BTC through its peg-out service on Sept. 6, prompting the release of approximately 3,996 BTC.
Related Reading A whitehat hacker is holding $320 million in drained Bitcoin until developers prove they patched a fatal network flawLiquid said neither SideSwap’s peg-out authorization key nor other federation keys had been compromised.
The emerging technical accounts focus on how the tokens reached that withdrawal process.
Calle described a flaw involving range proofs, which let nodes check that hidden transaction amounts fall within an allowed range without revealing those amounts.
Liquid’s confidential transactions require more than a check that inputs and outputs balance. A hidden negative output could otherwise offset a larger positive output, making newly created tokens appear to balance mathematically.
Range proofs are intended to prevent that outcome. Because checking them is computationally expensive, nodes cache successful verification results for reuse.
According to Calle’s account, the attacker could construct an invalid output and proof that matched the cache key associated with a previously valid check. A node finding that cached result would skip the verification that should have rejected the inflationary output.
Charles Guillemet endorsed the explanation, describing a crafted cache-key collision that allowed an invalid confidential transaction to bypass a range check. Calle cautioned that his account simplified the mechanism and could contain errors.
A separate transaction reconstruction by Stu identified setup transactions followed by an allegedly invalid transaction at Liquid block 4,050,336. Stu said the transaction created approximately 3,996.0183 L-BTC before the subsequent withdrawal through SideSwap.
Mononaut’s account adds a distinction between the nodes that accepted the transaction and those that did not.
He said federation functionaries accepted the exploit transactions, approved withdrawals, and continued building blocks. Other nodes, including those powering mempool’s Liquid explorer, rejected the affected block. That would explain why an explorer following the rejecting nodes could omit transactions visible elsewhere.
The reported divergence makes the affected software versions material to understanding the failure. A postmortem would need to establish which code functions ran, why it was deployed, and how its validation behavior differed from the nodes that rejected the block.
Meanwhile, the actors controlling the withdrawn Bitcoin have described themselves as whitehats and conditioned the return of most funds on the bug being fixed across affected nodes. The available reporting does not establish a completed return or patch rollout.
Recovering the Bitcoin would address the reserve shortfall. Explaining why federation nodes accepted the transactions and demonstrating that the corrected software rejects them would address the failure that allowed those reserves to leave.
The post Tokens created out of thin air may explain how $320 million in Bitcoin left the Liquid sidechain appeared first on CryptoSlate.
Why this matters
Bitcoin is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CryptoSlateRelated market context
Locked liquidity did not stop this $14 million crypto pool drain
The PancakeSwap pool for 79AU, 79thVault’s token, lost $14.35 million in USDT on Oct. 7 through two selling wallets, according to...
Circle minted another 750 million USDC on Solana in the last 24 hours
Increased USDC liquidity on Solana may boost SOL demand, but its market impact depends on active circulation and broader crypto tr...
Bitcoin holder loses 80 BTC worth $5.2 million after moving funds to reseller-bought Ledger
The incident underscores the critical importance of purchasing hardware wallets from official sources to ensure asset security. Th...
Securitize Puts 12 U.S. Stocks on Solana With 1:1 Backing and 24/7 Trading Plans
Key Takeaways: Securitize has already launched tokenized U.S. stocks on Solana, including NVIDIA, Tesla and Apple. Each token repr...
OpenAI, Google and Meta battle for AI internet domains as crypto firms target .bitcoin and .wallet
OpenAI, Google, and Meta are competing for AI-related internet domains as cryptocurrency firms pursue their own digital naming rig...
Tether freezes USDT linked to Ledger user thefts near $90 million
The freeze highlights the need for robust supply chain security and raises concerns about the limitations of centralized control i...