Unpatched Eclair Bitcoin Lightning nodes could crash again every time they restart
A newly disclosed unfunded-channel flaw could leave Eclair, a Bitcoin Lightning implementation, crashing repeatedly without an attacker spending BTC on-chain. The flaw affected reachable nodes running v0.14.0 and earlier...
Watchlist
Fresh in the current trading session. A tracked entity is involved.
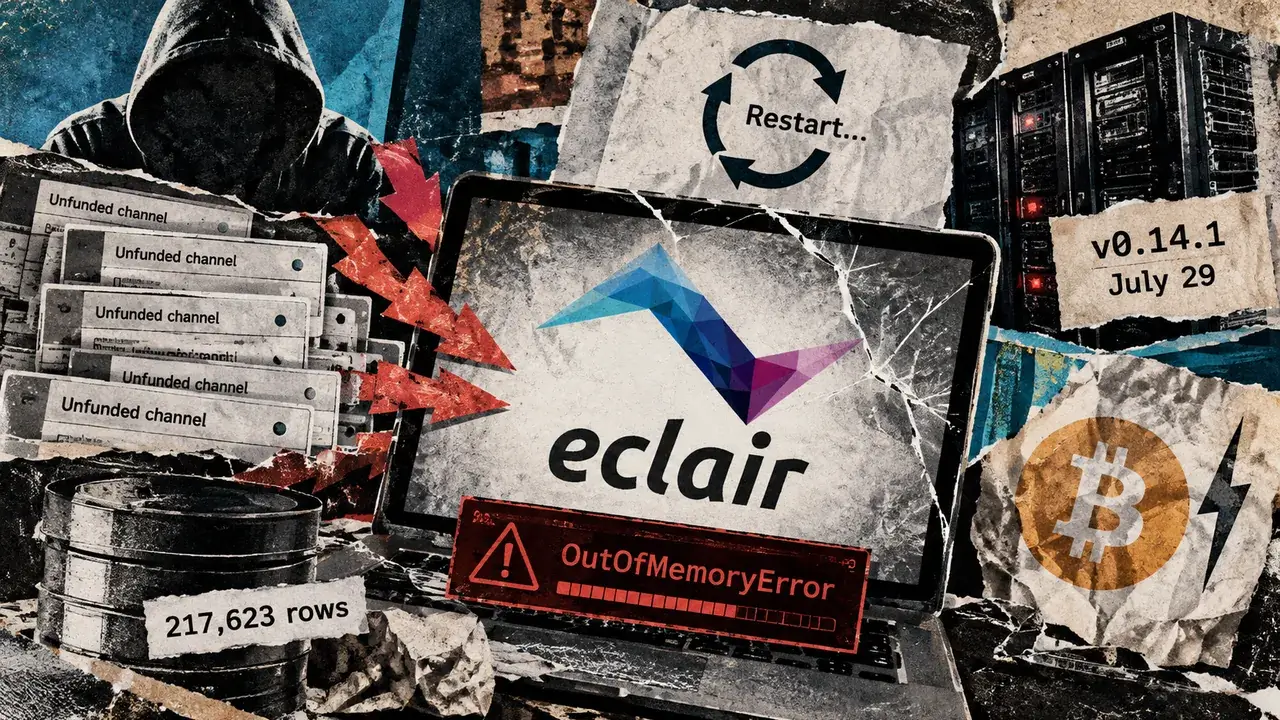
A newly disclosed unfunded-channel flaw could leave Eclair, a Bitcoin Lightning implementation, crashing repeatedly without an attacker spending BTC on-chain. The flaw affected reachable nodes running v0.14.0 and earlier, with saved channel records making a restart insufficient to restore service.
Researcher Erick Cestari published the persistent-crash finding Sept. 30 and explained it alongside a separate denial-of-service bug in an Oct. 1 developer post. Both were fixed in v0.14.1, released in July, before the public disclosures. ACINQ now recommends the later v0.14.3 security release for separate vulnerabilities.
Why restarting could failEclair limited the number of pending channels a peer could open, but inconsistent checks of temporary and final channel identifiers let its counter undercount unfunded channels. A malicious peer could accumulate saved requests without broadcasting the funding transaction or paying an on-chain fee.
That distinction matters: the BTC normally needed to fund a channel did not have to be committed for the vulnerable node to incur memory and database costs. The attack still required computing resources and network traffic.
In Cestari’s proof of concept, Eclair v0.14.0 ran in regtest, Bitcoin’s local testing environment. He reported that the node exhausted a 4 GB Java virtual machine heap after about 47 minutes 43 seconds, with 217,623 rows accumulated in the channel database. That is one laboratory benchmark, not a universal attack duration.
Related Reading Critical Bitcoin Lightning bugs exposed nodes to fund theft and restart failureThe initial crash left those records on disk. During startup, Eclair reloaded the channels and exhausted memory again. Cestari described increasing the heap or manually removing fake channel records as recovery measures. Repeated restarts left the underlying load in place.
The demonstration concerns one vulnerable node’s availability. It does not establish live exploitation or the number of unpatched nodes.
ACINQ merged PR #3324 July 17. The patch strengthened duplicate-channel checks, and v0.14.1 shipped July 29. According to Erick Cestari / Delving Bitcoin, v0.14.0 and earlier are affected, while v0.14.1 or later addresses these two denial-of-service findings.
Related Reading Core Lightning patches flaw that could let revoked channel state escape penaltyThe second bug, disclosed by Matt Morehouse / lnfuzz as LNF-2026-0003, was a channel-opening race that left orphaned channel processes consuming memory or CPU. His advisory says the tested node recovered on disconnect or restart without loss. That recovery result belongs to the race bug, rather than the persistent database flood.
Related Reading A Bitcoin Lightning flaw could send a node’s entire balance straight to minersThese findings also differ from the fund-loss vulnerabilities CryptoSlate covered Sept. 21, which were patched in v0.14.3. The July minimum fix should therefore not be read as a complete current security recommendation.
ACINQ recommends upgrading to v0.14.3, released Sept. 14, because malicious nodes could exploit some of the issues it fixed. Preventing new unfunded-channel floods and recovering an already overloaded database are separate operator concerns.
The post Unpatched Eclair Bitcoin Lightning nodes could crash again every time they restart appeared first on CryptoSlate.
Why this matters
Bitcoin is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CryptoSlateRelated market context
Electrum patches Lightning flaw, but old Bitcoin backups break
Electrum’s latest security update fixes a Lightning backup defect, but some Bitcoin wallet users still need to replace saved backu...
MetaMask Exits Ethereum Validators After Security Incident Hits Staking Infrastructure
Key Takeaways: MetaMask is addressing a security incident to its infrastructure of which it is unaware. According to the company,...
MetaMask Pulls Its Staking Validators After a Security Incident Hits Its Infrastructure
MetaMask is taking the Ethereum validators run by its staking business offline after what it described on Wednesday as “an ongoing...
PropAMMs lower Solana trade costs, and public pool returns crash
A trader can get a better Solana (SOL) swap price while a passive pool depositor remains exposed to traders picking off stale quot...
MetaMask security scare pushes Ethereum validator exits to a nine-month high
MetaMask is pulling thousands of Ethereum validators after a security breach redirected rewards, creating a network-wide backlog f...
MetaMask says no user funds were hit in validator security incident
The incident highlights the vulnerability of staking infrastructures, emphasizing the need for robust security measures to protect...