Harmony weighs a full blockchain rollback after unauthorized minting floods exchanges with billions in ONE
Harmony, the layer-1 blockchain network, has released an emergency validator patch that it says prevents further unauthorized minting of ONE, its native token. The project said it will address tokens already created in a...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
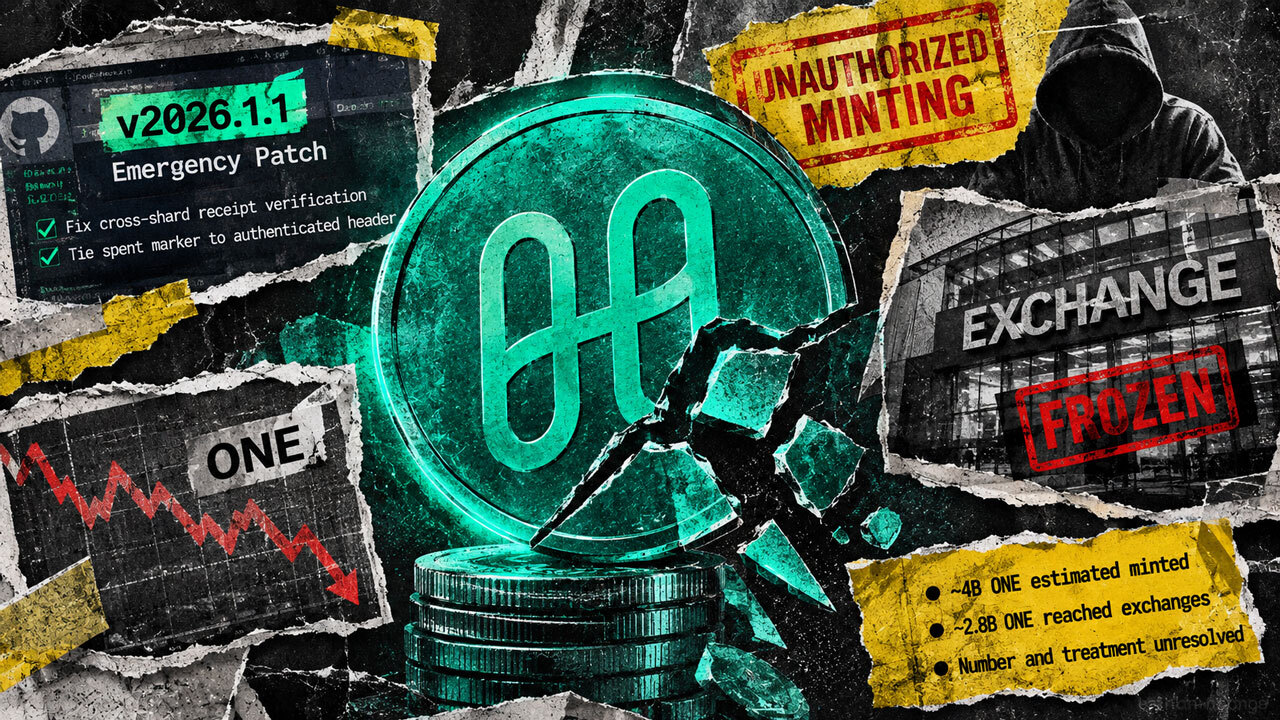
Harmony, the layer-1 blockchain network, has released an emergency validator patch that it says prevents further unauthorized minting of ONE, its native token. The project said it will address tokens already created in a later update, leaving their number and ultimate treatment unresolved.
Harmony told validators to install v2026.1.1 on Aug. 12. The notice confirms that minting occurred but does not disclose the amount.
Onchain researcher Juiceberg estimated that roughly 4 billion ONE, equal to about 26% of the supply figure used in the post, had been minted without authorization. Juiceberg also estimated that 2.8 billion ONE had reached exchanges. Harmony has not independently confirmed those figures.
Related Reading Polkadot Hyperbridge April Fools’ joke comes true as over 1 Billion fake DOT tokens were minted on Ethereum A proof replay bug let the attacker mint over $1 billion DOT tokens on Ethereum, yet shallow DOT pools capped the cashout near $240,000. Apr 13, 2026 · Oluwapelumi Adejumo How the patch blocks more mintingHarmony's published code changes address two weaknesses in cross-shard receipts, which carry transaction results between parts of the network.
One flaw allowed an empty signer record and a mathematically neutral aggregate signature to pass a quorum check. The verifier counted the full committee instead of the validators represented in the signer record, allowing a receipt to be accepted without the required approvals.
The second flaw affected how the network recorded that a receipt had already been spent. Some proof fields were not bound to the signed block header, so changing those fields could make a previously processed receipt appear new. The destination could then be credited again without a corresponding debit from the source.
Related Reading Crypto users told to pull funds after Ethereum L2 bridge failure exposes rollup exit risk The incident forced users to confront the part of rollup security that usually stays invisible: whether they can still withdraw when the bridge layer breaks. Jun 23, 2026 · Liam 'Akiba' WrightThe signed v2026.1.1 release changes the quorum calculation and ties the spent marker to authenticated header data, closing both paths described in the patch.
Harmony also paused bridge.harmony.one during the response, although its notice did not identify the bridge as the exploited component. The project published four implicated wallet addresses and asked exchanges to block and freeze traceable funds, without naming the venues or disclosing how much had been frozen.
Harmony's initial response said rollback options were under consideration. The project has not announced that a rollback will occur or specified the point from which transactions could be reversed.
The incident differs technically from the June 2022 Horizon bridge exploit, which involved compromised multisig control and about $100 million in stolen assets. The current patch instead addresses receipt verification and replay at the protocol level.
Related Reading North Korea’s Lazarus Group linked to $100M Harmony exploit Elliptics says the strategies employed for the Harmony exploit are consistent with the ones used for the Ronin Bridge exploit a few months ago. Jun 30, 2022 · Oluwapelumi AdejumoHarmony says further minting is now blocked. The remaining risk centers on the size and location of the ONE already created, how much exchanges can freeze, and whether the network will attempt a rollback to remove the excess supply.
The post Harmony weighs a full blockchain rollback after unauthorized minting floods exchanges with billions in ONE appeared first on CryptoSlate.
Why this matters
Ethereum is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CryptoSlateRelated market context

Ondo Unlocks $3.6B Tokenized Market With Direct Stock-to-Token Conversions
Key Takeaways: Ondo Finance has now introduced the ease of converting legacy shares into tokenized stocks and ETFs for approved in...
Solana flips Ethereum in fees, while ETH holds the burn lead
Solana generated more user fees than Ethereum in data provider DefiLlama's Sept. 22 dashboard snapshot, while Ethereum burned more...

Ethereum ETFs Pull In $270M As BlackRock Leads September 21 Rebound
TL;DR US spot Ethereum ETFs recorded $270.0 million of net inflows for the September 21 session. BlackRock’s ETHA led the day with...
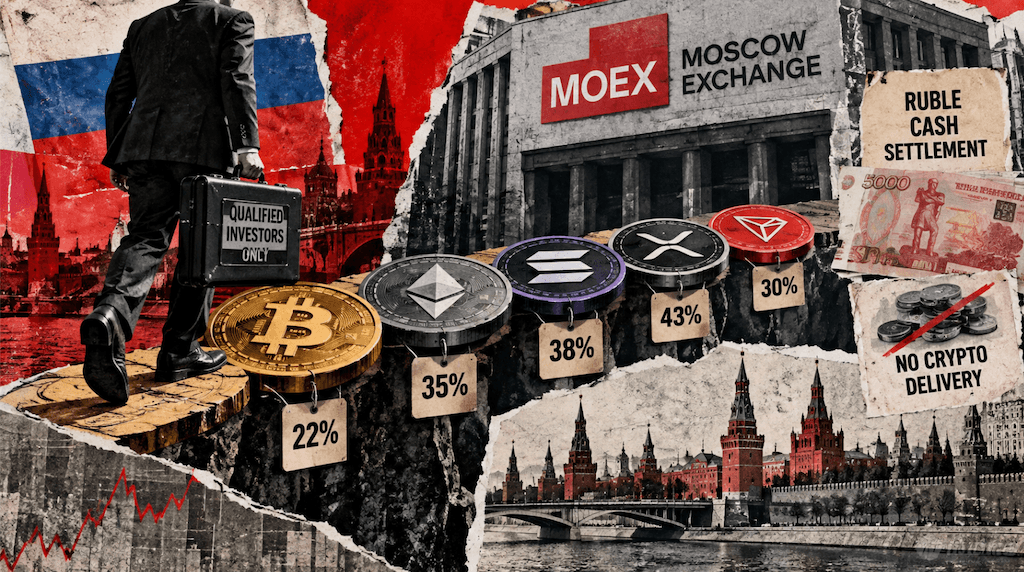
Moscow Exchange launches 5 crypto perpetual futures as demand tops 600 billion rubles
Moscow Exchange will launch perpetual futures tied to five major cryptocurrencies on Sept. 22, giving qualified investors continuo...
Crypto Got Its Rulebook Without Congress, Chris Perkins Says
The CLARITY Act stalled in the Senate on Sept. 15, when a motion to take it up drew 49 votes to 50, 11 short of the 60 it needed a...
Vitalik Buterin Backs Trueo's Ethereum Move As TRUE Jumps 900%
Vitalik Buterin endorsed a prediction market by name on Monday, welcoming Trueo's plan to move its primary deployment from Base to...