CrowdStrike and federal authorities dismantle Russian malware that secretly stole crypto for 8 years
Russia-based Sality watched for copied bitcoin and Ethereum addresses and quietly replaced them with the attacker’s. CrowdStrike and law enforcement have now isolated more than 15,000 infected machines.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Why this matters
Bitcoin is a tracked market entity in the DigitalMoneyBox archive, making this useful context for readers monitoring repeated mentions and follow-up coverage.
Original source
Read on CoinDeskRelated market context
Dormant Ethereum address holding 12,746 ETH wakes up after 10.2 years
The reactivation of dormant Ethereum wallets highlights potential market shifts, as early holders may choose between selling or st...
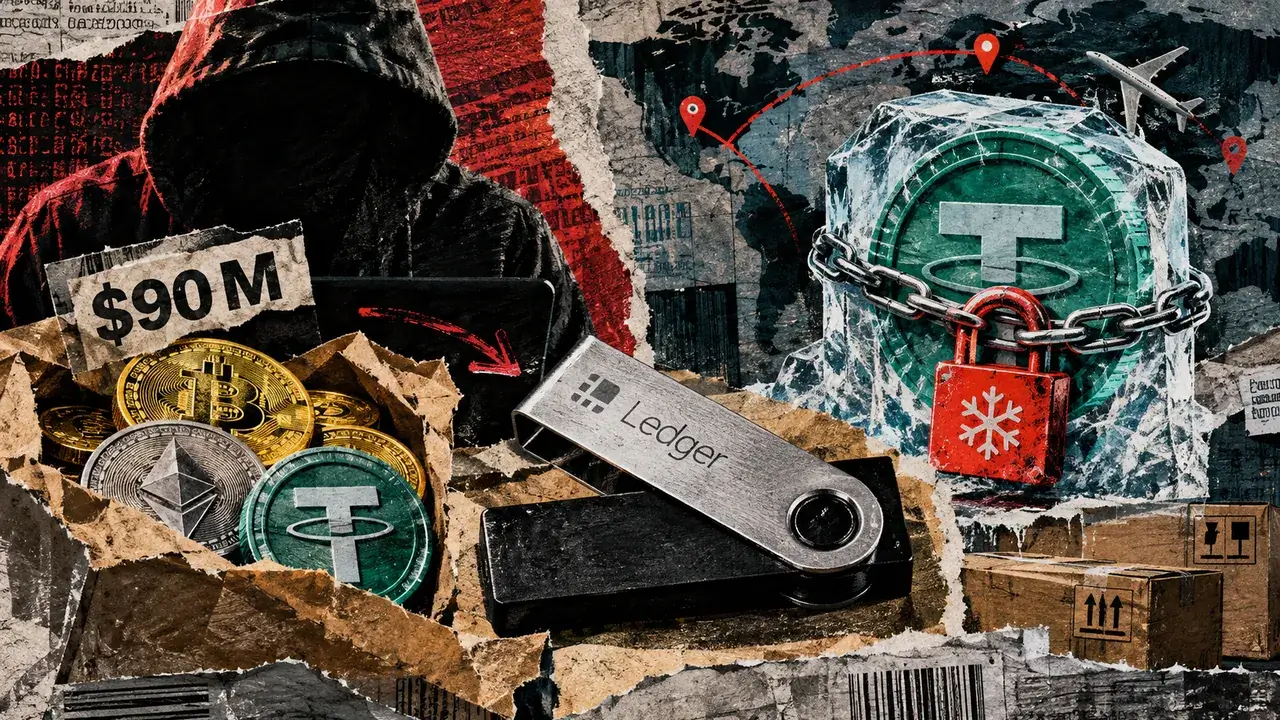
Ledger hack scare nears $90 million as Tether moves to freeze stolen USDT
Suspected Ledger wallet thefts are approaching $90 million as Tether freezes USDT stablecoin linked to the incident, according to...

AI Could Weaken Ethereum Security as Cryptographic Risks Grow, Vitalik Buterin Warns
Buterin urged developers to prepare for potential AI vulnerabilities in both conventional and quantum-resistant cryptography, whil...
Ethereum ETFs see largest weekly net outflow since January
The significant outflows from Ethereum ETFs may signal waning investor confidence and broader bearish sentiment in the crypto mark...
Stealing $1.5B in crypto is easy, cashing out is the trap
North Korean hackers stole around $1.5 billion from Bybit in February 2025. While the hack itself has been widely covered and anal...
STRK rallies as Starknet weighs a move from Ethereum layer 2 to its own layer 1
Starknet's potential shift to layer 1 could redefine blockchain security priorities, challenging Ethereum's timeline and reshaping...