DeadLock ransomware hides using exploited Polygon smart contracts
Group-IB found a ransomware dubbed DeadLock that is exploiting Polygon smart contracts to rotate proxy addresses to evade takedowns.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Group-IB found a ransomware dubbed DeadLock that is exploiting Polygon smart contracts to rotate proxy addresses to evade takedowns.
Why this matters
This maps to the Security Incidents hub, so it can help confirm whether that theme is gaining breadth across the crypto news cycle.
Original source
Read on CointelegraphRelated market context

S&P Global Agrees To Acquire Smart Contract Security Firm OpenZeppelin
TL;DR S&P Global has agreed to acquire OpenZeppelin. OpenZeppelin is one of the best-known smart contract security and auditing fi...
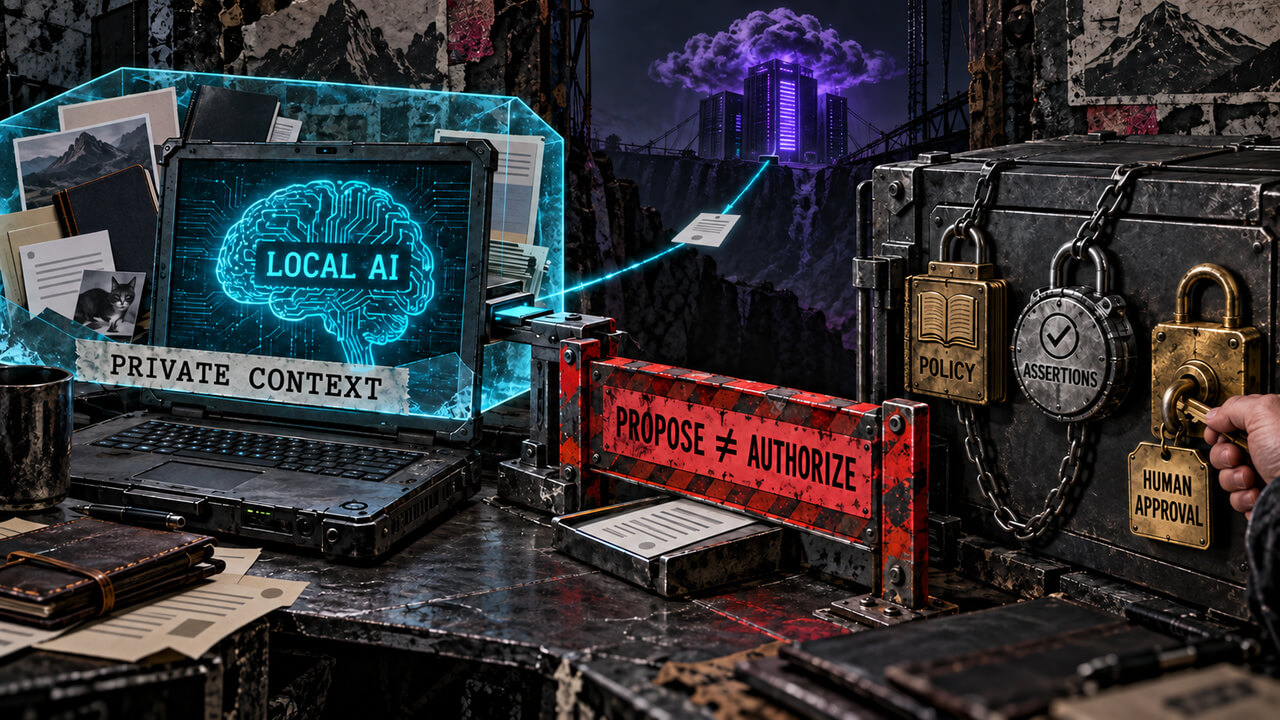
Ethereum co-founder Vitalik Buterin argues that local AI can protect your privacy without losing speed
Ethereum co-founder Vitalik Buterin says laptop AI is approaching a practical turning point. Wallet software still needs a much hi...
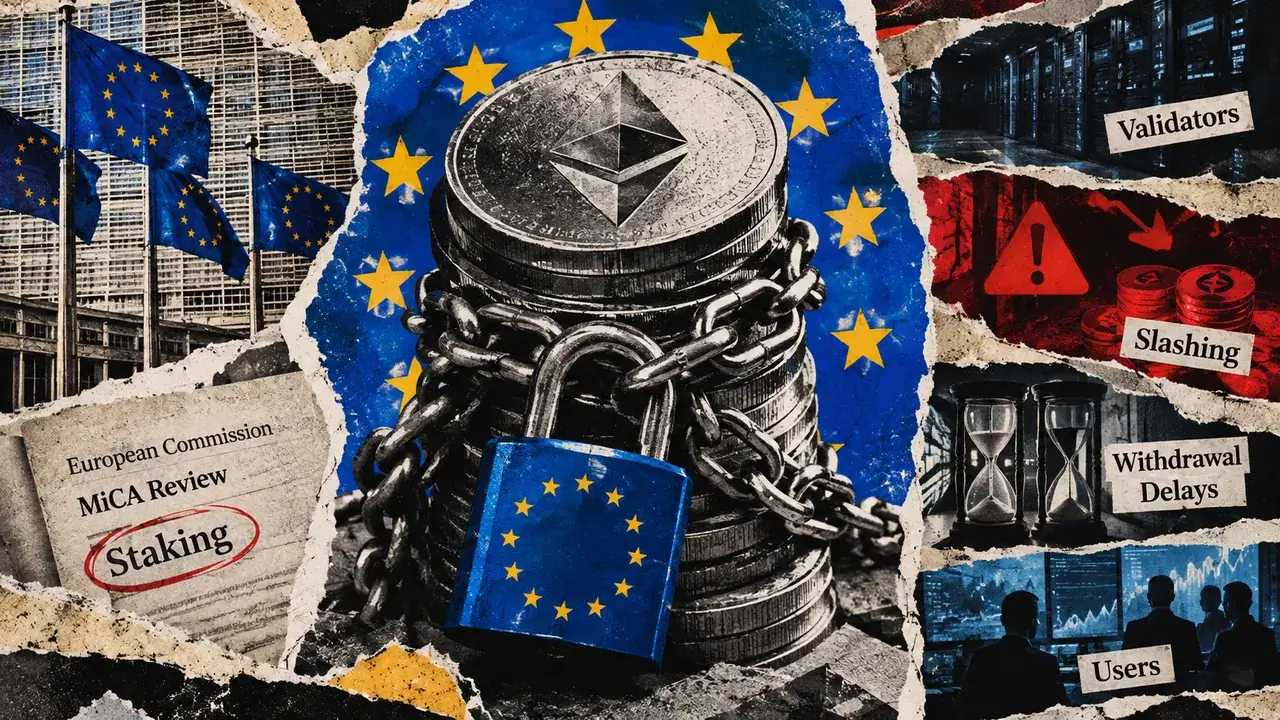
EU staking review threatens crypto yields and network security could pay the price
Some of the most consequential financial rules begin with surprisingly little text. For example, on page 36 of the European Commis...
S&P Global Agrees to Buy OpenZeppelin and Fold Smart Contract Audits Into Ratings
S&P Global announced on Thursday that it has agreed to acquire OpenZeppelin, the smart contract security firm, and will run it as...
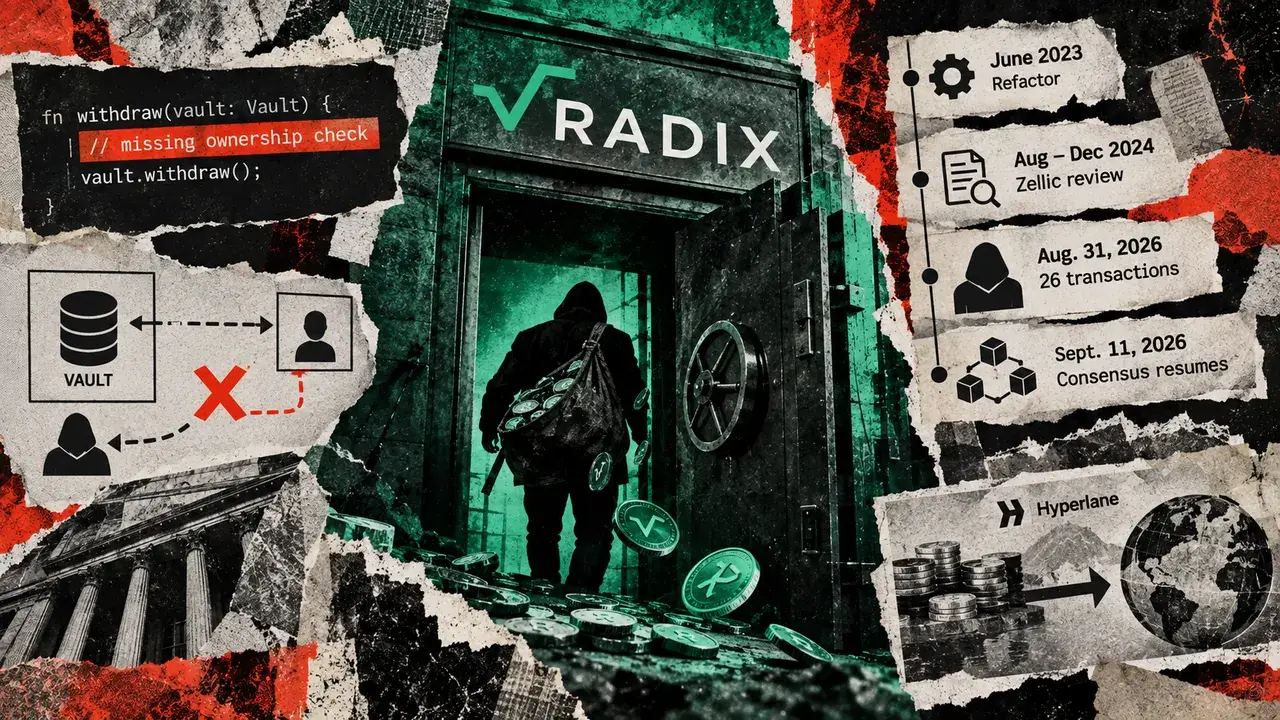
3-year-old bug triggers $1.3 million drain and forces 10-day blockchain halt
A routine Radix code refactor created a vault flaw that enabled a roughly $1.3 million theft and later forced validators to halt t...
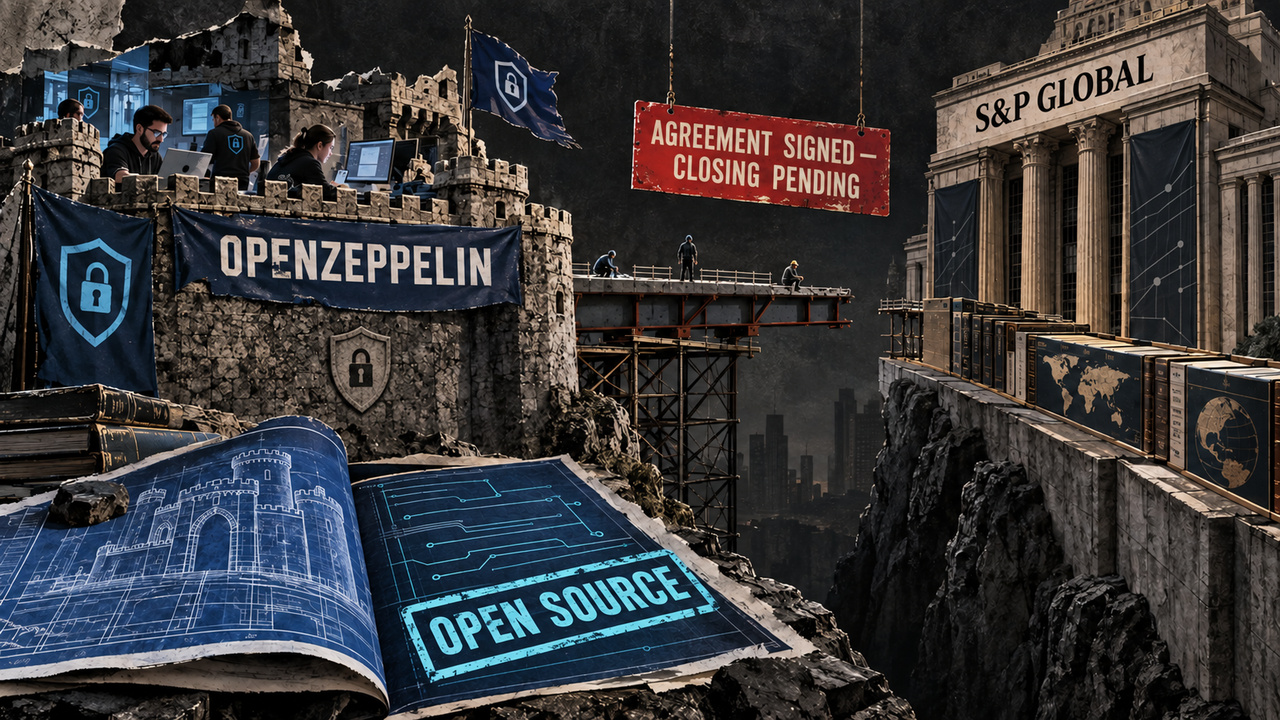
Wall Street gains direct oversight of Web3 security as S&P Global buys OpenZeppelin
S&P Global has agreed to acquire smart contract security company OpenZeppelin in a transaction that would put the crypto company i...