Lazarus used ‘Kandykorn’ malware in attempt to compromise exchange — Elastic
Lazarus members posed as engineers and fooled exchange employees into downloading difficult-to-detect malware.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.

Lazarus members posed as engineers and fooled exchange employees into downloading difficult-to-detect malware.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context
Glassnode co-founder counts 6.26 million BTC with exposed public keys
Rising exposure of Bitcoin public keys heightens security concerns, especially with quantum computing threats, urging exchanges to...
Papertrade draws $3B in Bitcoin open interest as on-chain perps exchange launches
The launch of Papertrade could reshape crypto trading dynamics, emphasizing leverage and risk, potentially impacting market stabil...
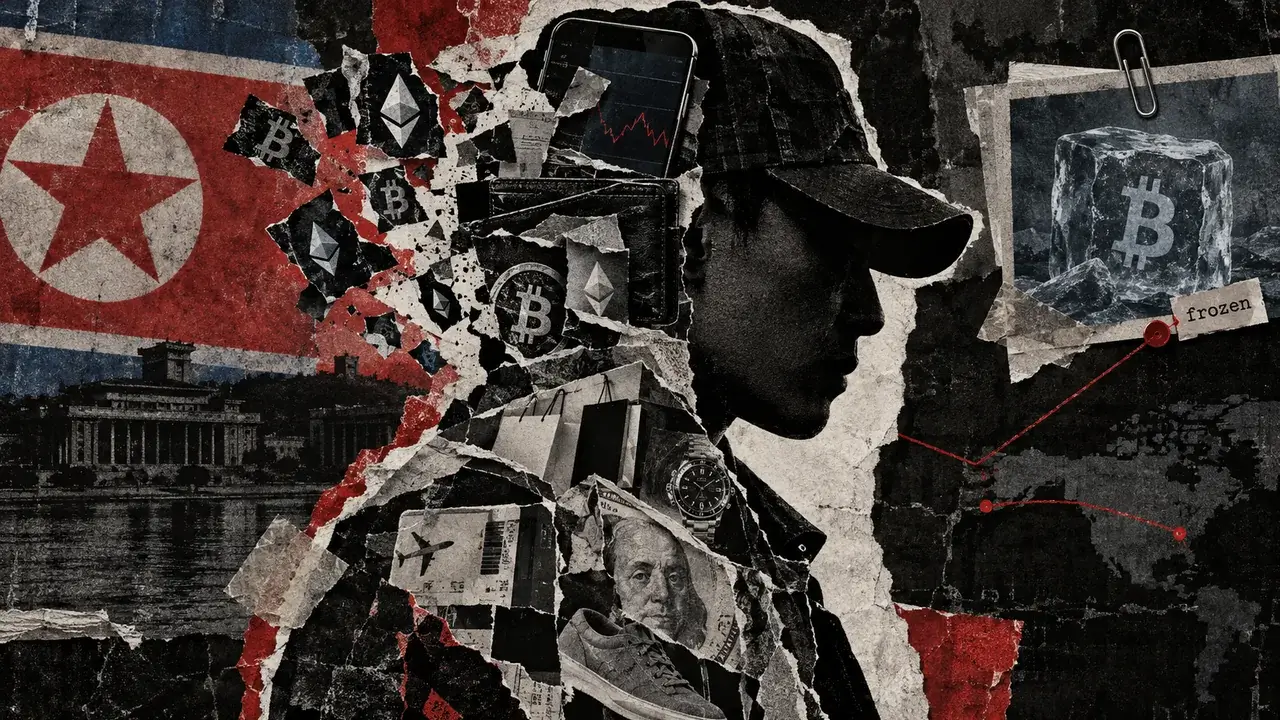
Stealing $1.5B in crypto is easy, cashing out is the trap
North Korean hackers stole around $1.5 billion from Bybit in February 2025. While the hack itself has been widely covered and anal...
Hyperliquid surpasses $1B revenue, $1B used for HYPE buybacks
Hyperliquid's strategic buybacks enhance HYPE's market value, reflecting strong financial health and boosting investor confidence...
Ledger hack scare nears $90 million as Tether moves to freeze stolen USDT
Suspected Ledger wallet thefts are approaching $90 million as Tether freezes USDT stablecoin linked to the incident, according to...
UK sanctions three crypto exchanges tied to Russian illicit funds
The UK sanctioned crypto exchanges and payment processors, some of which were tied to thousands of Russian entities and the sancti...