Ledger scammers are sending letters to steal seed phrases
Scammers are mailing physical letters to the owners of Ledger crypto hardware wallets asking them to validate their private seed phrases in a bid to access the wallets to clean them out.In an April 29 X post, tech commen...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
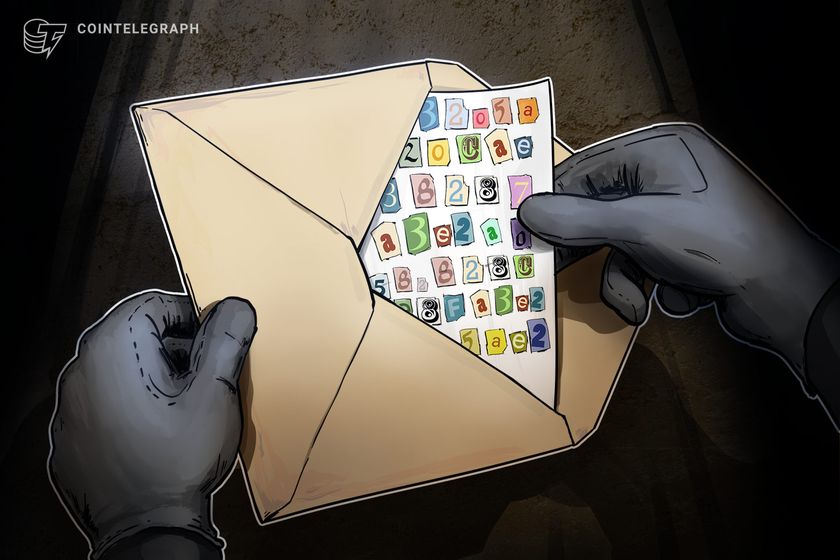
Scammers are mailing physical letters to the owners of Ledger crypto hardware wallets asking them to validate their private seed phrases in a bid to access the wallets to clean them out.
In an April 29 X post, tech commentator Jacob Canfield shared a scam letter sent to his home via post that appeared to be from Ledger claiming he needed to immediately perform a “critical security update” on his device.
The letter, which uses Ledger’s logo, business address, and a reference number to feign legitimacy, asks to scan a QR code and enter the wallet’s private recovery phrase under the guise of validating the device.
The letter threatens that “failure to complete this mandatory validation process may result in restricted access to your wallet and funds.”
A seed phrase, or recovery phrase, is a string of up to 24 words that unlocks access to a crypto wallet. A scammer with the phrase can access and control the associated wallet to transfer its holdings elsewhere.
Earlier this month, the X account of a crypto hardware wallet reseller said it had also received multiple reports of Ledger users receiving a similar letter.
In response to Canfield’s post, Ledger said the letter is a scam and cautioned its device users to stay vigilant against phishing attempts.
Related: Ledger wallet user reports 10 BTC loss — Community blames phishing
“Ledger will never call, DM [direct message], or ask for your 24-word recovery phrase. If someone does, it's a scam,” it added.
“Please don't engage with accounts claiming to be Ledger employees or anyone offering to help recover funds.”Unclear whether connected to the Ledger’s data leakCanfield suggested that scammers were sending letters to Ledger customers whose data was leaked nearly five years ago.
In July 2020, a hacker breached Ledger’s database and dumped the personal information of more than 270,000 of its customers online, which included names, phone numbers and home addresses
The following year, several Ledger users claimed to have been mailed fake Ledger devices that were tampered with and designed to install malware upon use, Bleeping Computer reported at the time.
Magazine: Your AI ‘digital twin’ can take meetings and comfort your loved ones
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context

WaterPlum Targets 30,000 Devices and Steals 7,000+ Crypto Wallet Records Worldwide
Key Takeaways: WaterPlum hacked over 30,000 devices in 100+ countries and accessed information from 7,000+ crypto wallets. Fake jo...

Binance Wallet Opens $4.7T Pre-IPO Market Access Through PancakeSwap Tokenized Deals
Key Takeaways: Binance Wallet now provides eligible users a chance to participate in PancakeSwap Pre-Access campaigns for tokenize...
Binance Wallet launches Pre-Access campaigns for tokenized pre-IPO exposure via PancakeSwap
Binance's Pre-Access campaigns could democratize early investment opportunities, potentially reshaping retail investor access to p...
Why keeping your private keys safe won’t always stop crypto theft
Almost 4,000 Bitcoin left Liquid's reserve on Sept. 6 through a withdrawal the network approved, even though the private keys used...
X brings crypto trading closer to your social feed
Crypto Twitter (now X) has always been a place where someone with an illustrated animal for a profile picture can explain why your...

WisdomTree And MoonPay Expand US Access To Tokenized Funds
TL;DR WisdomTree is integrating MoonPay into its tokenized-fund platform. MoonPay says its ecosystem reaches more than 30 million...