Litecoin Postmortem: MWEB Bug Let Attacker Fake 85,034 LTC Pegout Before Devs Froze Funds
Litecoin developers published a postmortem on Tuesday confirming two related security incidents tied to a critical Mimblewimble Extension Block validation bug that allowed an attacker to fabricate an 85,034 LTC pegout in...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.

Why this matters
Litecoin is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on Bitcoin NewsRelated market context
Hackers mint trillions in fake Bitcoin, but 15 BTC bridge recovery leaves liquidity providers unpaid
Cross-chain protocol Symbiosis said it recovered approximately 15 BTC after an attacker exploited its native Bitcoin Bridge, but a...

Blockstream bets 600 Bitcoin by rejecting Liquid hacker’s $50 million bounty demand
Blockstream is refusing to pay the Liquid attacker nearly 600 Bitcoin (roughly $50 million), escalating a dispute over how the cry...
Audited DeFi protocols lost $885M to attacks that occurred completely outside their audit scopes
In decentralized finance, “audited” is often presented as a verdict on an entire project. In practice, an audit usually covers nam...

Revolut Customer Records Exposed: Attackers Demand 10,000 BTC
Revolut disclosed sensitive customer records to an unauthorized party after fraudulent data requests arrived from an email address...
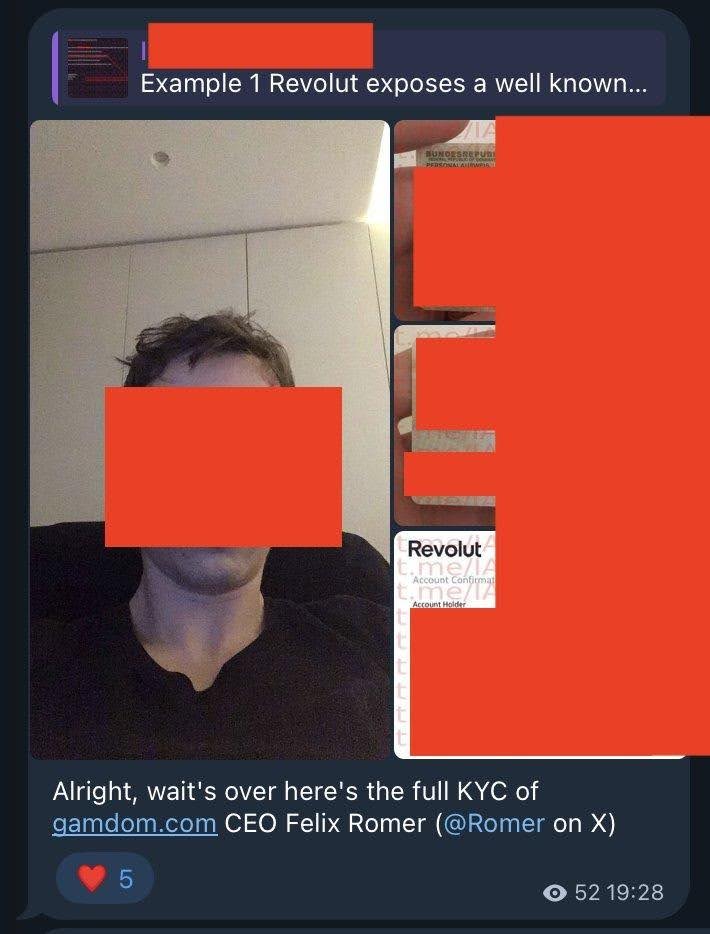
Revolut Crypto Data Leak Exposes Bitcoin Records, Attackers Demand Payment to Stop More
Key Takeaways: Hackers have reportedly begun to share personal data on the affected customers and ask for money to prevent more le...
Symbiosis says it recovered 15 BTC after Bitcoin bridge exploit, offers attacker 20% bounty
Blockchain security firm Blockaid said roughly 46.1 billion syBTC were minted but the attacker realized only about $336,000 in pro...