MacOS malware hijacks Telegram sessions, targets crypto wallets: SlowMist
A macOS malware steals credentials to hijack Telegram sessions, decrypt cryptocurrency wallets or trick users into entering their wallet recovery phrases through fake applications.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
A macOS malware steals credentials to hijack Telegram sessions, decrypt cryptocurrency wallets or trick users into entering their wallet recovery phrases through fake applications.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context
Binance hacker splits $1.4 billion of bitcoin into 19 wallets that no one can freeze
All 18,270 coins sit in 19 wallets, 17 of them holding exactly 1,000 BTC each, and none has moved since Thursday night, a CoinDesk...
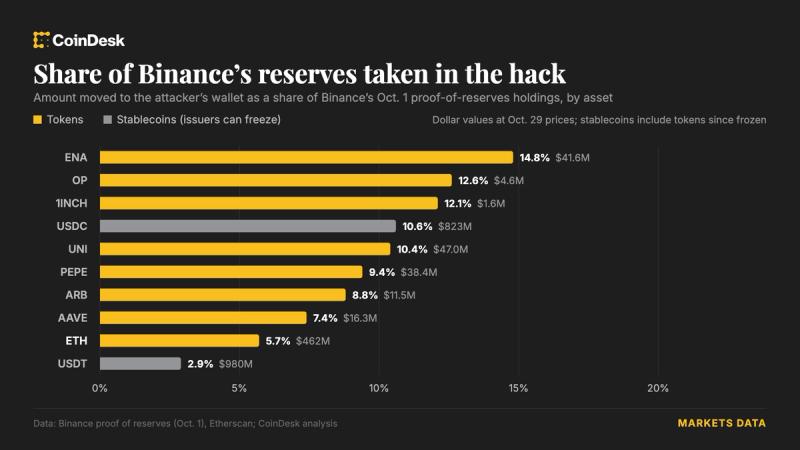
Binance hack drained wallets backing customer assets, reserve data shows
Binance’s own reserve data lists the drained wallets as backing customer balances, leaving its ether backing an estimated 6% short...
MANTRA brings Privy embedded wallets to its RWA apps
MANTRA's integration of Privy's non-custodial wallets could accelerate mainstream adoption of tokenized real-world assets by simpl...
Binance Says User Funds Are ‘Completely Safe’ After $3.5 Billion Drains From Its Hot Wallets
Binance said on X that “user funds are completely safe” after wallets Etherscan labels as Binance hot wallets sent billions of dol...
Binance Founder Suggests Likely Hack as Billions in Crypto Leaves Exchange Wallets
Billions of dollars’ worth of cryptocurrency was pulled from the wallets of leading exchange Binance on Thursday, according to onc...
BNB falls as much as 9% after reports of $2.77 billion leaving Binance wallets
Market volatility and trust issues may escalate if Binance doesn't clarify the massive outflows, impacting broader crypto stabilit...