New Malware Exploits Fake Job Ads to Hit Crypto Wallets on Windows, Mac, Linux
A newly discovered cross-platform malware dubbed ModStealer is slipping past antivirus systems and targeting crypto wallets on Windows, macOS, and Linux, according to researchers at Apple device security firm Mosyle. Key...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
A newly discovered cross-platform malware dubbed ModStealer is slipping past antivirus systems and targeting crypto wallets on Windows, macOS, and Linux, according to researchers at Apple device security firm Mosyle.
Key Takeaways:
- ModStealer malware is evading antivirus detection and targeting crypto wallets across Windows, macOS, and Linux.
- The malware spreads via fake job ads and extracts private keys, credentials, and wallet data.
- Researchers warn that ModStealer is part of a growing Malware-as-a-Service trend.
ModStealer has remained undetected by major antivirus engines since it was first uploaded to VirusTotal nearly a month ago, 9to5Mac reported on Thursday.
The malware is being distributed through fake job recruiter ads aimed at developers, a growing tactic among cybercriminals.
Victims Tricked into Running Malicious JavaScript FileVictims are tricked into running a malicious JavaScript file written in NodeJS, which avoids detection by traditional signature-based defenses.
Unlike more basic infostealers, ModStealer comes loaded with features designed for stealth and scale.
It targets 56 browser-based crypto wallet extensions, including those on Safari, and is capable of extracting private keys, credentials, configuration files, and certificates.
Clipboard and screen capture tools are also embedded, alongside remote code execution, which can give attackers near-total control of an infected device.
On macOS, the malware uses Apple’s launchctl tool to gain persistence by embedding itself as a LaunchAgent.
From there, it silently monitors activity and sends data to a remote server believed to be hosted in Finland but routed through German infrastructure.
Fake paid ads
Scam ads are seemingly-real ads on Twitter and Google that advertise fake giveaways and airdrops. Their goal is to trick you into connecting your wallet and signing malicious transactions.
NEVER use links in paid ads or search results to access airdrops! pic.twitter.com/MoFJbgp345
Researchers believe ModStealer is part of a growing Malware-as-a-Service (MaaS) ecosystem, where advanced malware packages are sold to affiliates who deploy them without needing technical expertise.
This mirrors a wider trend in the cybercrime space: infostealers now dominate Mac malware, with Jamf reporting a 28% surge in such threats in 2025 alone.
The implications for crypto users are especially severe, given the malware’s focus on wallet extensions and sensitive blockchain credentials.
“This isn’t just a Mac issue anymore,” said Mosyle in a statement. “The cross-platform nature of ModStealer, combined with its stealth and MaaS distribution model, represents an evolving threat to developers, traders, and enterprises alike.”
With its focus on evading antivirus systems, the campaign highlights the need for more advanced, behavior-based security solutions.
Investor Loses $3M in Crypto Phishing ScamAs reported, a cryptocurrency investor has fallen victim to a phishing scam, losing $3.05 million in Tether (USDT) after unknowingly signing a malicious blockchain transaction.
The loss, flagged by blockchain analytics platform Lookonchain on Wednesday, underscores the rising threat of phishing attacks targeting digital asset holders.
The attacker exploited a common habit among crypto users: validating only the first and last few characters of a wallet address while ignoring the middle.
Crypto investors lost over $2.2 billion to hacks, scams, and breaches in the first half of 2025, driven largely by wallet compromises and phishing attacks, according to CertiK’s latest security report.
Wallet breaches alone caused $1.7 billion in losses across just 34 incidents, while phishing scams accounted for over $410 million across 132 attacks.
The post New Malware Exploits Fake Job Ads to Hit Crypto Wallets on Windows, Mac, Linux appeared first on Cryptonews.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CryptonewsRelated market context
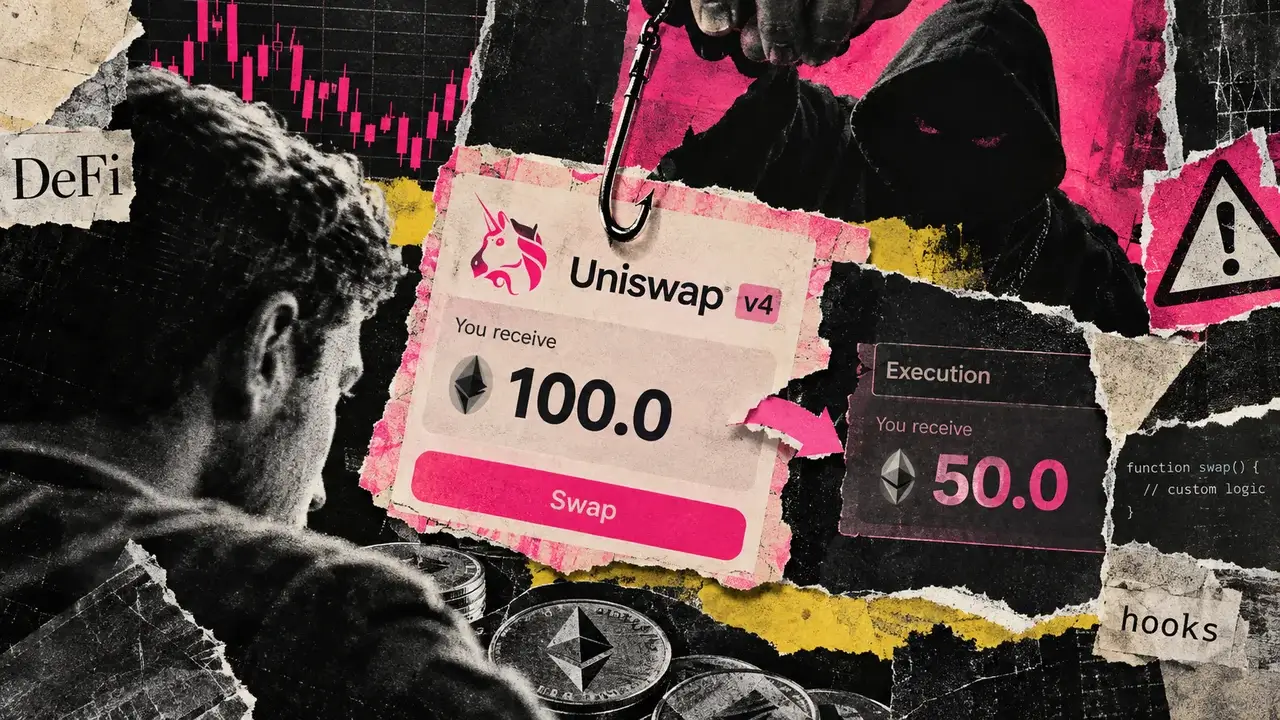
Malicious Uniswap v4 hooks are baiting DeFi traders with fake swap quotes
Liquidity aggregator 0x said on Sept. 14 that it had seen an alarming increase in malicious Uniswap v4 hooks over recent weeks, de...
A new XRPL upgrade could concentrate XRP ownership inside banks instead of retail wallets
A proposed XRP Ledger (XRPL) upgrade could let banks and fintechs absorb XRP costs so customers never need to hold the token. The...

XRP News: XRPL Records 2K Transactions from 20 Wallets
The XRP Ledger processed a record 3,254 transactions in ledger 106,965,249 yesterday, but 2,000 of the news came from just 20 acco...
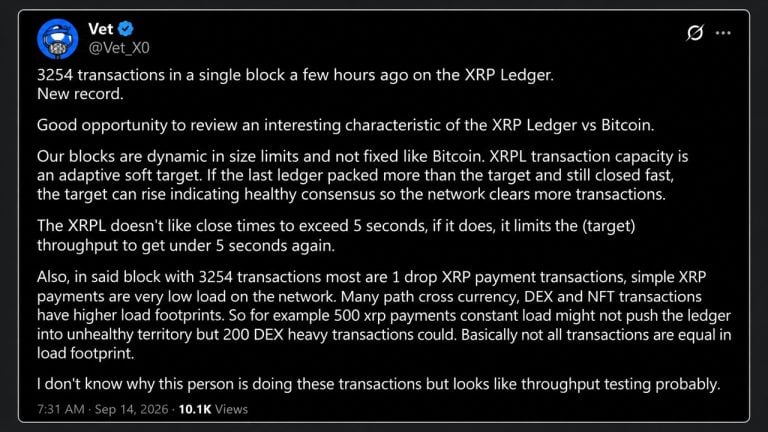
XRP Ledger Broke Its Transaction Record, and 20 Wallets Did Most of It
The XRP Ledger crammed a record 3,254 transactions into one ledger on Sept. 13, yet 2,000 of them were identical 1-drop payments f...
Ethereum, Base give up on common wallet standard after months of talks
Ethereum is moving ahead with EIP-8141 while Coinbase-backed Base backs EIP-8130, leaving wallets and apps that span both networks...
Ethereum and Base Abandon a Shared Wallet Standard as Account-Abstraction Talks Break Down
Ethereum and Base have given up on building one shared account-abstraction standard for both networks and will ship competing desi...