Openclaw AI Skills Vulnerable to Malicious Exploits, Certik Researchers Warn
A report by Certik highlights significant security flaws in Openclaw, an open-source AI platform, particularly its reliance on “skill scanning” which fails to adequately protect users from malicious third-party extension...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on Bitcoin NewsRelated market context

Argentina to require crypto platforms to report user data to local tax authority
Argentina's new crypto reporting rules could enhance tax compliance and international data sharing, impacting user privacy and pla...

EU mandates 24-hour reporting for crypto wallet vulnerabilities under Cyber Resilience Act
The EU's stringent reporting rules could drive significant investment in threat intelligence and reshape industry communication on...
EU cyber rules put crypto wallet makers on 24-hour reporting clock
Crypto wallet providers must submit an early vulnerability report within 24 hours and a full notification within 72 hours of explo...
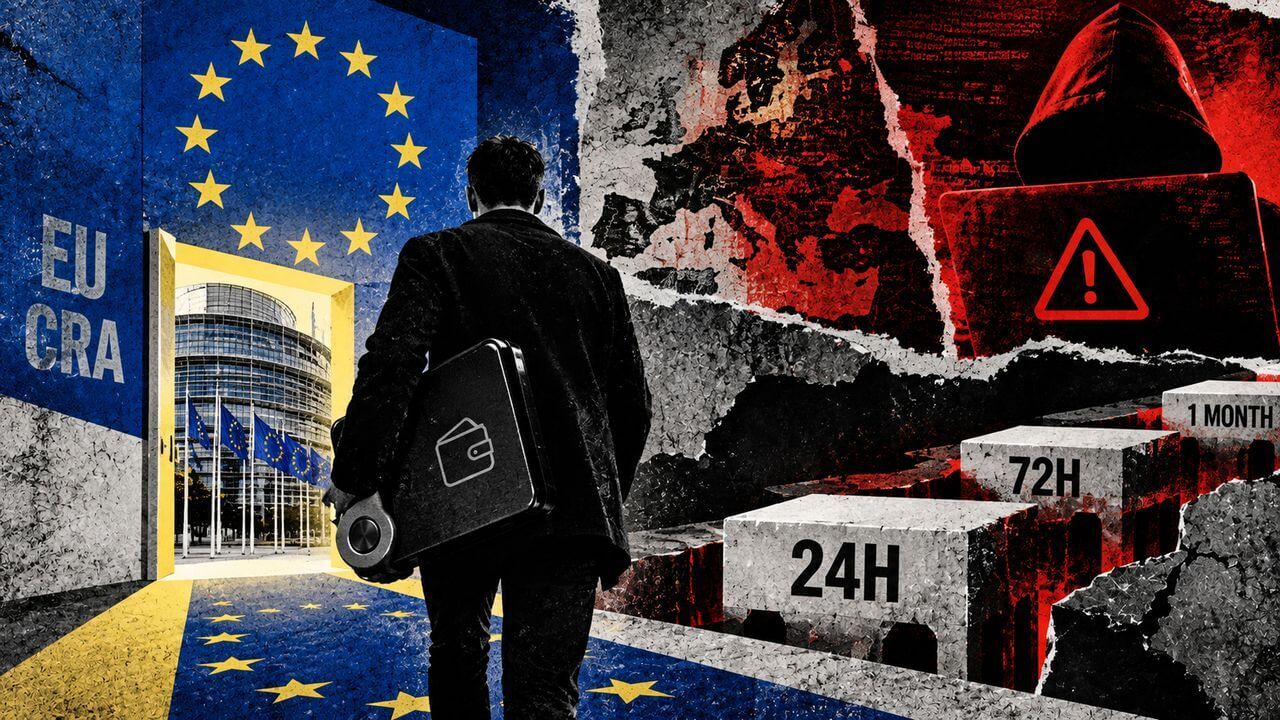
Crypto wallet creators now have just 24 hours to alert regulators when flaws are exploited
Commercial manufacturers whose connected hardware wallets or wallet software meet the European Union's product test must now warn...

Wyoming Stable Token Commission cites LayerZero security failures in switch to Chainlink CCIP
Wyoming's switch to Chainlink CCIP underscores the critical need for robust security in state-backed digital asset infrastructure....

Plume Network general counsel outlines tokenization’s benefits in Bitcoin Suisse wealth report
Tokenization's rise could redefine asset management, enhancing efficiency, transparency, and global competitiveness in financial m...