SlowMist flags Linux Snap Store attack targeting crypto seed phrases
Attackers have hijacked trusted Snap Store publishers via expired domains, allowing malicious wallet updates to reach long-time Linux users.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Attackers have hijacked trusted Snap Store publishers via expired domains, allowing malicious wallet updates to reach long-time Linux users.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context

Revolut Customer Records Exposed: Attackers Demand 10,000 BTC
Revolut disclosed sensitive customer records to an unauthorized party after fraudulent data requests arrived from an email address...

Revolut Exposes Bitcoin Records, Passports After Fraudulent Government Email Attack
Key Takeaways: Revolut had to share sensitive data about its users after receiving a phishing request that looked legitimate from...
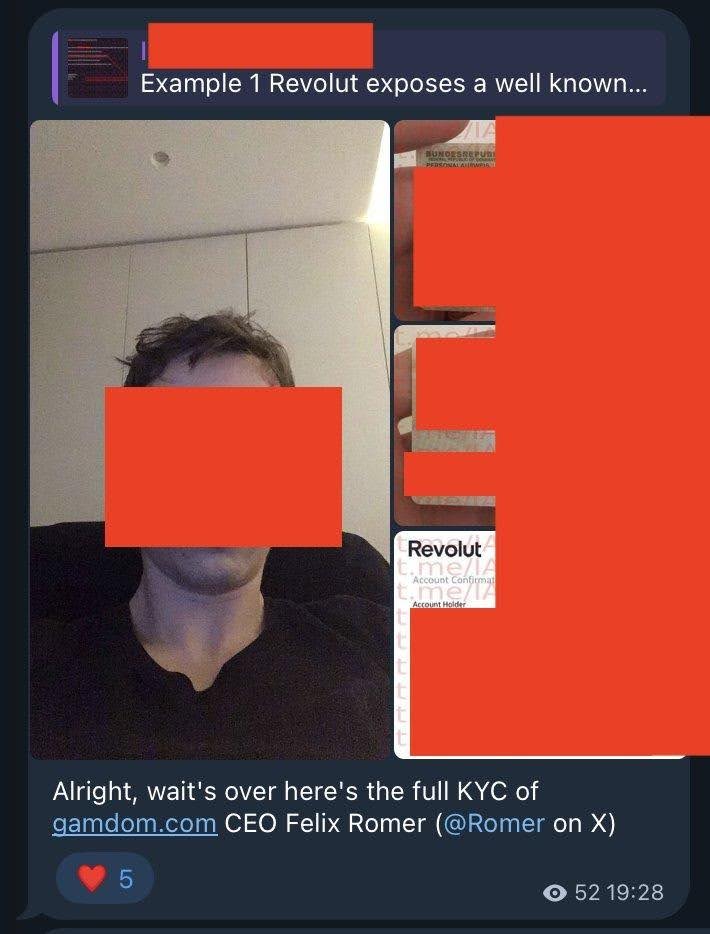
Revolut Crypto Data Leak Exposes Bitcoin Records, Attackers Demand Payment to Stop More
Key Takeaways: Hackers have reportedly begun to share personal data on the affected customers and ask for money to prevent more le...

SlowMist details Liquid Network exploit, attacker mints 3,998 L-BTC in largest Bitcoin sidechain hack of 2026
The exploit highlights critical vulnerabilities in sidechain security, urging immediate audits and reevaluation of cryptographic v...
Strive Snaps Up More Bitcoin, Brings Holdings to 25,000 BTC
Bitcoin Magazine Strive Snaps Up More Bitcoin, Brings Holdings to 25,000 BTC Nasdaq-listed bitcoin treasury Strive now holds 25,00...

Zoth expands zPayments to Base, targeting $6B in annual cross-border stablecoin payouts
Zoth's expansion of zPayments on Base could significantly disrupt traditional cross-border payment systems, enhancing speed and re...