Supply chain attack hits Axios npm releases, users urged to rotate keys
Security companies flagged [email protected] and 0.30.4 as compromised, urging credential rotation and rollback of affected packages.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Security companies flagged [email protected] and 0.30.4 as compromised, urging credential rotation and rollback of affected packages.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context

Anthropic’s Claude AI Predicts a Wild Price for Chainlink (LINK)
Anthropic’s Claude AI predicts that in a peak bull-market setup, Chainlink (LINK) could hit $150–$250 by January 1, 2027, with a s...
Tom Lee’s Bitmine Nears 5% of Ether Supply, Trims Weekly Buy to 12,532 ETH
Bitmine Immersion Technologies (NYSE: BMNR) held 6,028,946 ETH as of Oct. 11, the Ethereum treasury company said in a press releas...
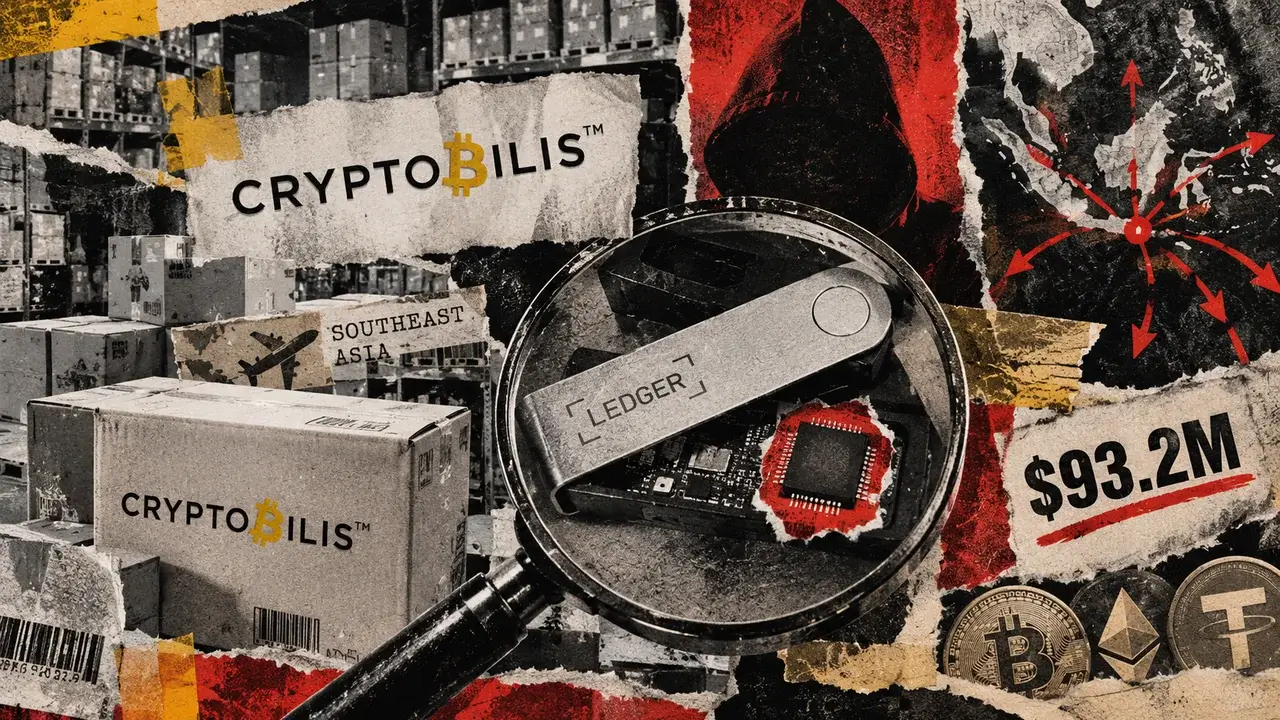
Ledger wallet implant exposes a gap in its authenticity check
Ledger has confirmed an unauthorized hardware implant in one affected customer's wallet as independent investigators estimate $93....
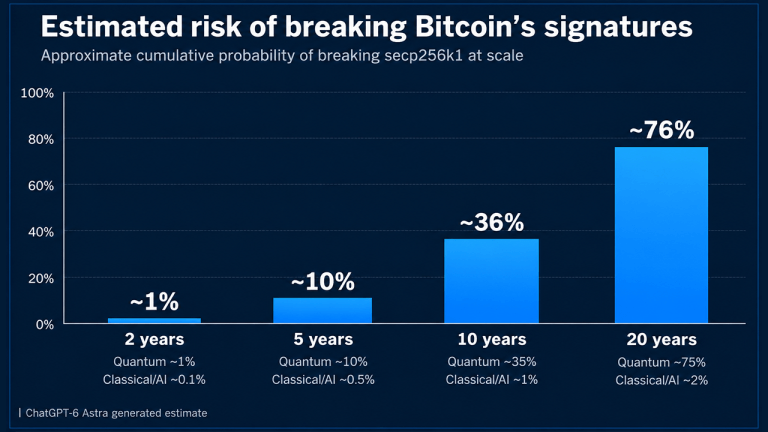
Bitcoin’s Security Faces a 76% Risk by 2046, AI Model Predicts
Onchain analyst Willy Woo stirred fresh debate over Bitcoin’s long-term security on Sunday, Oct. 11, 2026, after sharing artificia...
New iPhone spyware can hunt for crypto wallets and extract their data every 15 seconds
Researchers found a new iPhone spyware variant that can remotely extract cryptocurrency wallet data and sensitive credentials from...
China’s top leadership calls for a national blockchain network, minus the tokens
China's blockchain push, sans tokens, may bolster state control over digital infrastructure, impacting global blockchain innovatio...