Malicious Pull Request Inserted Into Ethereum Code Extension: Research
Cybersecurity firm ReversingLabs uncovered two lines of malicious code in an update forETHCode, an open source suite of tools.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Why this matters
This ethereum story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on DecryptRelated market context
Former Ethereum Core Dev Greg Markou Defends Developers Over Stalled Gas Repricing
Greg Markou, a former Ethereum core developer, defended the engineers who build Ethereum’s protocol as Glamsterdam, its next upgra...
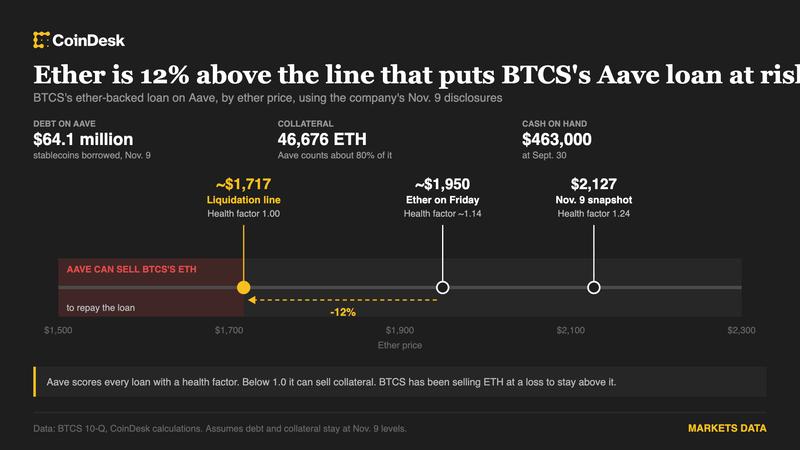
Ethereum treasury firm BTCS sold ether at a loss to keep $64 million Aave loan healthy
The Nasdaq-listed company has 46,676 ETH backing its borrowings, and the loan could become eligible for liquidation if ether slide...
18 Crypto Firms Seek to Join Court Fight Over Illinois’ 0.2% Crypto Tax
Under Illinois’ Digital Asset Tax Act, a broker that exchanges, transfers or holds a digital asset for a customer in Illinois must...

Ethereum Dancing on Two Fronts as Quantum Upgrade Advances and Treasury Leverage Bites
Ethereum developers want to upgrade the network to be quantum-ready by 2027, potentially accelerating one of its biggest security...
Ethlabs Calls for Ethereum Quantum Protection in 2027 as Upgrade Priorities Shift
TL;DR: Ethlabs proposes quantum readiness in 2027 and plans to withdraw its quick-slots work from Hegotá. Developers still need to...
Ethereum faces temporary issues due to cloud provider malfunction
Cloud dependency highlights Ethereum's vulnerability, urging diversification to ensure network resilience and uninterrupted user a...