Wintermute’s “CrimeEnjoyor” to Warn Ethereum Users of Wallet-Draining Attacks
Key Takeaways: Wintermute’s new “CrimeEnjoyor” tool injects on-chain warnings into malicious Ethereum contracts. Over 97% of EIP-7702 delegations are being used in wallet-draining attacks. An Ethereum user recently lost...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Key Takeaways:
- Wintermute’s new “CrimeEnjoyor” tool injects on-chain warnings into malicious Ethereum contracts.
- Over 97% of EIP-7702 delegations are being used in wallet-draining attacks.
- An Ethereum user recently lost $146K by signing malicious EIP-7702 transactions.
Crypto market maker Wintermute has developed a tool that injects on-chain warnings into malicious wallet-draining contracts to alert users.
The new tool comes as Ethereum users face a new wallet-draining threat that exploits a feature in the network’s latest upgrade.
On May 30, Wintermute revealed it had developed “CrimeEnjoyor,” a code that injects visible warnings into verified malicious Ethereum contracts. The move targets contracts designed to auto-drain wallets when private keys are compromised.
‘Do Not Send ETH’ WarningThe injected message clearly states that the contract “is used by bad guys to automatically sweep all incoming ETH” and prominently advises users to “NOT SEND ANY ETH.”
The malicious contracts exploit Ethereum Improvement Proposal-7702 (EIP-7702), a feature introduced in the recent Pectra upgrade.
EIP-7702 allows wallet owners to temporarily delegate control of their wallets to smart contracts—an opt-in feature meant to expand Ethereum’s capabilities.
However, Wintermute’s research team found troubling patterns.
According to their analysis, over 97% of EIP-7702 delegations were being used in identical sweeping contracts designed to automatically drain ETH from compromised addresses.
“These are sweepers, used to automatically drain incoming ETH from compromised addresses,” Wintermute said in a post on X.
While EIP-7702 brings new convenience, it also introduces new risks
Our Research team found that over 97% of all EIP-7702 delegations were authorized to multiple contracts using the same exact code. These are sweepers, used to automatically drain incoming ETH from compromised… pic.twitter.com/xHp7zr4hC9
To inject warnings, the team reverse-engineered the contracts’ Ethereum Virtual Machine (EVM) bytecode into readable Solidity code and then publicly verified it.
As a result, the modified warning now appears inside most of the malicious contracts.
“This one copy-pasted bytecode now accounts for the majority of all EIP-7702 delegations,” Wintermute added. “It’s funny, bleak, and fascinating at the same time.”
While EIP-7702 was designed to offer greater wallet flexibility, its lack of verification features has made it difficult for users—especially newcomers—to distinguish between legitimate and malicious contracts.
Wintermute hopes that tagging compromised contracts will help surface suspicious activity and better protect the ecosystem.
Ethereum User Loses $146KThe risks are real. On May 23, one Ethereum user lost $146,550 after unknowingly signing a batch of malicious EIP-7702 transactions, according to blockchain security firm Scam Sniffer.
ALERT: An address upgraded to EIP-7702 lost $146,551 through malicious batched transactions in phishing attack. pic.twitter.com/7GbamqOZVI
— Scam Sniffer | Web3 Anti-Scam (@realScamSniffer) May 24, 2025Since Ethereum’s Pectra upgrade went live on May 7, users have executed 12,329 EIP-7702 transactions.
Pectra also introduced other significant changes: EIP-725 raised the validator staking limit from 32 ETH to 2,048 ETH, and EIP-7691 increased data blob capacity to improve scalability and lower fees on Ethereum layer-2 networks.
Last month, Vitalik Buterin unveiled a new proposal aimed at making it significantly easier for everyday users to run Ethereum nodes, by reducing the hardware and storage requirements currently needed to sync with the network.
The Ethereum mastermind suggested a shift in how nodes store and retrieve data, moving from full data replication to a more flexible, user-centric model.
Under this approach, nodes would store only the data relevant to the user, rather than Ethereum’s entire global state, which currently exceeds 1.3 terabytes, according to Etherscan.
The post Wintermute’s “CrimeEnjoyor” to Warn Ethereum Users of Wallet-Draining Attacks appeared first on Cryptonews.
Why this matters
This ethereum story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CryptonewsRelated market context
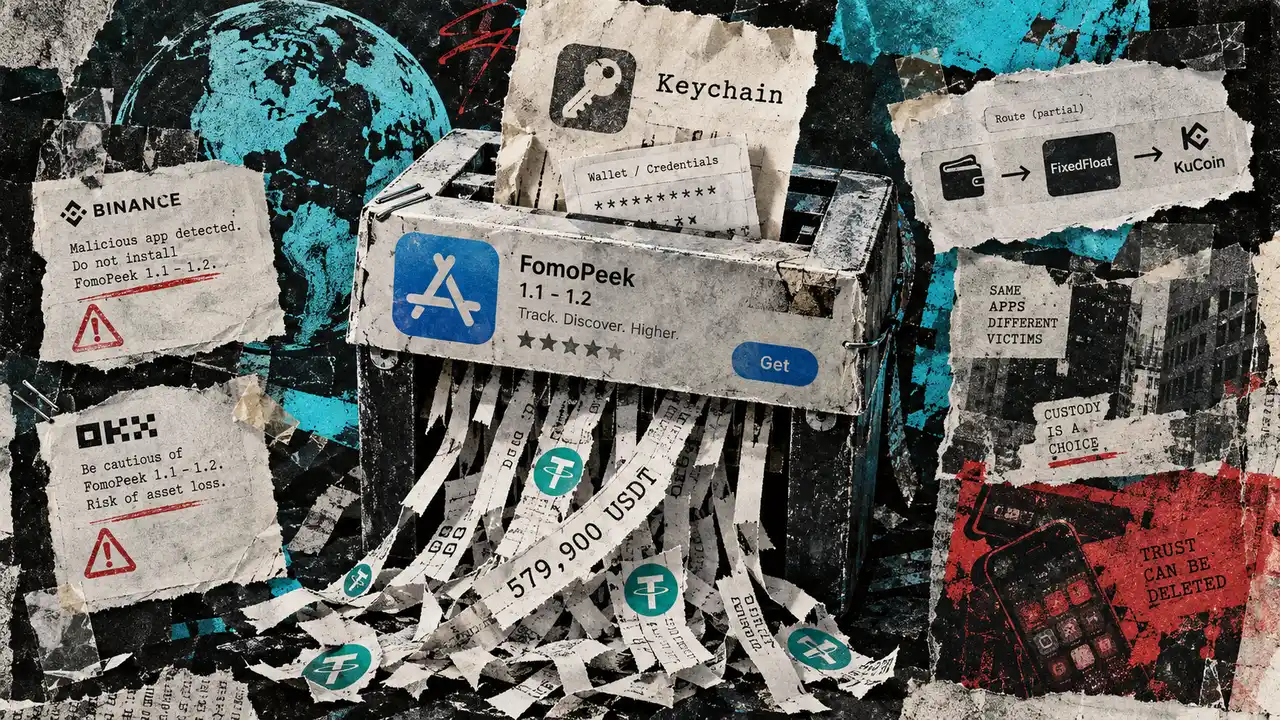
Rogue iPhone app escapes iOS sandbox to hijack $580,000 in USDT
Fomopeek, a malicious iPhone app distributed through Apple’s App Store, has been linked to nearly $580,000 in stolen USDT. Blockch...

Ethereum ETFs Pull In $270M As BlackRock Leads September 21 Rebound
TL;DR US spot Ethereum ETFs recorded $270.0 million of net inflows for the September 21 session. BlackRock’s ETHA led the day with...
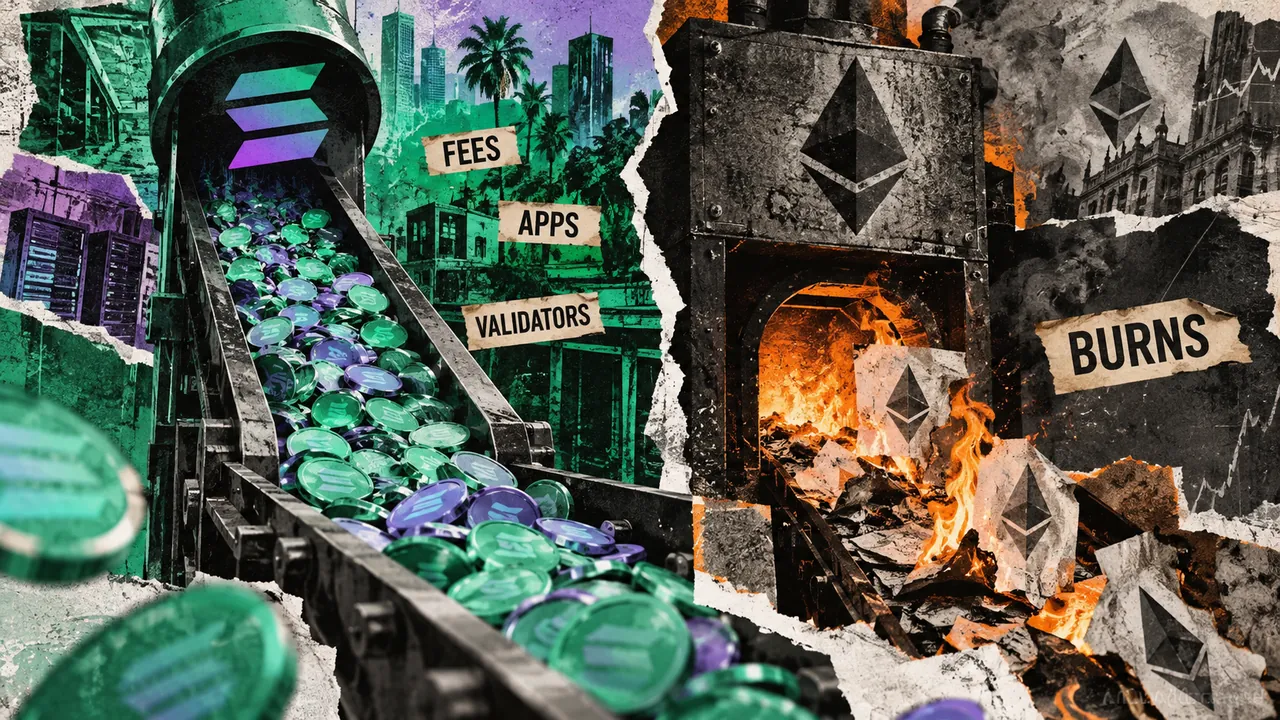
Solana flips Ethereum in fees, while ETH holds the burn lead
Solana generated more user fees than Ethereum in data provider DefiLlama's Sept. 22 dashboard snapshot, while Ethereum burned more...
Crypto Exchange That Invented 100x Leverage Is No More: Here’s What BitMEX Users Need to Know
BitMEX ended trading at 04:00 UTC Wednesday and is urging users to withdraw their remaining funds, as fees now apply to balances l...
NYSE, Blockchain.com in tie-up to bring tokenized US stocks to crypto users
Blockchain.com users could gain access to tokenized US stocks and ETFs through NYSE’s planned digital trading platform under a new...
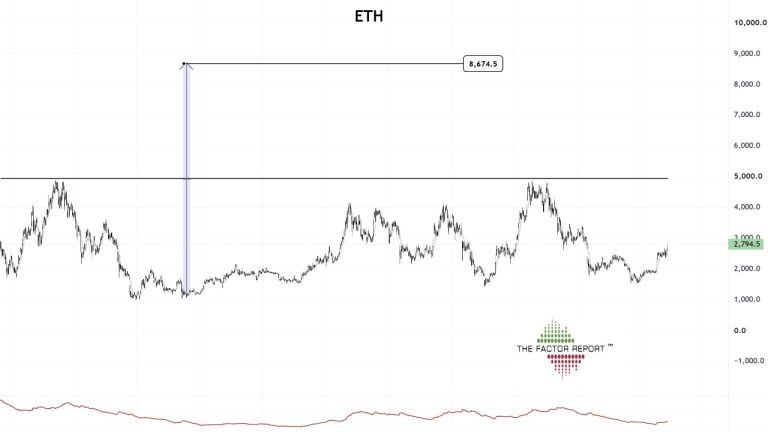
Peter Brandt Sees Ethereum at $8,600 if ETH Clears $5,000
Ethereum could eventually reach $8,600 if it first clears $5,000, according to a long-term chart posted by veteran trader Peter Br...