ZachXBT infiltrates $1B crypto syndicate to expose Lazarus Group
Blockchain investigator ZachXBT said he infiltrated a Chinese laundering syndicate by posing as a cryptocurrency client and funding repeated stablecoin trades. In an Oct. 5 disclosure, he alleges the network laundered mo...
Watchlist
Archive context. The story has cross-source confirmation.
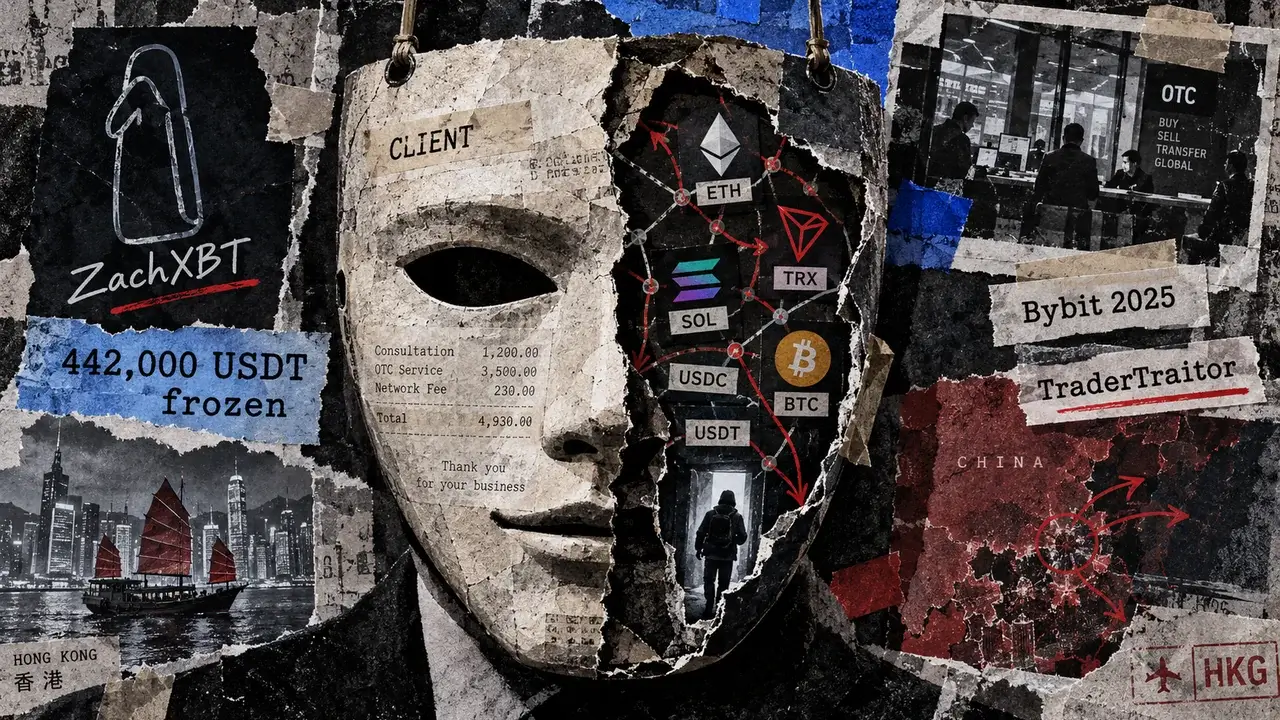
Blockchain investigator ZachXBT said he infiltrated a Chinese laundering syndicate by posing as a cryptocurrency client and funding repeated stablecoin trades.
In an Oct. 5 disclosure, he alleges the network laundered more than $1 billion across exploits for Lazarus Group.
He said he fronted 349,700 USDC to build a relationship with a contact using the alias Jimmy Green. According to his account, the repeated exchanges led to private conversations about moving funds stolen from Bybit in 2025.
He reported tracing a cluster involving more than $12 million in Bybit funds and a later 442,000 USDT freeze by Tether.
Becoming a clientZachXBT said the investigation began after the February 2025 Bybit exploit, when he noticed at least 15 accounts asking for help with orders he linked to stolen funds in public Telegram and Discord groups.
He contacted several of those accounts. One was Jimmy Green, the Telegram alias of the person with whom he subsequently exchanged funds.
On March 6, 2025, ZachXBT said he funded a new Ethereum address with 349,700 USDC in preparation for transactions with the contact. The arrangement involved sending his USDC on Ethereum in exchange for the contact's USDT on Tron. He then completed additional transactions to build trust.
As he built trust through repeat exchanges, ZachXBT said the contact began discussing movements of Bybit funds for North Korea before they occurred. The conversations also included details about operations in Hong Kong and mainland China.
In one example, he said the contact told him funds would move to Solana, and the movement happened the following day.
On March 12, 2025, ZachXBT said the contact sent a screenshot of a cross-blockchain transfer. He matched its amounts and timing to an order on the THORChain transaction explorer created within minutes of the message.
According to ZachXBT, the contact also supplied three Solana addresses. He said these exposed a cluster involving more than $12 million in Bybit exploit funds moving through Bitcoin, Ethereum, Solana and Tron.
He separately reported that Tether later froze 442,000 USDT linked to the cluster. That is the specific freeze amount described in this part of his investigation; the larger cluster figure represents funds he said he traced.
Related Reading Did Tether just freeze $72M in USDT with no link to a hack in Monero money laundering sting?The account also reaches beyond Bybit. ZachXBT said the contact mentioned a team whose funds had been frozen in 2024. He said that matched an on-chain freeze of 332,000 USDC tied to the Poloniex exploit.
The Bybit backdrop and the cost of accessIn a Feb. 26, 2025 alert, the FBI said North Korea stole approximately $1.5 billion in virtual assets from Bybit on or about Feb. 21. It called the specific malicious activity TraderTraitor.
At the time, the FBI said some stolen assets had been converted into Bitcoin and other virtual assets dispersed across thousands of addresses on multiple blockchains. It urged private-sector services to block transactions connected to the laundering addresses.
The syndicate's total and the links to Jimmy Green remain ZachXBT's findings, separate from the FBI's attribution of the theft.
Allegations involving a Chinese over-the-counter trader surfaced in October 2024. The latest account describes how ZachXBT obtained information by becoming a trading counterparty himself.
ZachXBT said he fronted 349,700 USDC for the case and lost 5% on each order. The amount advanced is distinct from his net loss, which he did not quantify in the disclosed figures.
He appealed for continued foundation grants and individual donations to support higher-risk investigations. He said intelligence from these trades helped freeze funds tied to the Bybit exploit.
The post ZachXBT infiltrates $1B crypto syndicate to expose Lazarus Group appeared first on CryptoSlate.
Why this matters
Tether is showing up inside the Stablecoins theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CryptoSlateRelated market context
Binance Hack: CZ Fires Back at Elon Musk, Cites $1B SpaceX Stake as Coinbase Offers Security Support
The dispute unfolded as Binance worked to contain the October 29 attack, freeze affected assets, and reassure customers that their...

Tether Q3 Profit Hits $1.5B While USDT Reserve Buffer Nearly Doubles to $8B
Key Takeaways: In Q3, Tether achieved an operating profit of $1.5 billion. Reserve assets rose to almost $8 billion. U.S. Treasury...
Bitcoin’s Rebound Drove Most of Tether’s $3.8 Billion Reserve Recovery
Tether held $7.95 billion more in reserves than it owed USDT holders on Sept. 30, up about $3.85 billion from the end of June, the...
Coinbase (COIN) Misses Revenue Estimates as Users Fall, Armstrong Sets Up New Share Sales
Bitcoin Magazine Coinbase (COIN) Misses Revenue Estimates as Users Fall, Armstrong Sets Up New Share Sales Coinbase had a mixed th...
US Secret Service Joins Circle, Tether in Freezing $2.37B in Binance Hack Funds
The US Secret Service is working with stablecoin issuer Circle to recover funds stolen in the $6.3 billion security breach at Bina...
Spot Bitcoin ETFs shed $643 million in a day as Ethereum funds lose $156 million
The significant outflows from Bitcoin and Ethereum ETFs highlight investor sensitivity to market disruptions, potentially impactin...