$2.5M Gone in Hours — Victim Hit Twice in Sophisticated Stablecoin Phishing Scam
A crypto investor lost a staggering $2.6 million USDT on May 26, 2025, after falling victim twice within three hours to a sophisticated phishing scam that manipulated Ethereum’s transaction history through zero-value tra...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
A crypto investor lost a staggering $2.6 million USDT on May 26, 2025, after falling victim twice within three hours to a sophisticated phishing scam that manipulated Ethereum’s transaction history through zero-value transfers. Could this devastating double-hit expose a critical blind spot in how even experienced traders verify wallet addresses?
The attack, which first siphoned off $843,000 and another $1.75 million, has raised serious concerns about how even seasoned traders verify wallet addresses in on-chain transactions.
The Mechanics: Zero-Value Transfers and Onchain Phishing https://twitter.com/CyversAlerts/status/1926915902001254475According to a report by crypto compliance firm Cyvers, the scammers used Ethereum’s transferFrom function to create transactions from the victim’s wallet to spoofed addresses without needing any private key signature or user authorization.
Since the transactions involved no real value, they were automatically added to the blockchain without triggering typical security alerts.
This attack works by placing the scammer’s wallet address in the victim’s transaction history. Users who see the address logged as an outbound transaction are more likely to trust it, mistaking it for a previously interacted or known address.
In follow-up transactions, they may copy and paste the spoofed address, unknowingly sending tangible assets directly to the attacker.
Zero-value transfers are considered an advanced evolution of the older address poisoning scam.
In traditional address poisoning, scammers send tiny amounts of cryptocurrency from addresses closely resembling the victim’s legitimate contacts, often with the same starting and ending characters.
Users who rely on pattern recognition or partial address verification are more likely to fall into the trap.
Zero-value transfers take this one step further by adding the fake transaction to the user’s visible history, reinforcing false legitimacy.
Blockchain security firm Elliptic reported in 2023 that roughly 150 scammers had initiated over 176,000 of these Ethereum and BNB Chain transactions since November 2022.
While these are zero-value transactions, executing them requires considerable gas fees.
The scammers have spent over $710,000 on fees but earned more than $1.5 million in illicit proceeds, resulting in a net profit of just under $800,000, averaging about $5,500 per attacker.
In a notable precedent in May 2024, a victim of a sophisticated address poisoning scam recovered nearly all of the $71 million in stolen WBTC, thanks to swift intervention by blockchain security firm Match Systems and exchange Cryptex.
https://twitter.com/cryptonews/status/1789566522538775019?s=46 Broader Impact and Defensive Measures Against Phishing ScamThe rise of zero-value transfer scams has exposed a troubling vulnerability in user behavior and how wallet interfaces present transaction data.
A January 2025 report revealed over 270 million address poisoning attempts occurred on BNB Chain and Ethereum between July 2022 and June 2024. Out of these, about 6,000 attempts were successful, resulting in losses exceeding $83 million.
https://twitter.com/cryptonews/status/1909156923318132953?s=46In response, the crypto ecosystem has started adapting. In 2023, Etherscan announced a new feature that hides zero-value token transfers by default to shield users from misleading transaction records.
https://twitter.com/etherscan/status/1645406189692526593?s=46While users can still choose to view them, the default setting aims to reduce confusion and prevent phishing attempts from reaching the average wallet owner.
Crypto wallet providers like Trezor have issued warnings about address poisoning and emphasized that such phishing scams, while insidious, do not involve any compromise of private keys or internal wallet security.
Instead, they rely on human error and behavioral exploitation, targeting the visual habits of users who recognize addresses by appearance or copy-paste from transaction logs without double-checking.
The post $2.5M Gone in Hours — Victim Hit Twice in Sophisticated Stablecoin Phishing Scam appeared first on Cryptonews.
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CryptonewsRelated market context

US Charges Man After Crypto Scam Wallets Received More Than $53M
TL;DR U.S. prosecutors have charged a Vietnamese national with money laundering tied to alleged cryptocurrency “pig butchering” sc...
Binance Wallet lets users pay gas fees in USDT across four major networks
Binance Wallet's USDT gas fee option simplifies crypto transactions, potentially increasing user adoption and reducing reliance on...
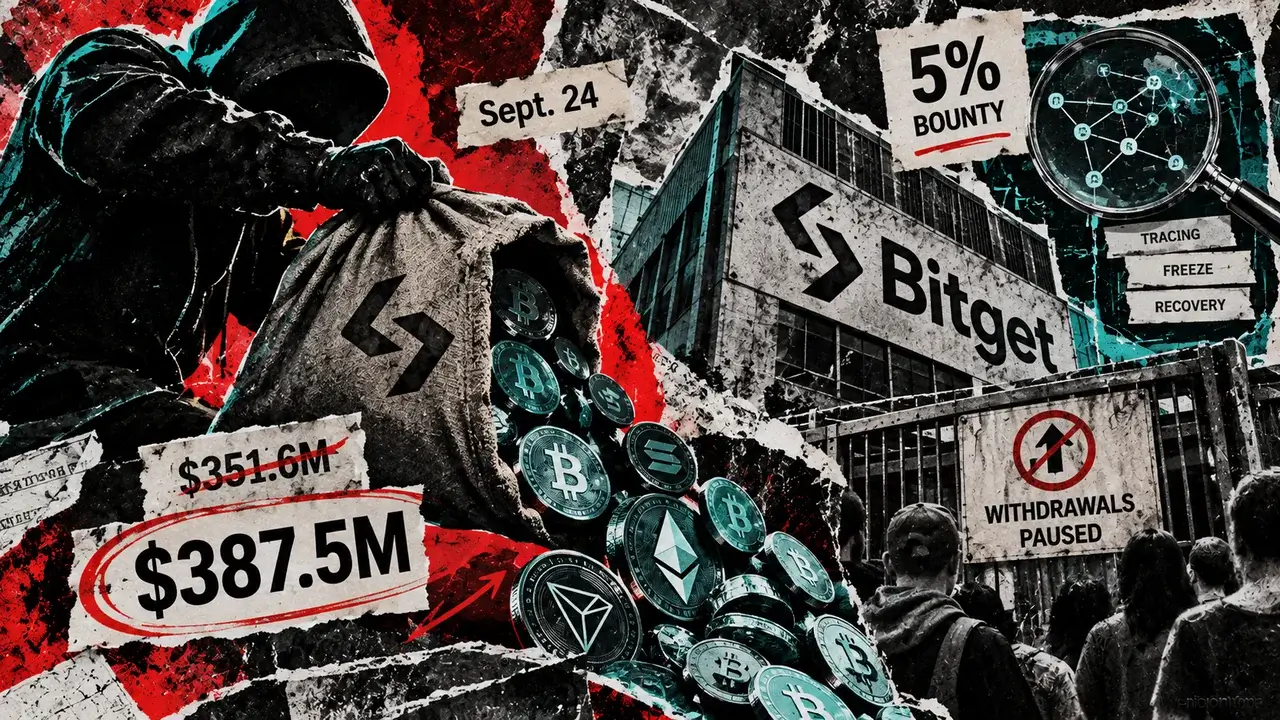
Bitget’s hack just got $36 million bigger, and now there’s a bounty on the stolen crypto
Bitget has raised the estimated value of assets taken in its Sept. 24 breach to $387.5 million as exchanges and security firms mob...
Washington has $114 billion reasons to want Tether around
Not that long ago, Washington fined Tether for misleading people about the dollars behind its tokens. Today, the company's insatia...
Bitget raises breach losses to $387.5 million after on-chain tracing uncovers Zcash and TRON transfers
Bitget raises breach losses to $387.5 million after tracing reveals Zcash and TRON transfers. Cold wallets secure, protection fund...
Bitget Confirms $351.6M Hot Wallet Breach And Pauses Withdrawals
Bitget says unauthorized transfers affected approximately $351.6 million held across parts of its hot and warm wallet infrastructu...