Bybit $1.4 Billion Breach Linked to Safe Wallet Vulnerability, Investigation Finds
Cryptocurrency exchange Bybit experienced a security breach resulting in the unauthorized transfer of over $1.4 billion in liquid-staked Ether (ETH) and MegaETH (mETH). The exchange reported unauthorized access to one of...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
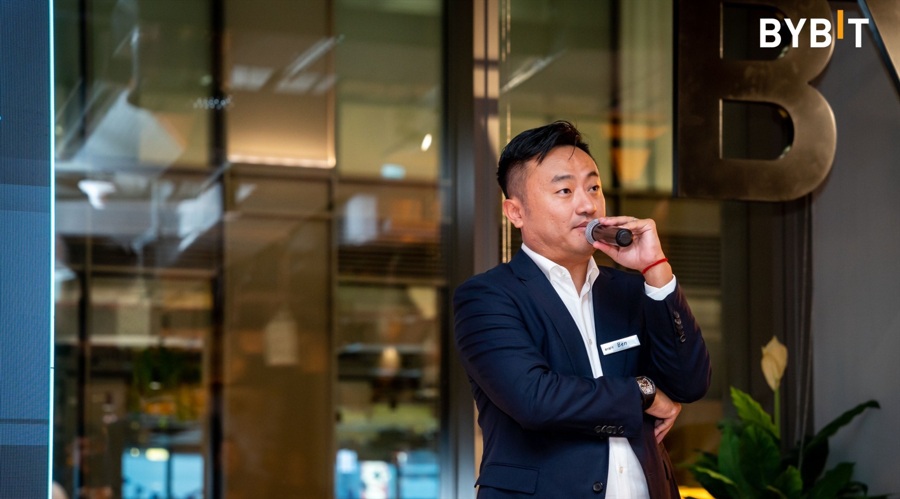
Cryptocurrency exchange Bybit experienced a security breach resulting in the unauthorized transfer of over $1.4 billion in liquid-staked Ether (ETH) and MegaETH (mETH). The exchange reported unauthorized access to one of its Ethereum cold wallets on February 21, 2025.
The incident took place during a multisignature transaction facilitated through Safe Wallet. A threat actor intercepted the process, altered the transaction, and gained control of the wallet. The attacker then transferred the funds to a separate wallet under their control.
Following the discovery, Bybit engaged cybersecurity firm Sygnia to conduct a forensic investigation. The investigation aimed to determine the source of the compromise, assess the extent of the attack, and implement measures to prevent future incidents.
Investigation Findings
The forensic analysis identified that malicious JavaScript code had been injected into a resource served from Safe Wallet’s AWS S3 bucket. The modification timestamp and historical web records suggest that the code was added on February 19, 2025, two days before the unauthorized transaction.
Bybit Hack Forensics ReportAs promised, here are the preliminary reports of the hack conducted by @sygnia_labs and @Verichains Screenshotted the conclusion and here is the link to the full report: https://t.co/3hcqkXLN5U pic.twitter.com/tlZK2B3jIW
— Ben Zhou (@benbybit) February 26, 2025The injected code was designed to manipulate transaction data during the signing process. It activated only when the transaction originated from specific contract addresses, including Bybit’s contract and another unidentified address. This suggests that the attacker had predefined targets for the exploit.
Safe Wallet JavaScript Modified Before Attack
Forensic examination of Chrome browser cache files from the three signers’ systems confirmed the presence of the compromised JavaScript resource at the time of the transaction. These files indicated that the Safe Wallet resource was last modified shortly before the attack.
Further analysis revealed that two minutes after the fraudulent transaction was executed, new versions of the affected JavaScript files were uploaded to SafeWallet’s AWS S3 bucket, removing the injected code. This suggests an attempt to conceal the unauthorized modification.
Public web archives captured two snapshots of Safe Wallet’s JavaScript resources on February 19, 2025. The first snapshot contained the original, unaltered version, while the second snapshot showed the presence of the malicious code. This further supports the conclusion that the attack originated from Safe Wallet’s AWS infrastructure.
No Evidence of Bybit Infrastructure Breach
At this stage, the forensic investigation has not found any evidence of a compromise within Bybit’s own infrastructure. The unauthorized access appears to have been facilitated through vulnerabilities in SafeWallet’s systems. Bybit and Sygnia are continuing their investigation to confirm the findings and assess any additional risks.
“The preliminary forensic review finds that our system was not compromised. While this incident underscores the evolving threats in the crypto space, we are taking proactive steps to reinforce security and ensure the highest level of protection for our users,” said Ben Zhou, Co-founder and CEO of Bybit.
This article was written by Tareq Sikder at www.financemagnates.com.Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on Finance MagnatesRelated market context

Safepal Hardware Wallet Users Receive Fake Security Alerts in the Mail
Safepal customers in Italy are reportedly being targeted by a sophisticated phishing campaign involving fraudulent letters contain...
Why the Path to Quantum Resistance Runs Uphill for Wallet Manufacturers
Bitcoin custody has always involved some degree of risk, but wallet manufacturers like Trezor — which build physical devices desig...
OpenAI introduces ChatGPT wallet for Pro subscribers
OpenAI's ChatGPT Wallet could streamline AI-driven transactions, enhancing user convenience and potentially reshaping digital comm...

Bitget Hacker Moves $78.6M in Bitcoin, Sends $63.4M Through 66 CoinJoin Transactions
Key Takeaways: In six days, Arkham recorded a loss of 1,052.34 BTC valued at $78.61 million from wallets that were identified as b...
Your wallet may show a dollar balance for fake USDT that you cannot sell
Keeper wallets maintained the quotations through restricted pools, where Forta's simulated outside sales failed for all 32 identif...
OpenAI Launches ChatGPT Wallet to Let AI Agents Shop—Without Crypto
OpenAI’s new wallet lets AI agents buy products using ordinary cards, challenging crypto payment tools from Coinbase and Circle as...