Claude Code Vulnerability Could Let Attackers Steal Credentials From GitHub, Says Microsoft
Researchers say prompt injection attacks could manipulate AI coding agents to access sensitive credentials stored in software development pipelines.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Why this matters
Anthropic is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on DecryptRelated market context

WaterPlum Targets 30,000 Devices and Steals 7,000+ Crypto Wallet Records Worldwide
Key Takeaways: WaterPlum hacked over 30,000 devices in 100+ countries and accessed information from 7,000+ crypto wallets. Fake jo...
AI Is Rereading Crypto’s Old Code, and Finding What Humans Missed
Crypto’s security problem took a strange turn in 2026. Artificial intelligence (AI)-assisted researchers found a four-year-old Zca...
Fake AI crypto software is secretly replacing browser wallet extensions
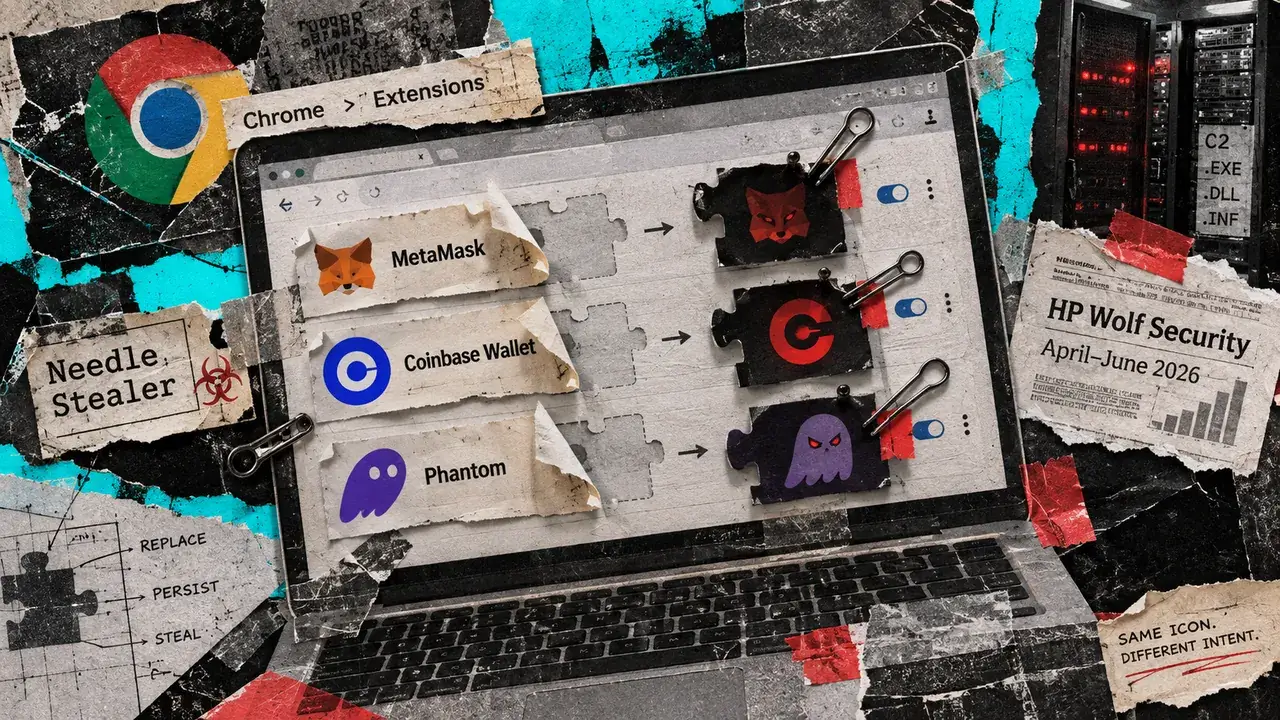
HP Wolf Security, the company's threat-research team, said a fake AI crypto-trading assistant distributed malware that could repla...
Researchers warn of Safari zero-day exploit targeting Apple iPhones and crypto wallets
The exploit highlights the critical need for enhanced security measures in mobile ecosystems, especially for safeguarding crypto a...

S&P Global Agrees To Acquire Smart Contract Security Firm OpenZeppelin
TL;DR S&P Global has agreed to acquire OpenZeppelin. OpenZeppelin is one of the best-known smart contract security and auditing fi...
Malware steals over $235K in crypto from hundreds of victims in just 48 hours
The incident highlights the urgent need for enhanced security measures in the crypto space, as irreversible transactions amplify c...