Crypto hackers exploit third-party Aave tool to steal 114 ETH
A third-party lending adapter built on Aave was exploited to steal about 114 ETH, worth over $300,000, while the protocol itself remained unaffected. On Oct. 2, blockchain security firm SlowMist said the attacker comprom...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
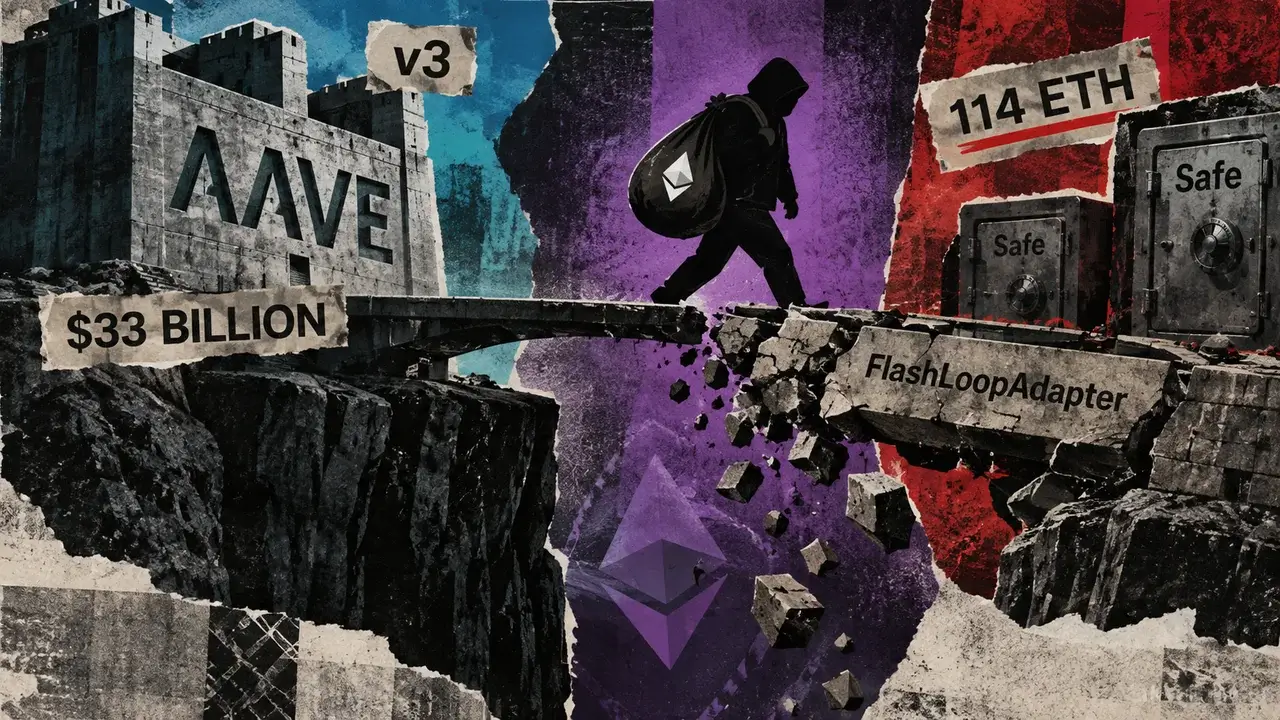
A third-party lending adapter built on Aave was exploited to steal about 114 ETH, worth over $300,000, while the protocol itself remained unaffected.
On Oct. 2, blockchain security firm SlowMist said the attacker compromised two Safe multisig wallets through a flaw in the FlashLoopAdapter used with Aave v3 positions. The exploit allowed the attacker to bypass the adapter’s authentication checks, execute arbitrary calls, and drain collateral from the affected wallets.
SlowMist estimated the direct loss at about 114.09 ETH. It said roughly 1,300 WETH of debt was also repaid during the attack to unlock collateral tied to the positions.
Aave founder Stani Kulechov said the incident did not involve Aave v3’s core smart contracts. He said:
“This is not Aave v3 contract, it’s third party external adapter built on top of Aave, zero effect on Aave v3.”
The distinction is significant for Aave, the largest decentralized lending protocol, with more than $33 billion in total value locked. The exploit affected infrastructure layered on top of Aave.
Fake Safe bypass opened access to collateralSlowMist traced the vulnerability to the FlashLoopAdapter’s open() and close() functions, which checked whether the calling Safe had enabled the adapter as a module.
That verification could be spoofed.
Related Reading Why DeFi giant Aave is pulling the plug on six hyped blockchains making less than $5,000 a quarterAccording to SlowMist, the attacker created a fake Safe contract that always returned a positive response when asked whether the module was enabled. The adapter then accepted the forged authentication and proceeded to its internal swap function.
The more serious weakness came next. The adapter allowed the caller to specify both the router and calldata used in an external contract call.
The attacker pointed the router back at the victim Safe and supplied instructions invoking Safe’s execTransactionFromModule function. Because the FlashLoopAdapter was already enabled as a module on the affected wallets, that call gave the attacker a path to execute transactions through the victims’ Safes.
SlowMist said the technique was used to withdraw weETH and collateral associated with Aave positions from two multisig wallets.
The incident highlights a recurring risk in decentralized finance: protocol security can remain intact while integrations built around it create separate attack surfaces.
For Aave, the immediate exposure appears contained to users of the vulnerable adapter. The next question is whether other wallets enabled the same module and whether the adapter’s developers identify additional affected positions before attackers can reuse the same authentication flaw.
The post Crypto hackers exploit third-party Aave tool to steal 114 ETH appeared first on CryptoSlate.
Why this matters
Aave is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CryptoSlateRelated market context

PHP Attack Threatens Crypto Safety: Should You Cash Out or Pull Funds From Exchanges?
The FBI, National Security Agency (NSA), and Cybersecurity and Infrastructure Security Agency (CISA) have warned organizations to...
Ethereum Scraps Glamsterdam’s Hoodi Fork After ChainSecurity Flags Gas Risks
Ethereum developers have called off Glamsterdam’s activation on the Hoodi testnet, four days before the upgrade was due to go live...

Dogecoin Labs Unites 3 Major DOGE Teams to Build Payments, Apps and DeFi at Scale
Key Takeaways: Dogecoin Labs is introducing MyDoge, DogeOS and Such App under one independent organization. The group is targeting...

Are You Sure Your USDC Rewards Are Safe?
Under the GENIUS Act, the stablecoin law Congress passed in July 2025, companies that issue stablecoins can’t pay interest to the...
Aave proposes V3.8 upgrade to add reentrancy protection across 16 networks
Aave's proactive security upgrade could set a precedent for DeFi protocols, emphasizing risk management and network-wide consisten...
Robinhood stock tokens go live on Morpho as collateral for stablecoin loans
Robinhood's integration with Morpho enhances DeFi liquidity options, potentially spurring innovation and expanding decentralized f...