Crypto users lost at least $5.69 million because their wallet seeds were too predictable
A flaw in software used by at least five crypto wallets made some recovery phrases predictable enough for attackers to reconstruct, contributing to at least $5.69 million in traced thefts since May. Earlier this month, b...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
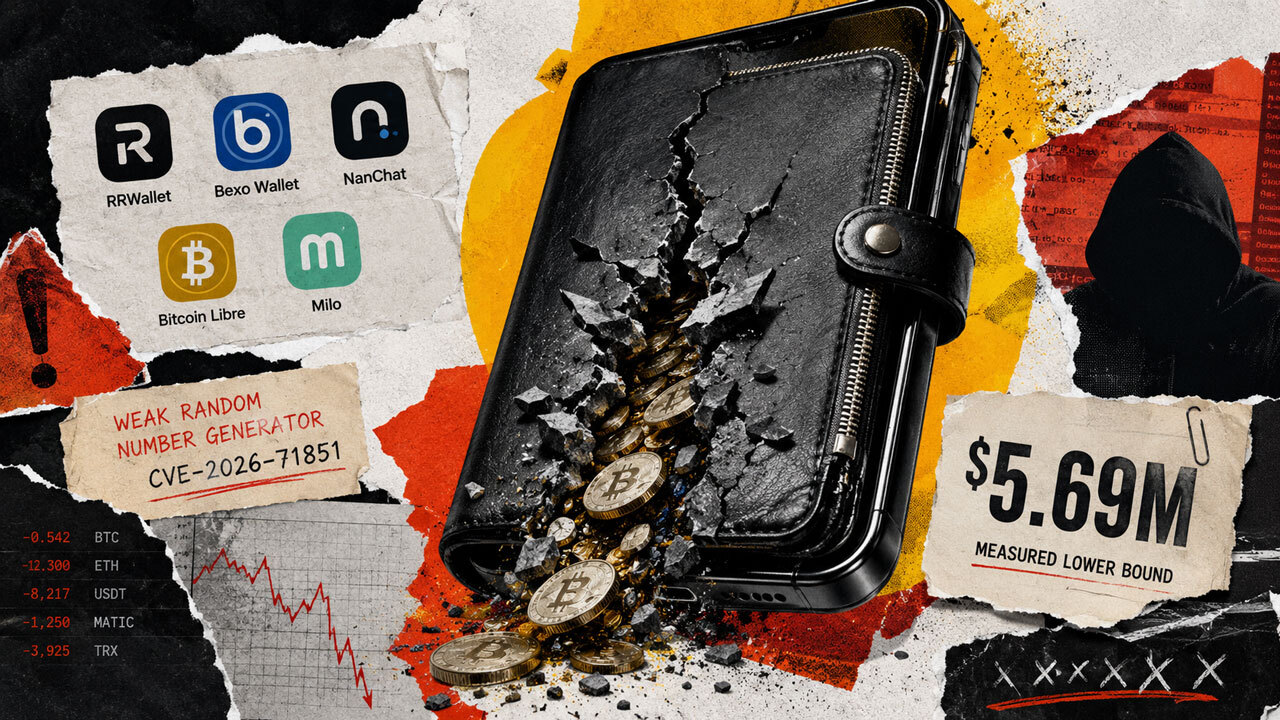
A flaw in software used by at least five crypto wallets made some recovery phrases predictable enough for attackers to reconstruct, contributing to at least $5.69 million in traced thefts since May.
Earlier this month, blockchain security firm Coinspect said RRWallet, Bexo Wallet, NanChat, Bitcoin Libre and Milo used a weak random-number generator from the CryptoJS library to create some crypto wallet recovery phrases.
According to the security firm:
“The vulnerable implementation was introduced in June 2014 as part of an attempt to strengthen WordArray.random() in response to GitHub issue #7, “randomBytes is not random enough”, and was implemented in commit ff1f003.”
Malicious attackers have targeted this vulnerability across multiple attack waves, with Coinspect tracing about $3.14 million drained on May 27 and another $2.55 million between May 30 and July 13.
The firm also stated that the attack had a third wave between July 20 and 21, which drained around $40,000 across the Chinese-mnemonic subset.
Cumulatively, the security firm's analysis covered more than 2,000 seeds with activity across Bitcoin, Ethereum, Tron, Rootstock, and Polygon, making the $5.69 million figure a lower bound rather than a measure of total losses.
Meanwhile, the affected crypto wallets list may not be exhaustive, and exposure depends on the software version that originally generated the phrase rather than the brand alone.
Related Reading A flaw in Coldcard seed generation lets attackers recreate private keys from the press of a button Weak randomness made wallet keys easier to guessA recovery phrase is the sequence of words that serves as a wallet’s master backup. It can be used to recreate the private keys controlling the wallet, meaning anyone who obtains or reconstructs the phrase can potentially move its funds.
Those phrases are supposed to be generated from randomness so vast that guessing them is computationally impractical.
Coinspect found that the vulnerable CryptoJS.lib.WordArray.random() function could reduce effective search spaces expected to contain 2^128 or 2^256 possibilities to roughly 2^39 and 2^47.
That reduction made affected phrases feasible to enumerate, derive into blockchain addresses, and check for funds. Simply having an older CryptoJS dependency does not establish exposure; the vulnerable function had to be used to generate the wallet secret.
Meanwhile, this weakness also means updating an app cannot fix a recovery phrase generated with insufficient randomness. Importing the same phrase into another software or hardware wallet also carries the vulnerability.
Coinspect said Bexo fixed the generation path in version 20.1.0, NanChat in version 1.3.0, and Bitcoin Libre in version 4. RRWallet and Milo have been discontinued. NanChat separately told users who created wallets before version 1.3.0 to consider them compromised and migrate to a newly generated phrase.
Coinspect has also released Unlukey, which lets users check public blockchain addresses against known exposed datasets without submitting private information. A match indicates potential exposure, while a negative result only means the address was not found in the published data.
For confirmed affected wallets, the remedy is to generate a new recovery phrase securely and move the funds it controls.
The post Crypto users lost at least $5.69 million because their wallet seeds were too predictable appeared first on CryptoSlate.
Why this matters
Bitcoin is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CryptoSlateRelated market context

US Charges Man After Crypto Scam Wallets Received More Than $53M
TL;DR U.S. prosecutors have charged a Vietnamese national with money laundering tied to alleged cryptocurrency “pig butchering” sc...
Bitget raises breach losses to $387.5 million after on-chain tracing uncovers Zcash and TRON transfers
Bitget raises breach losses to $387.5 million after tracing reveals Zcash and TRON transfers. Cold wallets secure, protection fund...

Bitget Halts Withdrawals After $351.6M Hot Wallet Incident Hits Crypto Exchange
Key Takeaways: Bitget reported unauthorized transactions of about $351.6 million that occurred in a portion of its hot & warm wall...
Bitget Confirms $387.5 Million Security Breach as Revised On-Chain Accounting Reveals Wider Losses
Bitget raises breach losses to $387.5 million after Zcash and TRON transfers found. Attackers spoofed backend transaction data to...
Bitget Confirms $351.6M Hot Wallet Breach And Pauses Withdrawals
Bitget says unauthorized transfers affected approximately $351.6 million held across parts of its hot and warm wallet infrastructu...
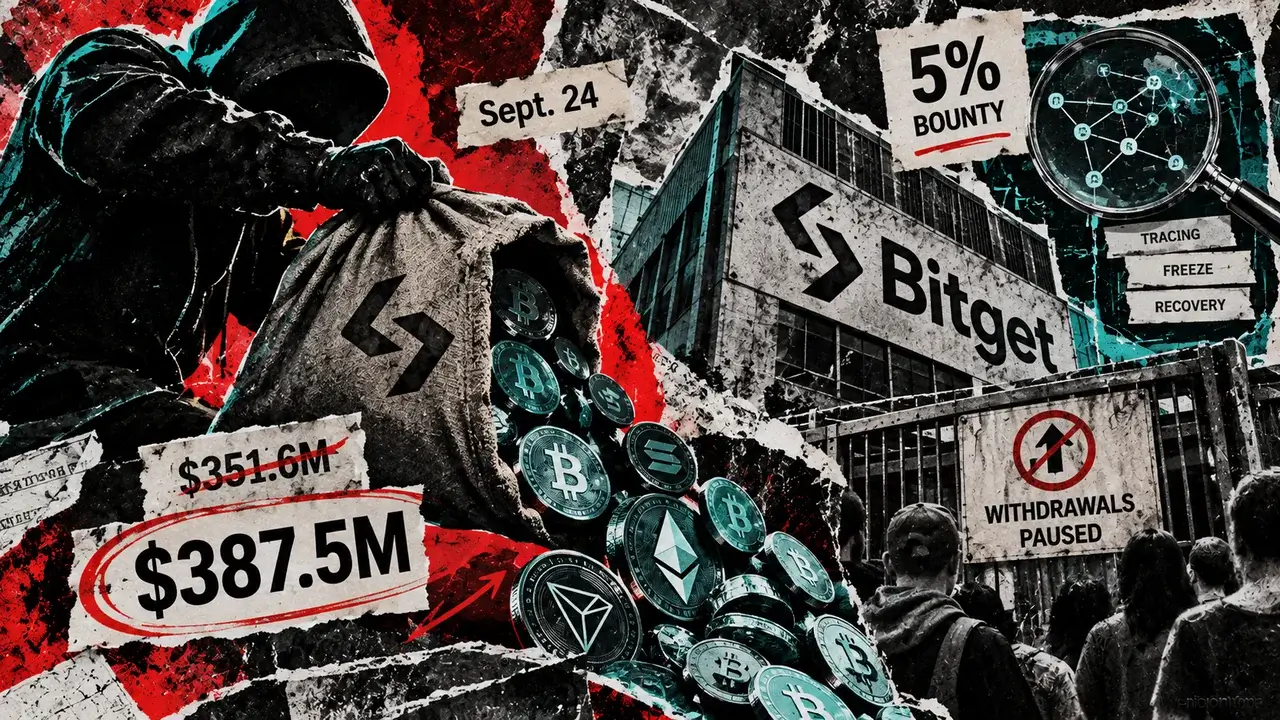
Bitget’s hack just got $36 million bigger, and now there’s a bounty on the stolen crypto
Bitget has raised the estimated value of assets taken in its Sept. 24 breach to $387.5 million as exchanges and security firms mob...