DeFi Platform TrustedVolumes Hit By $6.7M Hack As 2026 Exploits Surge
Another multi-million-dollar attack has hit the DeFi sector after liquidity provider and market maker TrustedVolumes fell victim to a smart contract exploit on Thursday night. TrustedVolumes Hit By $6.7M Hack On Thursday...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.

Another multi-million-dollar attack has hit the DeFi sector after liquidity provider and market maker TrustedVolumes fell victim to a smart contract exploit on Thursday night.
TrustedVolumes Hit By $6.7M HackOn Thursday, DeFi platform TrustedVolumes, one of 1inch liquidity providers and market makers, suffered a new exploit that drained millions of dollars in multiple assets from the project.
According to reports from blockchain security firms PeckShield and Blockaid, the attacker stole approximately $6 million in Wrapped Ethereum (WETH), Wrapped Bitcoin (WBTC), USDT, and USDT after exploiting a vulnerability in the protocol’s core signature validation logic, which allowed them to bypass authorization checks and forge trading orders.
Notably, the hacker quickly exchanged all assets for 2.513 ETH on a Decentralized Exchange (DEX) and distributed them across three addresses. In an X post, TrustedVolumes confirmed the incident, sharing the addresses currently holding the stolen funds and updating the estimated loss to roughly $6.7 million.
The vulnerability was a TrustedVolumes-controlled custom RFQ (request for quote) swap proxy. Crypto researcher Humphrey explained that “the Custom RFQ Swap Proxy contract contains a function designed to manage the ‘authorized order signer’ whitelist. Such whitelist mechanisms are common in DeFi—only addresses on the whitelist can issue valid transaction instructions on behalf of the protocol.”
However, he noted that “this registration function is public and lacks any permission modifiers.” As a result, the attacker exploited this public function within the contract, registering themselves as an authorized order signer.
“Since any external address can call this function, it is equivalent to giving everyone the ability to make a copy of the safe’s key,” the researcher continued.
Same Hacker, Different AttackThe online reports revealed that the attacker was the same hacker responsible for the $5 million 1inch Fusion V1 Settlement contract exploit in March 2025, which TrustedVolumes was the primary victim.
Humprey highlighted that while the same individual carried out both attacks, they were significantly different on a technical level. According to the post, the 2025 vulnerability involved low-level EVM memory manipulation in the 1inch Fusion V1 Settlement contract.
At the time, the hacker “proactively initiated on-chain negotiations,” offering to return the stolen assets for a white hat bounty. The DeFi platform accepted the proposal, and most of the funds were safely returned.
Now, TrustedVolumes affirmed that it is “open to constructive communication regarding a bug bounty and a mutually acceptable resolution.”
Decentralized exchange aggregator 1inch clarified that there was no impact on its systems, infrastructure, or user funds, explaining that “TrustedVolumes operate independently as a liquidity provider, used by multiple protocols across the industry, and are not exclusive to 1inch.”
DeFi Exploits See Historic SurgeThis attack follows a wave of exploits that has shaken the DeFi sector over the past month. Last week, PeckShield revealed that the crypto space saw 40 major hacks in April, which drained approximately $647 million.
This figure represents a 1,140% Month-over-Month (MoM) increase from March’s $52.2 million. It also represents a 292% surge from the $165 million the DeFi sector lost during the first quarter of 2026.
Notably, the top two incidents of the month, Drift Protocol’s $285 million and KelpDAO’s $290 million exploits, accounted for 91% of the funds lost last month. In addition, they now rank among the Top 10 hacks since 2021.
Why this matters
Ethereum is showing up inside the Stablecoins theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on NewsBTCRelated market context
SEC clears regulatory hurdle as crypto token buybacks hit record $638 million
Crypto projects spent about $638 million with token buybacks through late August 2026, according to Allium Labs data. That is alre...
Washington has $114 billion reasons to want Tether around
Not that long ago, Washington fined Tether for misleading people about the dollars behind its tokens. Today, the company's insatia...
Bitget Confirms $387.5 Million Security Breach as Revised On-Chain Accounting Reveals Wider Losses
Bitget raises breach losses to $387.5 million after Zcash and TRON transfers found. Attackers spoofed backend transaction data to...
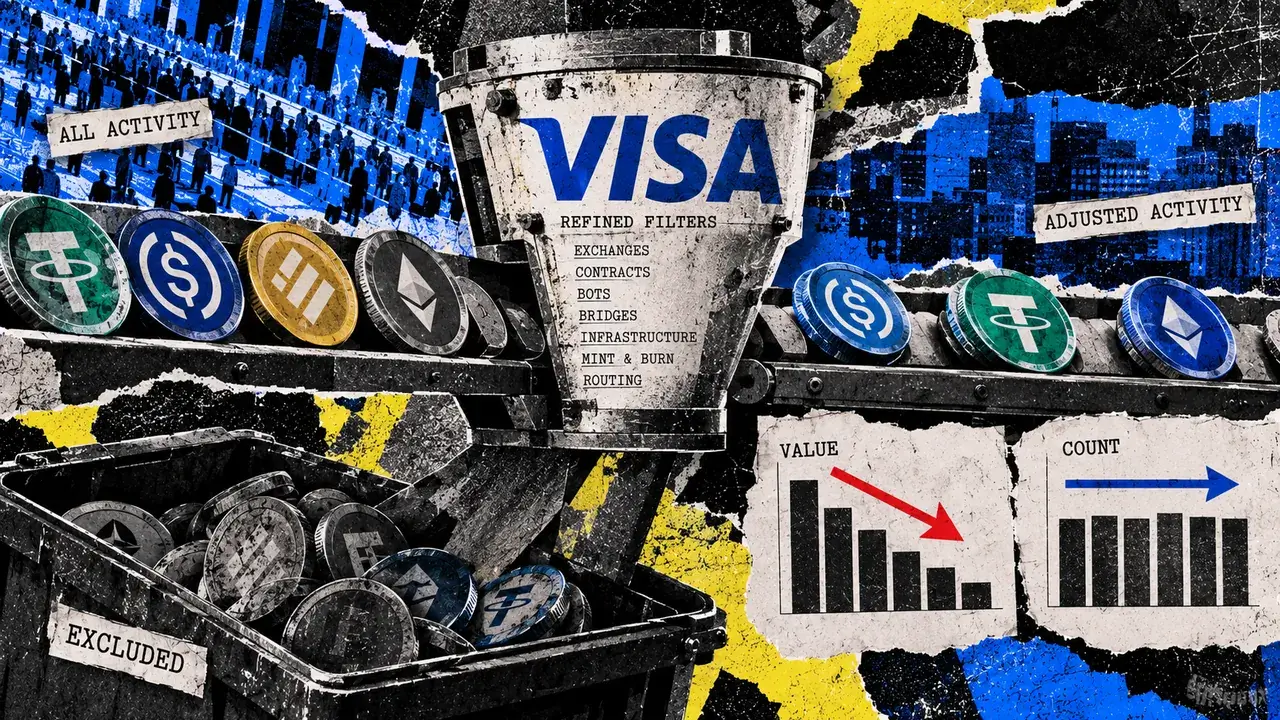
Visa cuts reported stablecoin volume but there’s no proof payments fell
Visa’s September 18 data refresh lowered its adjusted stablecoin volume measure, while its adjusted transaction count fell by less...
Ethereum is not instant, but collateral could make it feel that way
When a payment app tells you a transfer is complete, you start making decisions. You hand over whatever you've sold, spend the mon...
Elon Musk Grok AI Predicts a Bold Move for Ethereum in 2026
When prompted, the Elon Musk-backed Grok AI predicts a bold move for Ethereum (ETH) over the remainder of 2026. It claims that if...