DeFi protocol Grim Finance lost $30M in 5x reentrancy hack
An apparent security flaw in the Grim Finance protocol allowed the attacker to fake five additional deposits.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.

An apparent security flaw in the Grim Finance protocol allowed the attacker to fake five additional deposits.
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context
Aave Says V3.8 Security Proposal Preserves Flash-Loan Liquidations
Aave Labs has clarified that its proposed V3.8 security upgrade would preserve flash-loan liquidations. The October 23 response ad...
Bitcoin Core Rewrites Security Policy as LLMs Make Some Bugs Easy to Rediscover
Bitcoin Core has rewritten part of its security policy for an era of AI-assisted bug hunting. A policy update approved this week c...
Injective CEO meets White House, SEC and CFTC officials on onchain finance
The meetings highlight a potential shift towards regulatory acceptance, potentially paving the way for institutional adoption of D...
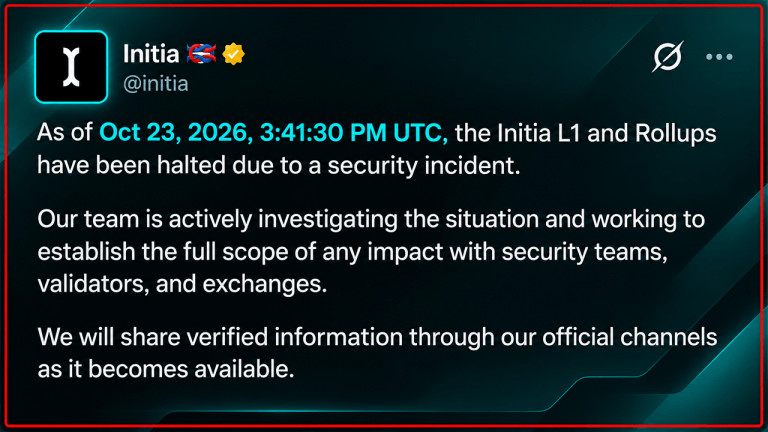
Hacker Prints $2.7M in Crypto as Initia Blockchain Grinds to a Halt
Modular blockchain platform Initia halted its network Friday after the team confirmed “a security incident” that compromised its o...
Bitcoin Core Ends Long Embargoes for Bugs AI Can Rediscover
Bitcoin Magazine Bitcoin Core Ends Long Embargoes for Bugs AI Can Rediscover Bitcoin Core has changed its security disclosure poli...
Bitcoin Core Changes Security Policy as AI Makes Vulnerabilities Easier to Find
Bitcoin Core is rewriting its approach to security vulnerabilities as artificial intelligence makes certain software flaws dramati...