ETH wallet exploit backfires as MEV bot captures $7.7M, Kelp freezes address
An MEV bot known as “Yoink” front-ran an attacker attempting to exploit a custom Safe module, capturing the stolen rsETH before Kelp temporarily froze the receiving address.
Watchlist
Published in the last two hours. A tracked entity is involved.

An MEV bot known as “Yoink” front-ran an attacker attempting to exploit a custom Safe module, capturing the stolen rsETH before Kelp temporarily froze the receiving address.
Why this matters
Ethereum is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CointelegraphRelated market context
Coinbase-backed Base just exposed the uncomfortable truth about Ethereum’s L2s
Ethereum and Coinbase-backed layer-2 network Base have abandoned an effort to agree on how the next generation of crypto wallets s...
Ethereum, Base wallet standards talks fail, Ethlabs researcher says
Ethereum and Base are pursuing different account abstraction designs after talks failed, according to Ethlabs researcher Derek Chi...

XRP News: XRPL Records 2K Transactions from 20 Wallets
The XRP Ledger processed a record 3,254 transactions in ledger 106,965,249 yesterday, but 2,000 of the news came from just 20 acco...
DeFi stalwart Balancer mulls shutdown after $130M hack
Once a household name in the DeFi sector, decentralized exchange Balancer is considering calling it quits. In a proposal posted to...
How a simple coding mistake let a hacker drain $7.8 million from a crypto wallet
Security firms traced the $7.8 million loss to a helper contract the wallet owner had authorized, not to Safe itself.
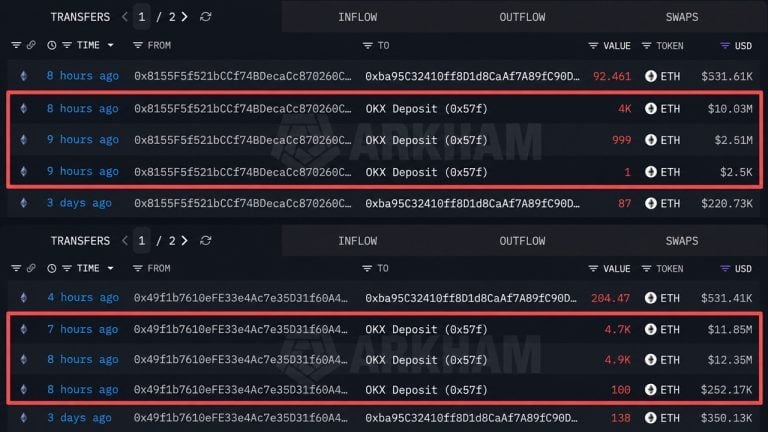
Ethereum Whale From 2021 Moves $37M Worth of ETH to OKX at a Loss
Two wallets that had been quiet for more than a year moved 14,700 ETH, worth about $36.94 million, into OKX on Sept. 14, and oncha...