Hacker Tries to Attack XRP Ledger Using Developer Access, Security Team Stops It
A potential security crisis was narrowly avoided after a hacker exploited a developer’s access token to inject malicious code into a key toolkit used by applications on the XRP Ledger.The vulnerability, identified by Aik...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.

A potential security crisis was narrowly avoided after a hacker exploited a developer’s access token to inject malicious code into a key toolkit used by applications on the XRP Ledger.
The vulnerability, identified by Aikido Security researcher Charlie Eriksen, could have led to a major supply chain attack across the crypto ecosystem.
Hacker Exploits NPM Token to Publish Malicious xrpl.js Versions on XRP LedgerAccording to Aikido Security, the attacker gained access to a developer’s Node Package Manager (NPM) token, allowing them to publish compromised versions of xrpl.js, the official JavaScript library for interacting with the XRP Ledger.
With over 140,000 weekly downloads, the package is widely integrated into hundreds of thousands of apps and websites, raising concerns over the potential scale of the breach.
“This could have been catastrophic,” Eriksen warned in a security update, noting that the flaw theoretically allowed attackers to steal private keys, putting crypto wallets at risk.
The malicious code was detected on April 21, when Aikido’s monitoring system flagged five suspicious package versions.
We have discovered a backdoor in the official #xrpl NPM package. This back door steals private keys and sends them to attackers. The affected versions 4.2.1 – 4.2.4, if you are using an earlier version, do not upgrade.#crypto #malware #npm pic.twitter.com/wshcTFKjbR
— Aikido Security (@AikidoSecurity) April 22, 2025Fortunately, major XRP-related platforms such as Xaman Wallet and XRPScan confirmed they were unaffected.
The risk was limited to third-party applications that installed the compromised versions—v4.2.1 through v4.2.4 and v2.14.2—during a short window before the issue was contained.
The XRP Ledger Foundation responded swiftly, deprecating the affected versions and releasing a patched update, v4.2.5, urging all developers using xrpl.js to upgrade immediately.
The foundation clarified that the core XRP Ledger codebase and its GitHub repository remained untouched, as the vulnerability was isolated to the external JavaScript library.
While the identity of the hacker remains unknown, Aikido Security hinted at having leads under investigation.
With today’s npm vulnerability, it’s a clear reminder about truly knowing what you’re using.
At Xaman, our track record speaks for itself.
We’ve been feature-complete, security-first from day one, building everything in-house.
No shortcuts.
This is what trust looks like. https://t.co/LH1nEFrlPH
Despite the scare, XRP prices showed resilience, rising 8.5% over the past 24 hours amid a broader crypto market rally.
SEC Lawsuit Against Ripple Labs Concludes After Four YearsThe legal dispute between Ripple Labs and the U.S. Securities and Exchange Commission (SEC) has concluded after more than four years, marking a significant development in cryptocurrency regulation.
In December 2020, the SEC filed a lawsuit against Ripple Labs, alleging that the company conducted an unregistered securities offering by selling XRP tokens, raising over $1.3 billion.
Ripple contested the claim, arguing that XRP is a digital currency, not a security.
In July 2023, U.S. District Judge Analisa Torres delivered a mixed ruling: she determined that XRP sales to institutional investors violated securities laws, while sales on public exchanges did not.
Consequently, Ripple was ordered to pay a $125 million civil penalty.
In March 2025, Ripple and the SEC reached a settlement. Under the agreement, Ripple would pay $50 million of the previously imposed fine, with the remaining $75 million returned to the company.
Both parties agreed to drop their respective appeals, effectively ending the litigation.
The post Hacker Tries to Attack XRP Ledger Using Developer Access, Security Team Stops It appeared first on Cryptonews.
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CryptonewsRelated market context
Bitget hacker withdraws $1.23M from Binance, funnels funds to attacker-controlled wallet
The Bitget hack highlights vulnerabilities in crypto exchanges, prompting urgent calls for enhanced security measures and internat...
XRP News: Bitget Hacker Moves 54M XRP, Putting Fresh Selling Pressure
The attacker behind Bitget’s $388 million news driver has moved about 54 million stolen XRP out of three of the five wallets that...
Ledger Opens 24/7 Tokenized Stocks to Millions With xStocks Integration
Key Takeaways: Ledger and a new partnership with Payward have brought xStocks to the Ledger wallet ecosystem. Eligible Ledger hold...

Ripple CEO Brad Garlinghouse Says XRP and Solana Can Both Thrive in Crypto’s Next 5 Years
Garlinghouse’s comments have resurfaced as XRP and Solana both trade near important technical levels following recent gains. “I’m...
XRP News: Ripple Takes Aim at SWIFT, Pantera CEO Says
Dan Morehead, founder and CEO of Pantera Capital, told CNBC News that Ripple is going after the cross-border payments turf long do...
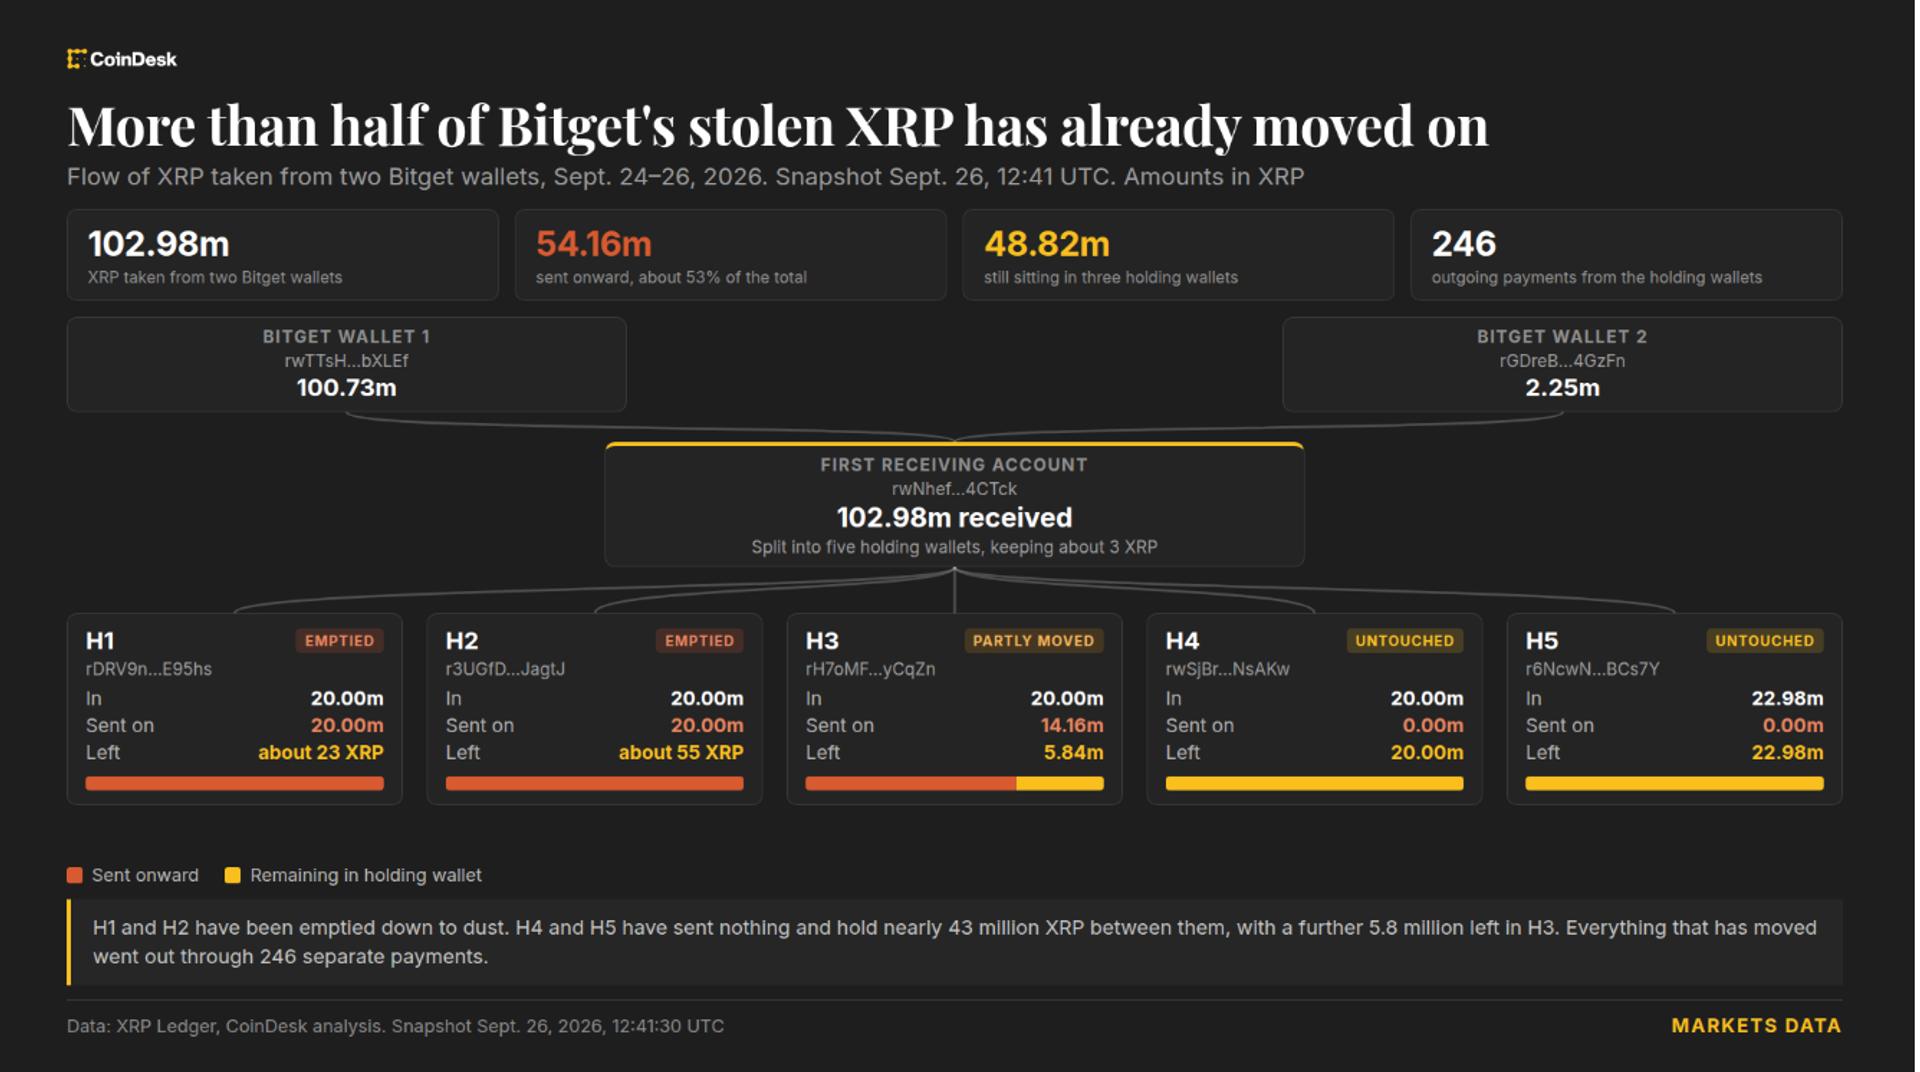
Bitget hacker moves $83 million in stolen XRP that Ripple cannot freeze
Two wallets have been almost emptied and a third is being drained, with about $75 million remaining across the five original holdi...