How a hacker reused the same authorization message 1,490 times to trigger massive crypto payout loops
According to the ICON Foundation, the Aug. 27 ICON replay exploit released 119,866,000 ICX and 531,600 bnUSD from foundation-held assets after two legitimate withdrawal messages were reused 1,492 times. Its Aug. 30 postm...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
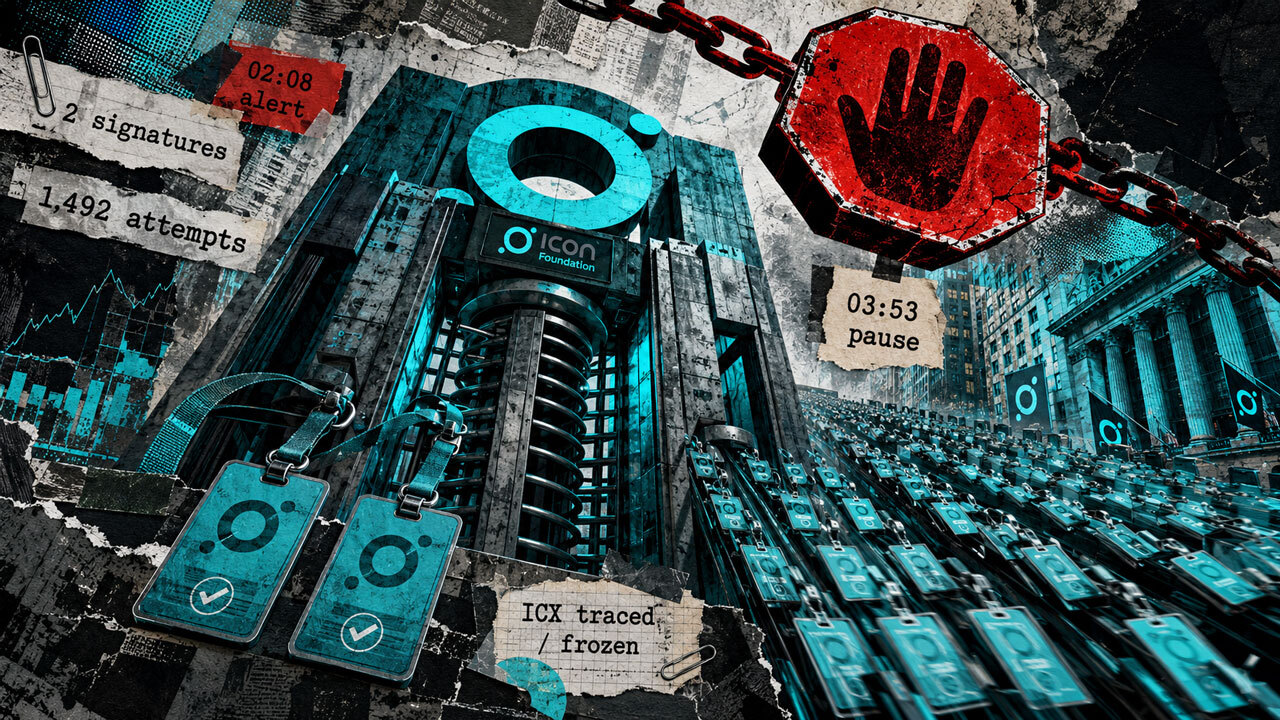
According to the ICON Foundation, the Aug. 27 ICON replay exploit released 119,866,000 ICX and 531,600 bnUSD from foundation-held assets after two legitimate withdrawal messages were reused 1,492 times. Its Aug. 30 postmortem said 1,490 calls succeeded, while no user deposits, balances or positions were accessed.
The headline-sized ICX release is not the same as the confirmed loss. ICON put net loss to date at about 150.2 ETH plus 31,204 USDC, with the vast majority of the ICX traced, frozen and in active recovery. The foundation said bnUSD and SODA were recovered in full, but exchange-held amounts remain subject to revision. That distinction matters because ICON had not received exact exchange figures for how much ICX was held, converted or withdrawn.
Related Reading Harmony weighs a full blockchain rollback after unauthorized minting floods exchanges with billions in ONEThe flaw let the attacker change part of a withdrawal identifier without changing the signed payload being verified. ICON traced the mismatch to a change intended to standardize withdrawal messages at 32 bytes, which routed part of the serial number through float64-range logic rather than exact integer arithmetic.
As a result, the contract's uniqueness check looked at high bits the attacker could vary, while cryptographic verification covered the unchanged low 256 bits. The signed payload and signature remained identical within each replay set, but the altered unsigned portion made the calls appear unique. Two calls reverted; every successful call credited the same relayer wallet. ICON said the flaw was specific to its implementation because other supported chains used fixed-width integers that could not produce the same mismatch.
Related Reading Polkadot Hyperbridge April Fools’ joke comes true as over 1 Billion fake DOT tokens were minted on Ethereum
ICON's monitoring system fired at 02:08 UTC, seven minutes after the exploit began. Technical staff started investigating at about 03:40, a 92-minute gap. The affected contract was paused at 03:53, 105 minutes after the alert.
The attacker had begun splitting ICX across exchange deposit addresses at 02:44, according to ICON, and the distribution continued until about 05:20. The foundation said an ICON-side pause could not stop movement of funds already swept into exchange custody.
The network was halted at 06:18:54 and resumed at about 07:51 the next day, roughly 25 hours later. Public notices from Bitvavo, Bitget and KuCoin confirm that ICX deposits and withdrawals were suspended around the incident, though none identifies itself as holding attacker funds or verifies the amount frozen.
Related Reading Crypto users told to pull funds after Ethereum L2 bridge failure exposes rollup exit riskA November 2025 relay audit reviewed selected relay and verifier code, including ICON verifier files, but its published scope did not list the affected migration-contract source. None of its nine disclosed findings flagged the serial-number mismatch. ICON said incident-related relay logic had been audited, but that the gap fell outside the findings.
The post How a hacker reused the same authorization message 1,490 times to trigger massive crypto payout loops appeared first on CryptoSlate.
Why this matters
Ethereum is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CryptoSlateRelated market context

Coinbase Tracks $1.1M Crypto Trail as Microsoft Takes Down 175 EvilTokens Domains
Key Takeaways: Between October 2025 and June 2026, approximately $1.1 million was traced from several Tron addresses belonging to...
ECB and EU Central Banks Want the Stablecoin Yield Ban to Reach Lending and Staking
The European Central Bank and the EU’s national central banks asked the European Commission to extend MiCA’s ban on paying interes...

BTC USD Fights For $85K: Bitcoin Price Prediction Says $90K Still in Play
Bitcoin is trading at $85,954, down 0.8% on the day after briefly tagging $86,922 earlier in the session. That pullback from the h...
Coinbase users can now borrow USDC against bitcoin at a fixed rate
Coinbase now allows users to borrow the USDC stablecoin against their bitcoin at a fixed interest rate and repayment date.
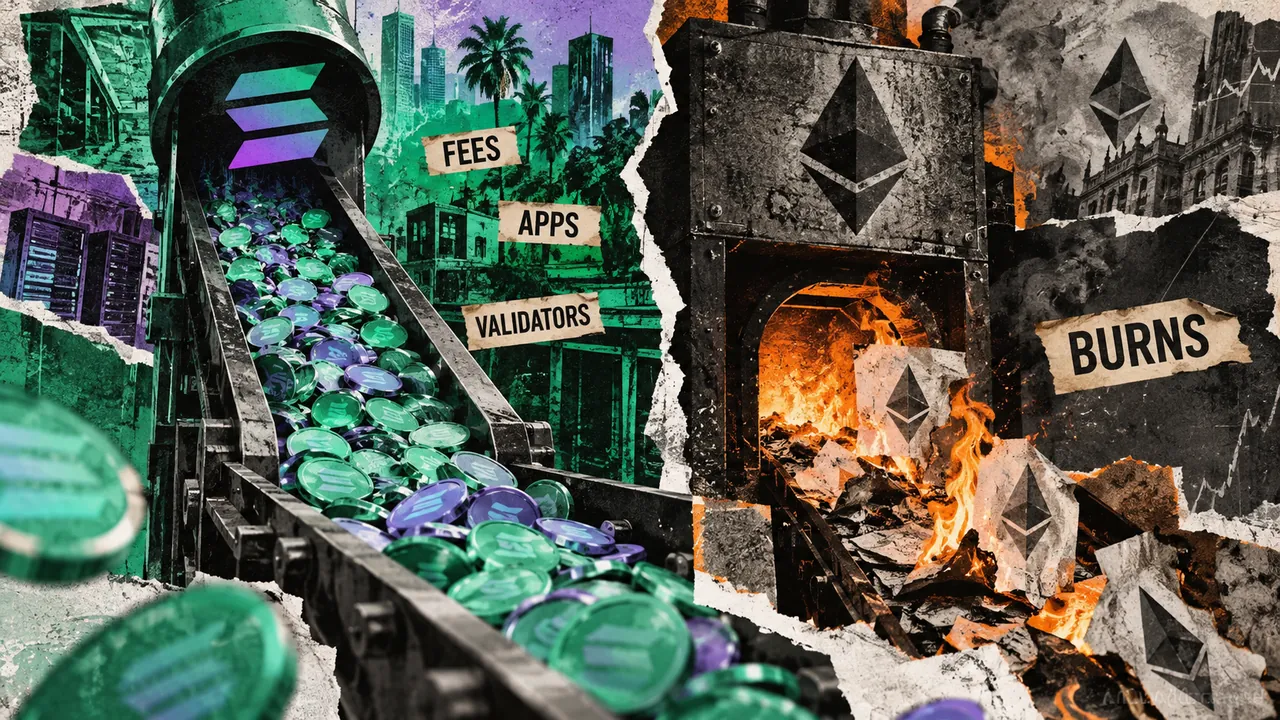
Solana flips Ethereum in fees, while ETH holds the burn lead
Solana generated more user fees than Ethereum in data provider DefiLlama's Sept. 22 dashboard snapshot, while Ethereum burned more...

Microsoft Copilot AI Predicts a Huge Move for Bitcoin by 2027
Microsoft Copilot AI predicts that if a full-blown bull market returns in Q4, Bitcoin could hit $180,000 before January 1, 2027. T...