Reusing Bitcoin Addresses Can Lead To Private Keys Being Stolen
Only using Bitcoin addresses one time is best practice. By using addresses more than once, users give up information that can result in negative outcomes.Listen To This Episode:Apple SpotifyGoogleLibsynOvercastIn this ep...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Only using Bitcoin addresses one time is best practice. By using addresses more than once, users give up information that can result in negative outcomes.
Listen To This Episode:
In this episode of “Bitcoin, Explained,” hosts Aaron van Wirdum and Sjors Provoost discuss reusing Bitcoin addresses. More specifically, they explain why reusing Bitcoin addresses is a bad idea.
Reusing Bitcoin addresses is a bad idea for roughly three reasons. The first two of these are that it harms privacy and impedes on Bitcoin’s censorship resistance . In the episode, van Wirdum and Provoost go over a couple examples of how such a loss of privacy and censorship resistance can negatively affect bitcoin users.
The third reason that reusing Bitcoin addresses is a bad idea is because it opens up the possibility of some niche attacks. In certain cases, attackers could extract private keys from signatures after coins are first spent from an address — though this does require that a wallet implemented the signing algorithm incorrectly in the first place. There are also some potential future scenarios where quantum computers could extract private keys from signatures if addresses are reused.
Another type of niche attack is a timing side-channel attack, such as the recently disclosed “Hertzbleed Attack.” Provoost explains that attackers can potentially derive a private key from a wallet by closely monitoring how the computer that hosts the wallet behaves when signing a transaction. This attack is more plausible if addresses are reused.
These aforementioned examples are some of the reasons why bitcoin users should refrain from using addresses more than once. Address reuse hurts users’ privacy and can potentially lead to a Hertzbleed Attack.
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on Bitcoin MagazineRelated market context
Ethereum Foundation Launches Privacy Tool That Cuts the Link Between AI Prompts and Payers
The Ethereum Foundation has launched zkAPI, a system for paying for AI models and other metered online services without that usage...
BitMart Proposes Court-Backed Plan Offering Users Payouts or Tokens Tied to Its 2021 Hack
BitMart has published a preliminary plan for repaying its users, more than two months after the crypto exchange began winding down...

Following the Bitget Hack: BitOK Traces 87.8 BTC as Stolen Funds Reach Mixers
Research and reporting by Alexander Manev, BitOK. Reporting and adaptation by Brave New Coin. Investigators following the Bitget h...
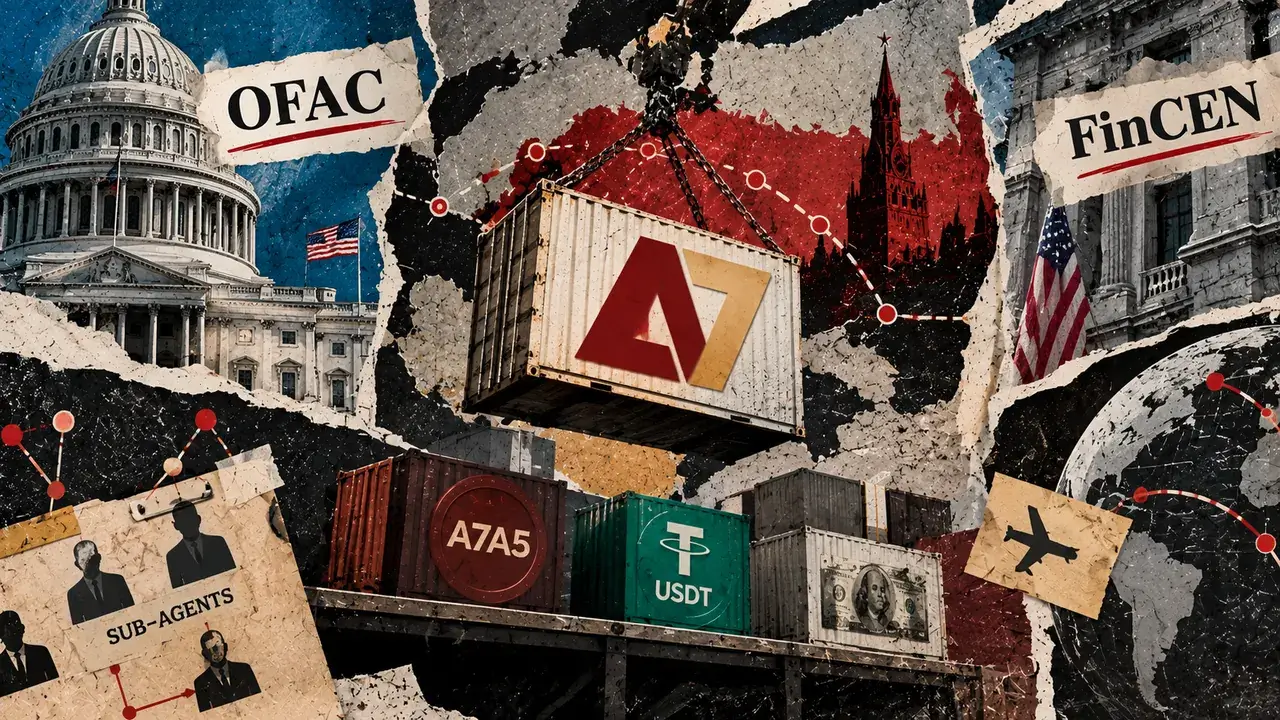
US targets $17 billion Russia-linked crypto payment network using USDT as an escape route
The US sanctioned the Russia-linked A7 Network and proposed new restrictions to cut its crypto intermediaries off from global mark...
Tether brings USDT back to Bitcoin with private transfers and swaps
Tether's USDT return to Bitcoin could reduce reliance on wrapped tokens, enhancing privacy and potentially reshaping crypto financ...

Solana Perps Exchange Drift Opens Recovery Token Claims for Users Who Lost Over $290 Million
The Drift Foundation opened claims and redemptions on Thursday for DFX, a Solana token issued to users of the perpetuals exchange...