Scammers use Gmail dot alias trick to spoof Robinhood in phishing scam
Visiting the fake login website alone isn’t enough for hackers to gain entry to accounts. However, entering sensitive information such as passwords could grant them access.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.

Visiting the fake login website alone isn’t enough for hackers to gain entry to accounts. However, entering sensitive information such as passwords could grant them access.
Why this matters
Robinhood is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CointelegraphRelated market context
Fake Claude trading bot tutorials drain $517K from 224 crypto users
The rise of AI-driven scams highlights the urgent need for enhanced user education and robust security measures in the crypto spac...
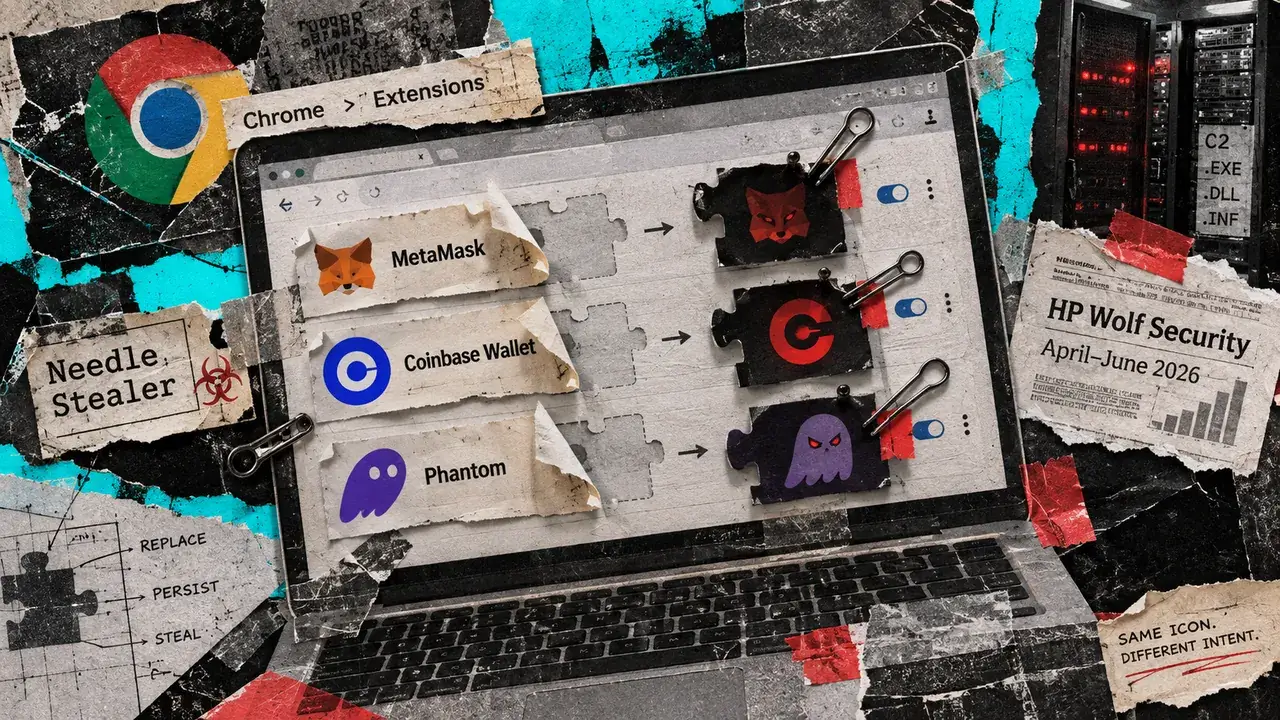
Fake AI crypto software is secretly replacing browser wallet extensions
HP Wolf Security, the company's threat-research team, said a fake AI crypto-trading assistant distributed malware that could repla...
0G expands wrapped token to Ethereum, Solana, Base, and Robinhood Chain
0G's token expansion across major networks enhances cross-chain interoperability, potentially accelerating decentralized AI and bl...

North Korean fake recruiters infect 30K devices, steal $10.7M in crypto
North Korean cyber group WaterPlum targeted developers with fake jobs at crypto, AI and NFT companies, infecting at least 30,000 d...

S&P Global Agrees To Acquire Smart Contract Security Firm OpenZeppelin
TL;DR S&P Global has agreed to acquire OpenZeppelin. OpenZeppelin is one of the best-known smart contract security and auditing fi...
Standard Reserve wants to become the liquidity backbone for Robinhood’s tokenized stock market
TSR's liquidity boost could stabilize Robinhood's tokenized stock market, attracting institutional interest and fostering new fina...