SuperRare $730,000 exploit was easily preventable — Experts weigh in
A critical access control bug in SuperRare’s staking contract — easily detectable by unit tests or even ChatGPT — allowed an attacker to steal $731,000 in RARE tokens.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
A critical access control bug in SuperRare’s staking contract — easily detectable by unit tests or even ChatGPT — allowed an attacker to steal $731,000 in RARE tokens.
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context

Best Crypto Staking Platforms for 2026: 7 Options Compared
Staking is the closest thing crypto has to earning interest: you lock up a proof-of-stake asset to help secure its network, and in...
SEC staff’s staking-token split spotlights the exit risks behind staked ETH tokens
An ETH holder can sell a liquid-staking token while the ETH behind it remains staked. A Sept. 25 SEC staff FAQ draws a conditional...
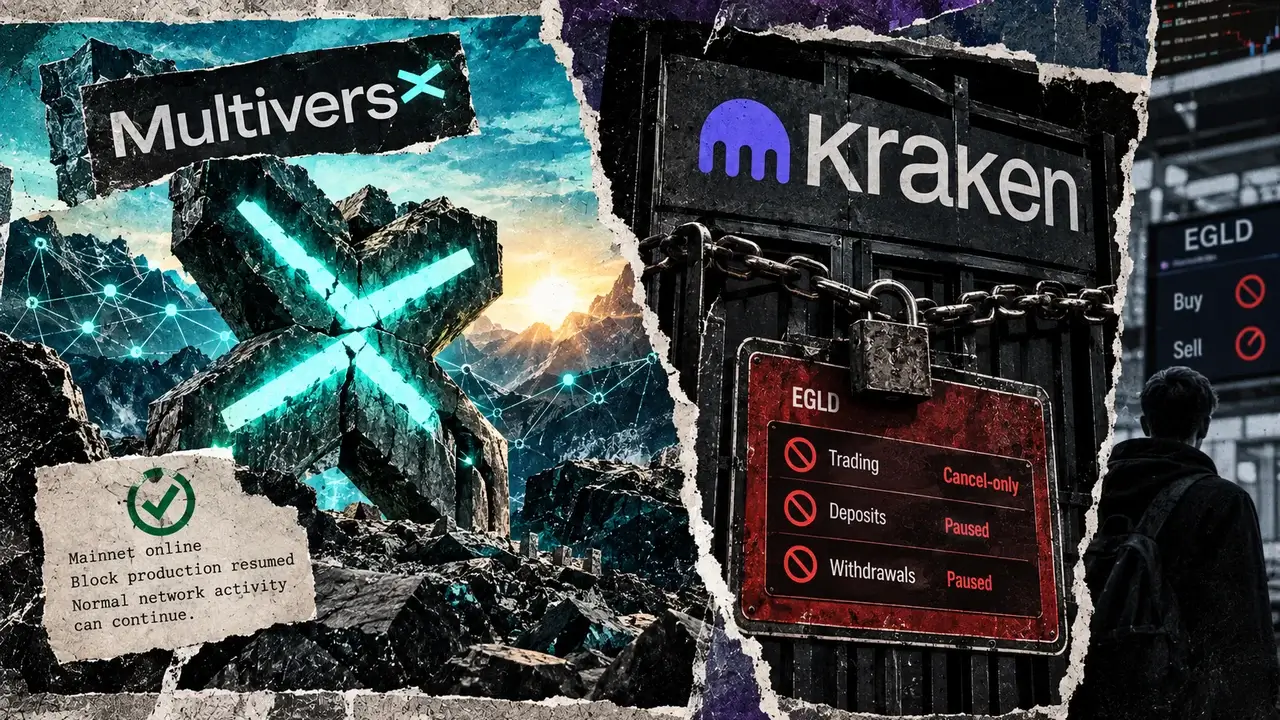
MultiversX restarts after exploit halt, but Kraken still bars new EGLD trades
MultiversX, a blockchain network, said its mainnet was back online Thursday, Sept. 24, about five days after an exploit-related ha...
SEC clears regulatory hurdle as crypto token buybacks hit record $638 million
Crypto projects spent about $638 million with token buybacks through late August 2026, according to Allium Labs data. That is alre...
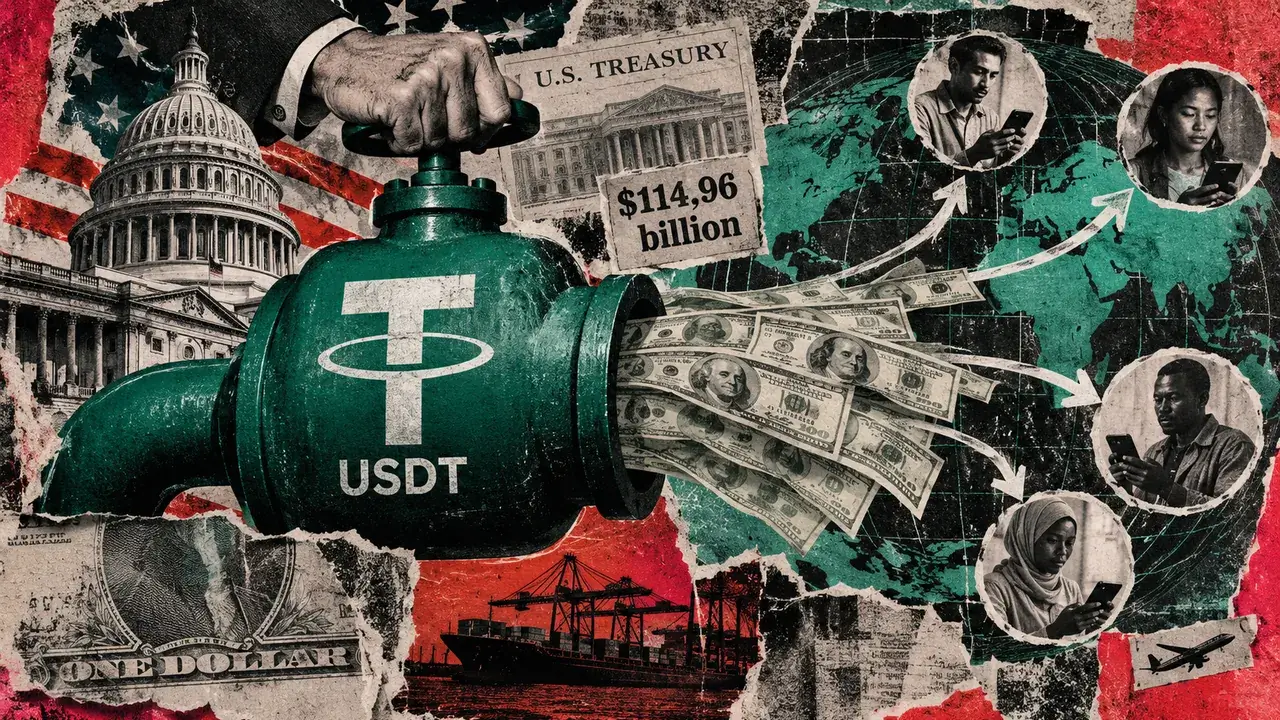
Washington has $114 billion reasons to want Tether around
Not that long ago, Washington fined Tether for misleading people about the dollars behind its tokens. Today, the company's insatia...
DeFi hack attack: Three exploits snatch $11M in a single day
Crypto and DeFi projects continue to be hacked at a dizzying pace, and few days in recent weeks have been incident-free. That said...