Trezor Shipping Partner Breach Exposes 27,000 Orders, Raising Crypto Phishing Risks
Key Takeaways: Data on approximately 27,000 orders was revealed after a breach of Trezor’s shipping partner, Skladon. The affected records included names, addresses, phone numbers and purchase information, among other th...
Watchlist
Fresh in the current trading session. A tracked entity is involved.

Key Takeaways:
- Data on approximately 27,000 orders was revealed after a breach of Trezor’s shipping partner, Skladon.
- The affected records included names, addresses, phone numbers and purchase information, among other things.
- Trezor states that they are safe at this time, but the risk of phishing becomes greater to the customer.
User Score
8.7
Follow us on Google NewsTrezor has warned customers about a data breach at logistics partner Skladon that exposed personal information linked to roughly 27,000 hardware wallet orders. The incident introduces a new phishing and physical security risk since the bad guys can now know both the buyer of a crypto wallet and its delivery address.
Skladon Breach Exposes Hardware Wallet Order DataSkladon reported on Nov. 15 to Trezor that the attackers had accessed the company’s systems with unauthorized access for customer shipping information. The leak happened on Nov. 7, Trezor said. The leaky data is from orders from Aug. 9 to Nov. 7, 2026.
These details were exposed: entire names, telephones, e-mail addresses, delivery addresses and order information including purchased products. Trezor suspects the source of the attacking data has been exported, and as far as it can determine, it is still ongoing.
Trezor emphasized that it was not the infrastructure of theirs being hacked. The leak didn’t include wallet backups, PINs & passphrases, and neither Trezor nor Skladon saves PINs and passphrases.
Read More: Coinone Customer Data Breach Sparks Fresh Phishing Risk for South Korean Crypto Users
Real Order Details Could Make Phishing More ConvincingThe greatest danger now is scams created from the real customer data.
Some users have already reported receiving calls they deemed to be scams due to the event, Trezor said. If an attacker provides a name, hardware wallet type, hardware wallet price or other delivery data, email, text or a physical letter would seem genuine.
The company warned anyone else who was using Trezor to watch out for this kind of operation, stating that it will never cold-call nor ask for their wallet backup. Support services should be called directly from the Trezor website, not via links, QR codes or numbers provided in spam messages.
Home addresses were leaked as well, and that’s why Trezor noted there were potential physical security issues if the customer that bought it revealed that they were a crypto owner.
Trezor Expands Anonymous Pickup After the BreachCurrently, Trezor is cutting down on personally identifiable data needed for shipping of the hardware wallets.
For its Anonymous Pickup service, it operates in 18 European countries and lets its clients collect items from lockers and/or collect points without sharing their real name, home address, or telephone number with Trezor.
The firm is also reducing the amount of time it retains order data, now from 90 to 45 days and will further slice that down. Shipping partners will be required to have the same retention policy.
Trezor Reviews Third-Party Security ControlsThe Skladon incident comes on the heels of another 2026 incident that occurred with a different Trezor fulfillment partner, ShipMonk, that impacted over 80,000 users. Trezor has stated it is looking at its ties with third party logistics providers and the measures used to appoint them.
The incident demonstrates that while self-custody safeguards private keys, it doesn’t remove potential risks associated with the manufacturing and delivery of physical crypto wallets.
Read More: Binance Warns of EU MiCA Licensing Risk as Millions Await Crucial June 30 Decision
The post Trezor Shipping Partner Breach Exposes 27,000 Orders, Raising Crypto Phishing Risks appeared first on CryptoNinjas.
Why this matters
Binance is showing up inside the Security Incidents theme, so this story is worth tracking for follow-through rather than treating it as a one-off headline.
Original source
Read on CryptoNinjasRelated market context
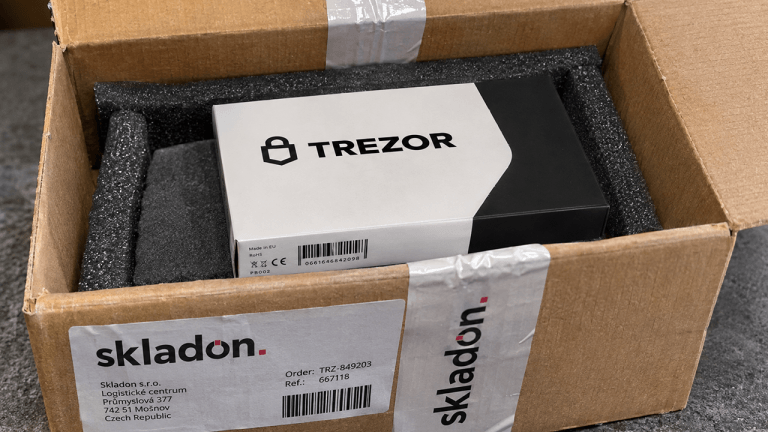
Hackers Strike Trezor Shipping Partner, Exposing Wallet Buyers’ Personal Details
Hardware wallet manufacturer Trezor disclosed Monday, Nov. 16, 2026, that a security breach at shipping partner Skladon exposed pe...
Bitcoin Wallet Maker Trezor Says Customer Data Was Exposed Again
A second Trezor shipping partner was breached in three months, exposing buyers' addresses and order details.
Binance Says Withdrawals Reopened on 87 Networks as Recovery Moves Toward Full Access
TL;DR Binance's November 14 update says withdrawals reopened on 87 networks during the week. The exchange targets the remaining ro...
Aster Says It Tightened Security After API Wallet Leak
A trader alleges $4.56 million in unauthorized transfers. CEO Leonard told users with suspected key exposure to delete the affecte...
Unocoin Estimates $200,000 Loss as Backup-Key Finding Explains Wallet Transfers
TL;DR Unocoin estimates a $200,000 cryptocurrency loss and says it will cover it. BitGo says the affected Ethereum transfers used...
Trezor patches crypto wallet spy chips but warns users a new device may not be enough
Trezor says firmware 2.13.1 blocks identified implants, but CryptoBilis buyers covered by its warning still need new seeds and fun...