UXLINK plunges 77% after multisig wallet breach
The breach highlights the critical need for robust security measures in crypto projects to maintain investor trust and market stability. The post UXLINK plunges 77% after multisig wallet breach appeared first on Crypto B...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
The breach highlights the critical need for robust security measures in crypto projects to maintain investor trust and market stability.
The post UXLINK plunges 77% after multisig wallet breach appeared first on Crypto Briefing.
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on Crypto BriefingRelated market context

Safepal Hardware Wallet Users Receive Fake Security Alerts in the Mail
Safepal customers in Italy are reportedly being targeted by a sophisticated phishing campaign involving fraudulent letters contain...
Why the Path to Quantum Resistance Runs Uphill for Wallet Manufacturers
Bitcoin custody has always involved some degree of risk, but wallet manufacturers like Trezor — which build physical devices desig...
BitGo Denies Breach as Unocoin Probes Wallet Transfers
BitGo says the disputed transfers used Unocoin-held keys without its participation. The exchange suspects misuse of a backup mecha...
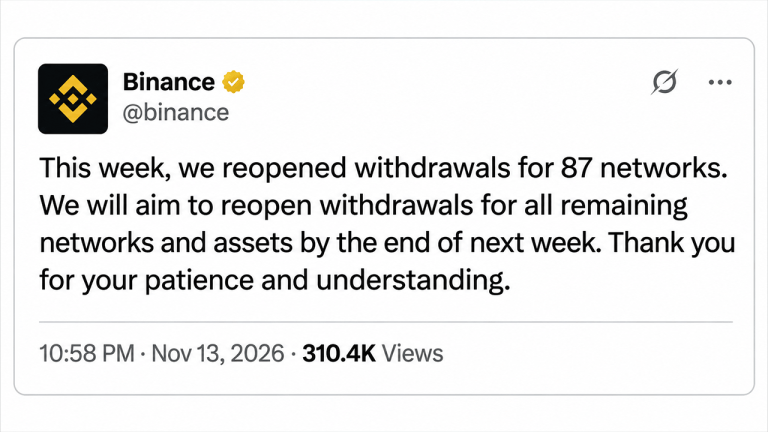
Binance Reopens 87 Networks Following Historic $6.3 Billion Breach
Binance has reopened withdrawals across 87 blockchain networks as the cryptocurrency exchange continues recovering from its devast...
Santiment ranks Dash, Chainlink and HOPR as top privacy projects by development activity
The ranking highlights a shift towards integrating privacy features into broader crypto infrastructure, indicating evolving priori...
Foundation CEO Zach Herbert urges hardware wallet makers to build locally
Local manufacturing of hardware wallets could enhance security by minimizing supply chain vulnerabilities, potentially reshaping i...