Ledger secures Discord after hacker bot tried to steal seed phrases
Hardware wallet provider Ledger has confirmed its Discord server is secure again after an attacker compromised a moderator’s account to post scam links on May 11 to trick users into revealing their seed phrases on a thir...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Hardware wallet provider Ledger has confirmed its Discord server is secure again after an attacker compromised a moderator’s account to post scam links on May 11 to trick users into revealing their seed phrases on a third-party website.
“One of our contracted moderators had their account compromised, which allowed a malicious bot to post scam links in one channel,” Ledger team member Quintin Boatwright wrote on the Ledger Discord server.
“The issue was quickly contained: the compromised account was removed, the bot was deleted, the website was reported, and all relevant permissions were reviewed and secured.”Some members in Ledger’s Discord channel claimed the attacker abused moderator privileges to ban and mute them as they tried to report the breach, possibly slowing Ledger’s reaction.
Boatwright said the security breach was an isolated incident and that Ledger has taken additional measures to strengthen its security on Discord, a chat platform many crypto projects use to share protocol developments and engage with their community.
Using the compromised Ledger community manager account, the hacker told Ledger Discord members that there was a recently discovered vulnerability in the firm’s security systems and strongly urged all users to verify their recovery phrases with a scam link, according to several screenshots shared on X.
Ledger users were asked to connect their wallets and follow on-screen instructions.
Source: ecurrencyholder
It isn’t clear whether anyone was affected by the security breach. Cointelegraph has reached out to Ledger for comment.
In April, scammers were mailing physical letters to owners of Ledger hardware wallets, asking them to validate their private seed phrases in a bid to access and empty the wallets.
The letter used Ledger’s logo, business address and a reference number to feign legitimacy and asked users to scan a QR code and enter the wallet’s recovery phrase.
One Ledger user who received the letter speculated whether scammers were sending letters to Ledger customers whose data was leaked in July 2020.
Related: Jameson Lopp: Most don’t realize how easy self-custody has become
That incident saw a hacker breach Ledger’s database and dump the personal information of over 270,000 of its customers online, which included names, phone numbers and home addresses.
The following year, several Ledger users claimed to have been mailed fake Ledger devices that were tampered with and designed to install malware upon use, Bleeping Computer reported at the time.
Magazine: ChatGPT a ‘schizophrenia-seeking missile,’ AI scientists prep for 50% deaths
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on CointelegraphRelated market context
This blockchain just voted to shut itself down for a Solana-powered AI pivot
ZetaChain's on-chain governance has approved retiring the network’s standalone blockchain and moving ZETA to Solana as the project...
EU staking review threatens crypto yields and network security could pay the price
Some of the most consequential financial rules begin with surprisingly little text. For example, on page 36 of the European Commis...
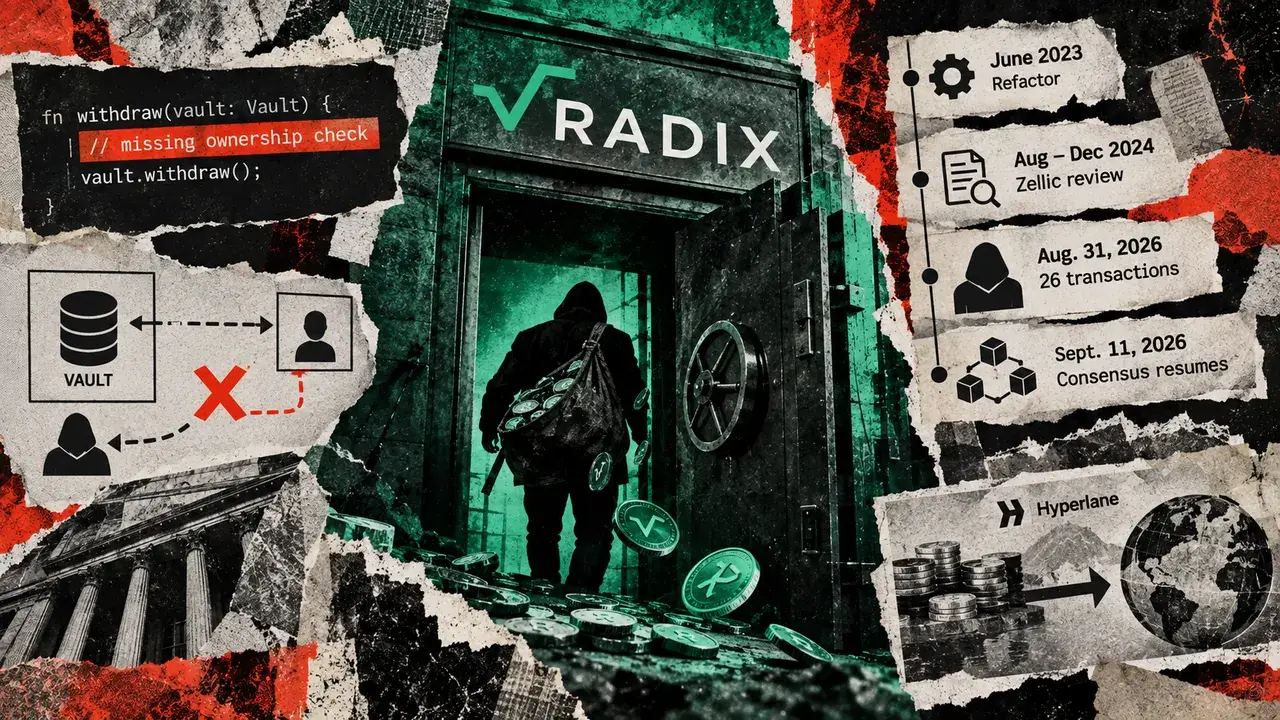
3-year-old bug triggers $1.3 million drain and forces 10-day blockchain halt
A routine Radix code refactor created a vault flaw that enabled a roughly $1.3 million theft and later forced validators to halt t...
Fake Claude trading bot tutorials drain $517K from 224 crypto users
The rise of AI-driven scams highlights the urgent need for enhanced user education and robust security measures in the crypto spac...

S&P Global Agrees To Acquire Smart Contract Security Firm OpenZeppelin
TL;DR S&P Global has agreed to acquire OpenZeppelin. OpenZeppelin is one of the best-known smart contract security and auditing fi...
Why keeping your private keys safe won’t always stop crypto theft
Almost 4,000 Bitcoin left Liquid's reserve on Sept. 6 through a withdrawal the network approved, even though the private keys used...