Malware Campaign Targets Crypto Wallets With Fake PDF Conversion Software
A new malware campaign is using fake PDF converters to sneak malicious PowerShell commands onto devices, putting crypto wallets at risk.
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
Why this matters
This cryptocurrency story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on DecryptRelated market context

WaterPlum Targets 30,000 Devices and Steals 7,000+ Crypto Wallet Records Worldwide
Key Takeaways: WaterPlum hacked over 30,000 devices in 100+ countries and accessed information from 7,000+ crypto wallets. Fake jo...
Fake IT Job Interviews Help North Korea Steal Millions in Crypto
A North Korean state-backed hacker group infected over 30,000 computers across 100 countries with malware that stole millions of d...
BitGo rolls out quantum-risk management tools to shield institutional Bitcoin wallets
BitGo's quantum-risk tools enhance Bitcoin security, potentially setting a new standard for institutional crypto custody amid evol...
Slowmist Warns Darksword iOS Exploit Targets Crypto Wallet Keys
23pds, Chief Information Security Officer at Slowmist, reported the evolution of this exploit, which, due to the combination of se...
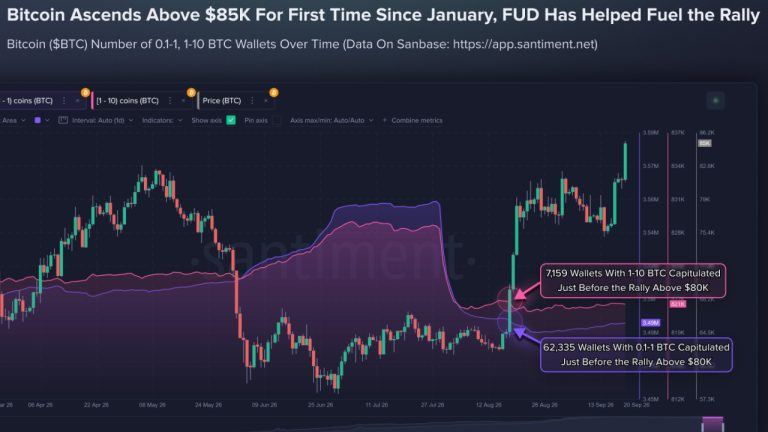
Smaller Bitcoin Holders Sold Before $85K Rally as 69,494 Wallets Exit
Bitcoin climbed above $85,000 after 69,494 wallets disappeared from two smaller-holder balance groups during the July-August downt...
SparkLend absorbs 88,320 ETH from tracked whale wallets as big money bets on conservative DeFi
Whale investments in SparkLend highlight a shift towards safer DeFi options, potentially influencing future risk management and pl...