BREAKING: Sushi DeFi Security Breach: CTO Sounds Alarm, SUSHI Price Drops 4%
In a significant blow to the decentralized finance (DeFi) sector, the Sushi DeFi protocol has fallen victim to its second exploit this year. The protocol’s Chief Technology Officer (CTO), Matthew Lilley, has issued a sta...
Archive context
Older archive item. Useful for background and entity history, but not a fresh market-moving signal.
In a significant blow to the decentralized finance (DeFi) sector, the Sushi DeFi protocol has fallen victim to its second exploit this year.
The protocol’s Chief Technology Officer (CTO), Matthew Lilley, has issued a stark warning to users, advising them to refrain from using any decentralized applications (dApps) until further notice.
Sushi And Zapper Frontends CompromisedThe latest breach has prompted concerns about the security and integrity of the Sushi DeFi protocol and other associated dApps. According to Lilley, a widely-used web3 connector has been compromised, allowing malicious code injection that affects numerous dApps.
Specifically, dApps that use the LedgerHQ/connect-kit, a dApp that allows users to connect other dApps to their Ledger hardware wallets, are considered vulnerable. Notably, Lilley’s warning underscores the severity of the situation, emphasizing that this is not an isolated attack, but a large-scale assault targeting multiple dApps.
Further investigation by security experts has revealed a potential supply chain attack on the ledger connect kit. The attacker allegedly successfully injected a wallet-draining payload into the popular Node Package Manager (NPM), impacting several prominent dApps, including Hey and others.
Additionally, it has been discovered that the Zapper and Sushi frontends have been hijacked, exacerbating the scope of the breach.
Slowmist, a module of Ledger, further confirmed that their system was hijacked and tampered with during the supply chain attack. This compromised the integrity of the ledgerhq/connect-kit library, which is relied upon by many dApps.
As a result, users are urged to exercise caution when conducting any dApp-related operations and to scrutinize requests for wallet information that may appear unexpected.
Malicious Connect Kit Neutralized?In an official statement, Ledger has confirmed the identification and removal of a malicious version of the Ledger Connect Kit. The company assures users that their Ledger devices and Ledger Live remain uncompromised.
The company stated that a genuine version of the Connect Kit is currently being pushed to replace the malicious file. Ledger advises users to refrain from interacting with any dApps at the moment for their safety.
The company pledges to provide updates as the situation develops, ensuring users stay informed about the ongoing efforts to address the security breach.
SUSHI’s Uptrend Threatened By Exploit FalloutIn light of recent events affecting the Sushi DeFi protocol, its native token, SUSHI, has experienced a decline of over 4% within the past hour, reaching a low of $1.590.
Before the exploit, SUSHI had been exhibiting a notable uptrend structure on its 1-day chart, marked by higher highs and higher lows. However, with the loss of its crucial support level at $1.961, there is a potential invalidation of the previously established uptrend.
The uncertainty surrounding the protocol’s native token raises the possibility of further downside in SUSHI’s price action. If a sustained downtrend continues, the next significant support level for SUSHI is located at $1.084.
Featured image from Shutterstock, chart from TradingView.com
Why this matters
This security story adds another data point to the current market tape and is useful when read alongside nearby source coverage.
Original source
Read on NewsBTCRelated market context
U.S. Targets $1.2 Billion From Binance Hack—Where Is the Rest?
The Binance hack recovery has reached a significant milestone: U.S. authorities say more than $1.2 billion in stolen cryptocurrenc...

Safepal Hardware Wallet Users Receive Fake Security Alerts in the Mail
Safepal customers in Italy are reportedly being targeted by a sophisticated phishing campaign involving fraudulent letters contain...
Chainlink and Moody’s Complete Testnet Pilot for Cross-Chain Credit Ratings
TL;DR: Chainlink and Moody's Ratings completed a cross-chain distribution pilot using test data. It ran on testnets and did not pu...
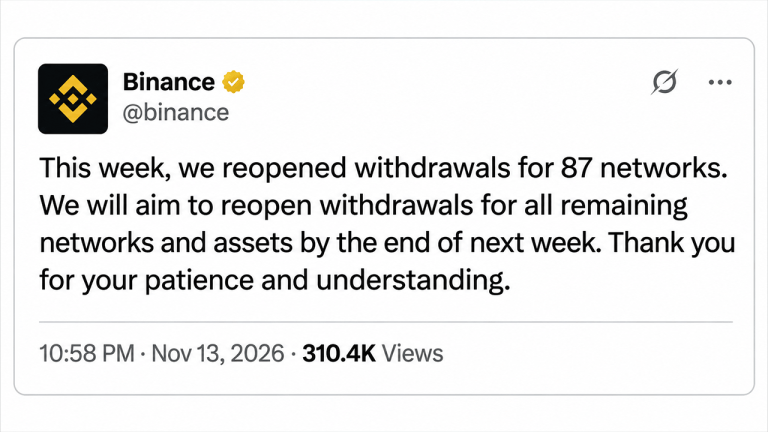
Binance Reopens 87 Networks Following Historic $6.3 Billion Breach
Binance has reopened withdrawals across 87 blockchain networks as the cryptocurrency exchange continues recovering from its devast...
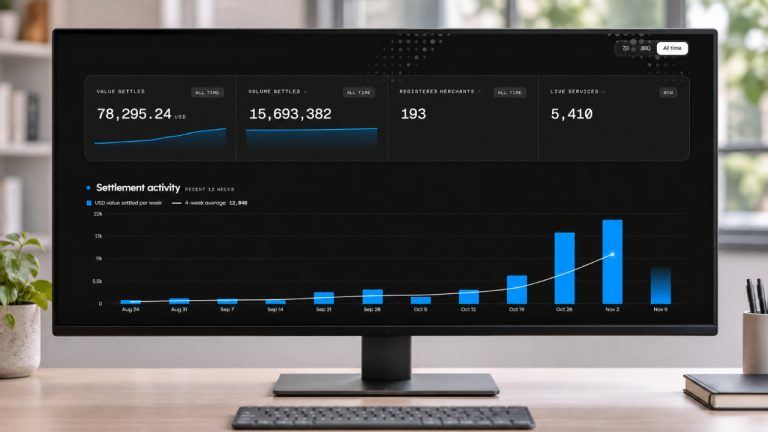
XRP Ledger AI Services Exceed 5,400 Across More Than 190 Merchants
AI agents can now purchase more than 5,400 services on the XRP Ledger, according to t54. Its expanding directory connects automate...

Bitget Hacker Moves $78.6M in Bitcoin, Sends $63.4M Through 66 CoinJoin Transactions
Key Takeaways: In six days, Arkham recorded a loss of 1,052.34 BTC valued at $78.61 million from wallets that were identified as b...